
Endpoint Detection and Response (EDR) Selling to the CISO — 60-Min Training
 Curated byKory White · Fractional CRO · Maryland
 PULSEKNOWLEDGE LIBRARY
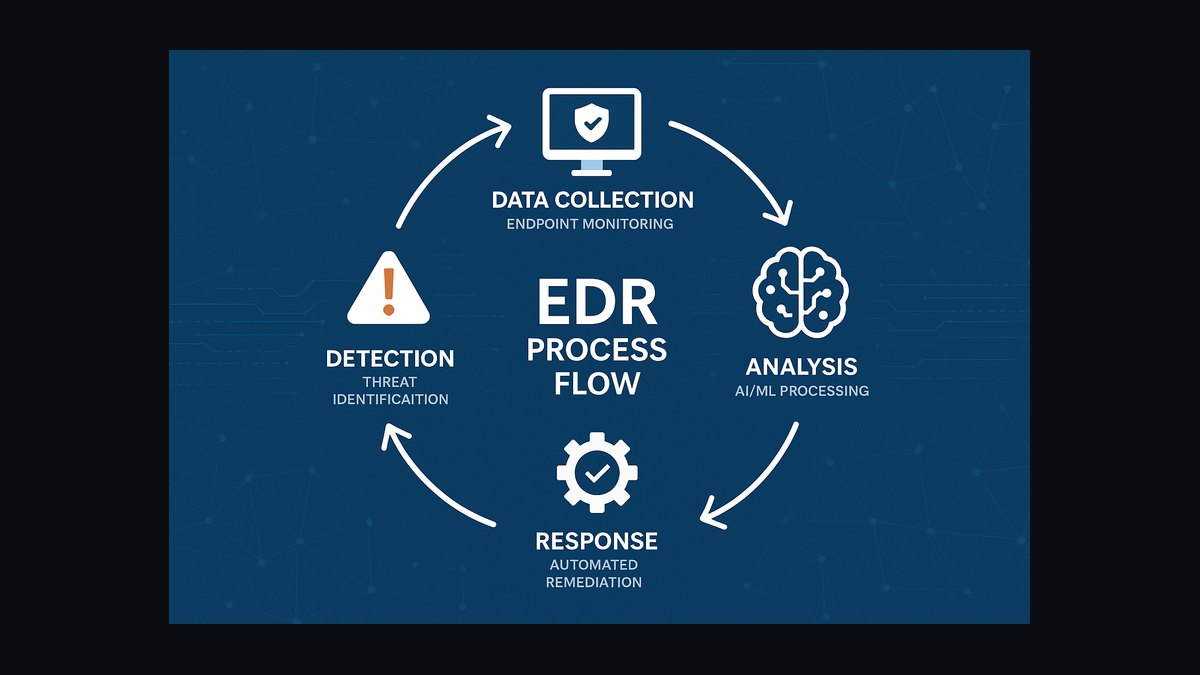
Selling EDR to a CISO means winning three buyers at once: the CISO judges detection efficacy, the SOC manager judges alert noise and analyst hours, and IT operations judges agent footprint. Anchor discovery to those three scoreboards, prove them on production endpoints, and price against the incumbent's real gaps.
The two paths a 60-minute EDR training can take
Every enablement session on endpoint security eventually splits into two designs, and the choice determines whether reps leave with a repeatable motion or a vocabulary list.
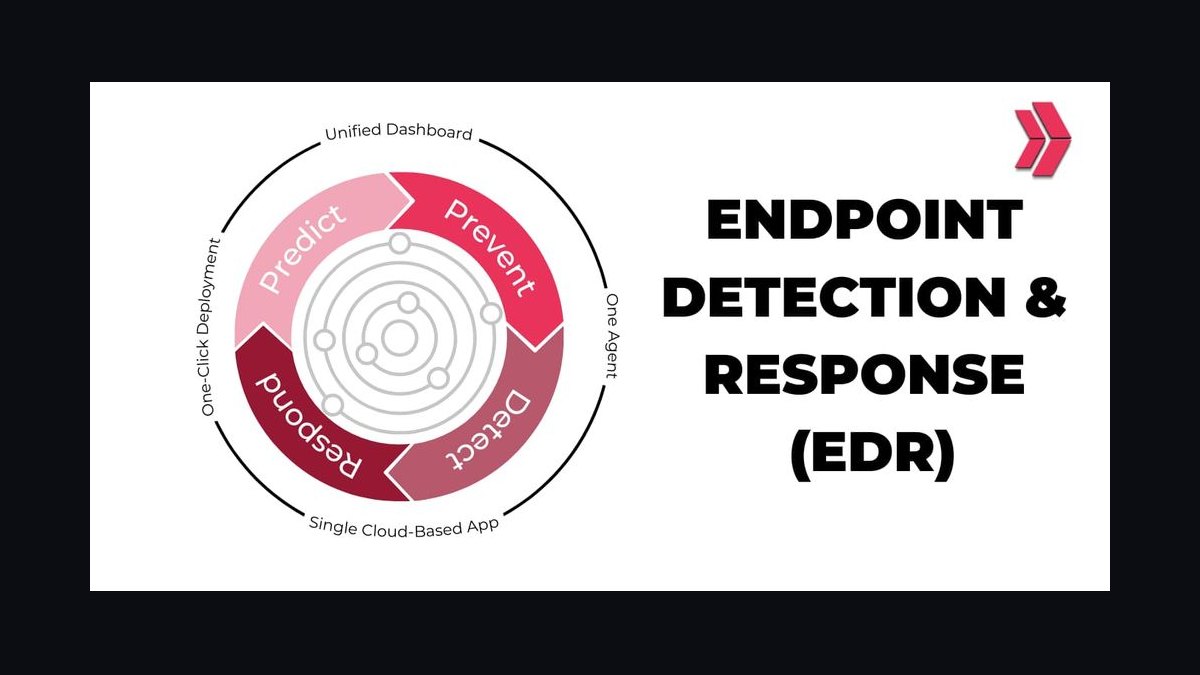
Path A — the product-fluency session. Sixty minutes spent on architecture: how the sensor collects telemetry, what the behavioral engine does with process trees, how cloud analytics correlate across the fleet, what the response actions are (network containment, process kill, file quarantine, rollback where supported). Reps leave able to describe the product. The implicit theory is that a rep who understands the technology will figure out the conversation.
Path B — the buyer-scoreboard session. Sixty minutes spent on who decides, what each decider is measured on, and how to run a proof that speaks to all three at once. Product detail appears only as ammunition for a specific objection. Reps leave with a discovery script, a proof-of-concept design, an incumbent-displacement play, and a renewal trap-set.
The honest trade-off: Path A is easier to build and easier to grade. You can quiz reps on features. It also fails predictably in EDR specifically, because the category's losses are rarely technical ignorance — they're structural. A rep who can explain kernel-level telemetry but walks into a room with only the SOC manager present, and no CISO, has already lost the budget conversation. A rep who nails the demo but never asks about the incumbent's contract end date lands a technical win and a "revisit next year."
Path B is harder to build because it requires you to have opinions about your own competitive position, and it requires managers to inspect discovery notes rather than demo recordings. But it's the design that matches the category. The recommendation for a single 60-minute block is Path B with Path A material pushed to pre-work: send the architecture deck 48 hours ahead, spend the live hour on the buying motion.
There's a third design worth naming to reject it: the "objection-handling drill" session, where reps rehearse rebuttals to a list of stock objections. It feels productive and produces reps who argue. In EDR the winning move on the hardest objection — the bundled Microsoft Defender for Endpoint question — is not a rebuttal at all. It's a scoping question about which operating systems and which endpoint tiers the customer actually needs covered. Drilling rebuttals trains reps to talk past that.
The three buyers and what each one is actually graded on
The single most useful thing a 60-minute session can install is that "the CISO" is not one buyer. Endpoint Detection and Response purchases are typically co-owned, and the three roles want different proof.
The CISO owns budget and risk. Their scoreboard is detection efficacy and defensibility — can they stand in front of the board or an auditor and explain why this control was chosen. This is why public evaluation results matter disproportionately in this category. MITRE Engenuity's ATT&CK Evaluations are the reference point most enterprise security teams cite, because the methodology is public and vendor-neutral: adversary emulation runs against each product, and the results report visibility and analytic detection coverage per technique. A rep who cannot discuss their own product's evaluation results — including the weak spots — reads as either uninformed or evasive. Both cost credibility with this buyer in the first ten minutes.
The SOC manager owns the analysts. Their scoreboard is noise and time. Every false positive is a queue item that consumes analyst attention, and analyst burnout is a hiring problem, which makes it a budget problem. The questions that land with this buyer are operational: how many alerts per day per thousand endpoints, what percentage get auto-resolved, how long does triage take, what does the investigation timeline look like when an analyst opens an alert at 2am. If your product genuinely reduces alert volume or shortens investigation, this buyer becomes your internal champion — and the SOC manager is usually the one who writes the renewal recommendation.
The IT operations lead owns the endpoints and, critically, owns the pain when something breaks. Their scoreboard is agent footprint, deployment friction, and stability. CPU and memory consumption on a developer's laptop, whether installation requires a reboot, whether the agent conflicts with other software, how updates roll out and whether they can be staged. This buyer rarely champions a purchase but very often kills one. The July 2024 CrowdStrike incident — a faulty content update that caused widespread Windows crashes — permanently raised this buyer's standing in EDR evaluations. Expect questions about update staging, rollout rings, and rollback that would have been unusual before it.
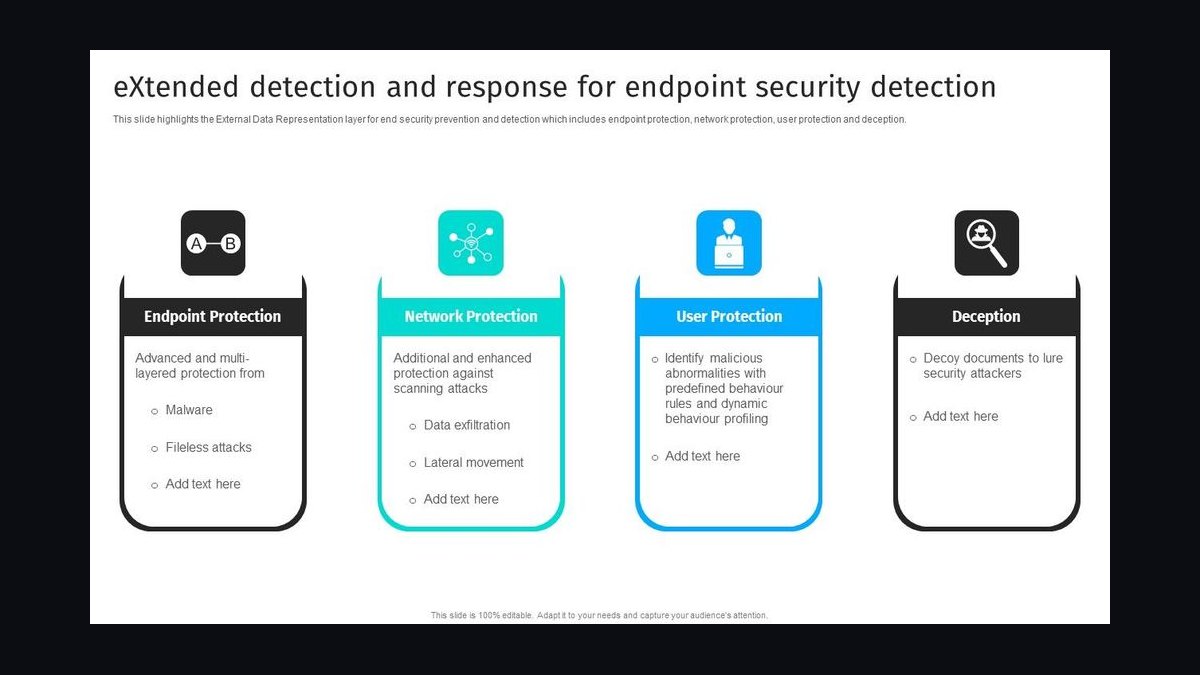
The training implication: teach reps that a meeting missing one of the three is not a meeting worth running at full effort. Reschedule, or at minimum run it as an information-gathering call and explicitly ask who else needs to be in the room for the real one.
How to decide which motion a given deal needs
Not every EDR deal runs the same play. The 60-minute session should give reps a branching decision rather than one script.
The branch points that matter: is there an incumbent third-party EDR under contract, is the customer running Microsoft Defender for Endpoint as their de facto control, and is the driver a compliance deadline or an actual incident. Each combination changes the sequencing.
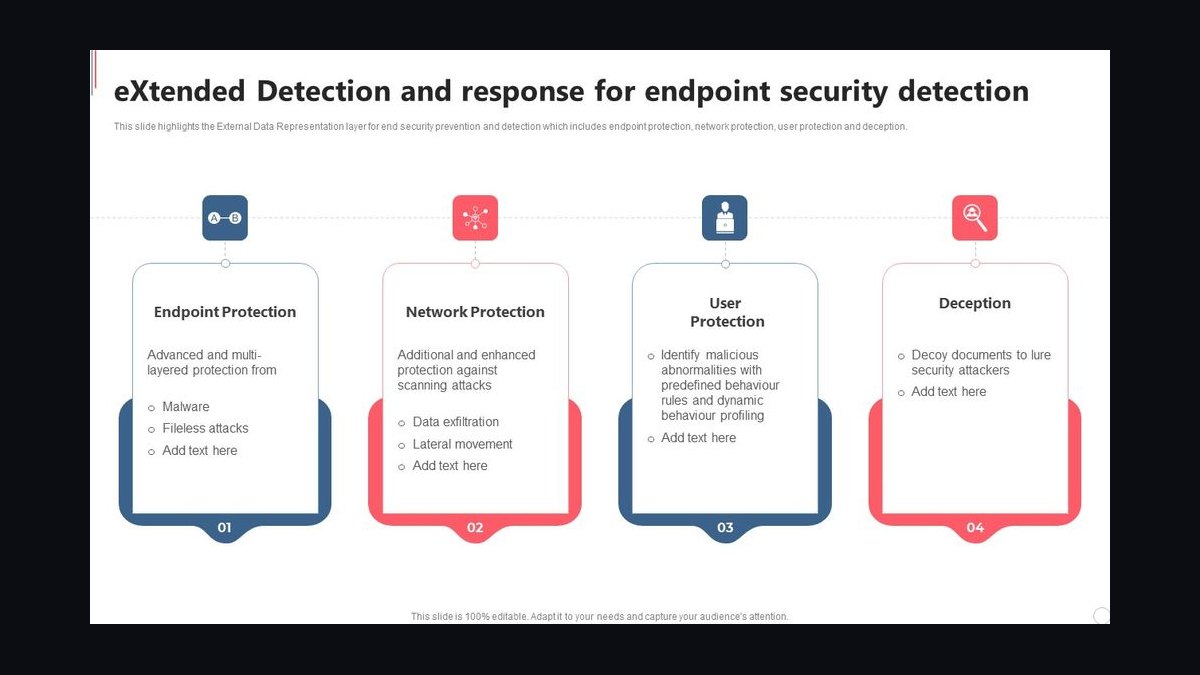
Walk the room through each branch with a real account name from their own pipeline. The exercise that makes this stick: hand each rep three of their own open opportunities and have them place each one on the diagram, out loud, with the evidence for the placement. Reps who cannot place a deal have a discovery gap, and that gap is the actionable coaching output of the whole session.
The disqualification branch is the one managers under-coach. If a customer runs a homogeneous Windows fleet, has an E5 license, has no dedicated SOC, and is under no compliance pressure, the bundled option is often genuinely adequate and the deal will consume two quarters before dying in procurement. Teaching reps to name that early is worth more than teaching them one more rebuttal.
The discovery block: seven questions and the numbers behind them
Fifteen minutes of the session goes to a discovery sequence reps can run in a real 45-minute call. Each question exists to surface a number that later anchors the proof and the pricing.
Current deployment and coverage. "Walk me through what's protecting endpoints today — which product, what percentage of the estate, and which operating systems are on it." The gap between "we have EDR" and "EDR is deployed on 100% of endpoints" is where most real risk lives. Unmanaged devices, contractor laptops, Linux servers, and legacy systems are common blind spots. Get the percentage, not the vendor name.
Operating system mix. Ask for the split across Windows, macOS, Linux, and any specialized systems. This question does more competitive work than any rebuttal, because cross-platform depth is where bundled offerings and third-party products diverge most concretely, and the answer is a fact the customer supplies rather than a claim you assert.
Alert volume and disposition. "How many alerts reach an analyst per day, and what fraction close as false positives?" Customers often haven't measured this precisely, which is itself useful — offering to measure it during a proof is a low-friction way to get deployed. If they have measured it, the number becomes your before-and-after baseline.
Mean time to investigate. How long from alert to disposition. This is the metric that converts to headcount math, which is the metric that converts to budget.
Detection validation practice. "Do you run adversary simulation against your current control, and with what?" Open-source and commercial options exist — Atomic Red Team and MITRE Caldera are the widely used open-source projects, and there are commercial breach-and-attack-simulation platforms. If the customer already runs simulations, you have an objective scoreboard available for the proof. If they don't, offering to run one is often the most differentiated thing in your proposal.
Managed detection posture. Whether they run the tooling with their own analysts, with a managed detection and response provider, or a hybrid. This changes who your economic buyer is and whether you're selling software, service, or both. Several major vendors offer a managed tier alongside the platform, and whether the customer wants one materially changes deal size and the shape of the proof.
Contract timing and extraction friction. Renewal date, notice period, auto-renewal clauses, and whether there are multi-year commitments with remaining term. A rep who learns this in call one can sequence a whole year correctly; a rep who learns it in month five has already burned the cycle.
Coach reps to write these seven answers into the opportunity record as numbers, not prose. The manager inspection is trivial: are there seven numbers, and are they specific.
Designing a proof of concept that survives contact with production
The proof is where EDR deals are won and where they most often quietly die. Fifteen minutes of the session covers design.
Scope it to a representative sample, not a token one. A handful of clean test VMs proves nothing about noise, because noise is a function of real user behavior — developers compiling code, admins running scripts, marketing installing odd browser extensions. Push for a sample that includes each major operating system, at least one developer machine, at least one server workload, and at least one executive laptop. Representativeness matters more than raw count.
Let the customer's team do the deployment. If your sales engineer installs everything, you've proven that a specialist can deploy it. Have the customer's endpoint management team push the agent through their own tooling. Deployment friction discovered during a proof is recoverable; discovered during rollout, it becomes a churn story.
Run adversary simulation, and publish the misses. Execute a defined set of techniques mapped to ATT&CK tactics and show what was detected, what was blocked, what was only visible in telemetry, and what was missed. Publishing the misses is counterintuitive and it is the single highest-trust move available in this category. Security buyers assume a vendor-run demo is rigged; a vendor who volunteers their gaps is the one who gets believed on their strengths.
Measure noise for long enough to matter. Alert volume over three days tells you nothing — the first days are dominated by tuning. Thirty days is the shortest window that produces a defensible false-positive rate. If the customer will only give you two weeks, say explicitly that the noise number will be directional and set the comparison up honestly rather than cherry-picking a quiet week.
Measure footprint on the machines that complain. Pull CPU and memory numbers from the developer laptop and the busiest server, not the average. The IT operations lead's objection will come from the loudest user, so pre-empt it with that user's data.
Book the scorecard call at kickoff. Set the review meeting date before the proof starts, with all three buyers invited. A proof without a scheduled decision meeting becomes a permanent free trial.
Failure modes worth naming explicitly in the session: proofs that run without a written success criteria document, proofs where the sales engineer tunes the configuration without telling the customer what was tuned, proofs extended a second time (an extension is a signal to re-qualify, not to try harder), and proofs where the SOC analysts who will actually use the product were never given hands-on access.
Handling the bundled-Defender objection without arguing
This deserves its own segment because it is the most common and most mishandled moment in EDR sales.
The objection arrives as: "Defender for Endpoint is included in our E5 licensing — why would we pay separately?" Reps instinctively argue product superiority. That's the losing move, because it invites a feature-parity debate the customer will resolve by defaulting to the thing they already own.
The winning move is to convert the objection into a scoping question. Microsoft's own documentation is explicit that Defender for Endpoint's capabilities differ across platforms and across licensing plans — there are distinct plan tiers with different feature sets, and the depth of support varies by operating system. So the reply is not "we're better," it's: "Which endpoints, specifically? Let's map your estate against what your plan covers."
Then walk the estate:
- Windows desktop and server fleet. Be honest: this is the strongest case for the bundled option. If the customer is Windows-only with an appropriate plan tier, say so. Trying to win here on features damages you everywhere else.
- macOS and Linux. Support exists but the capability and management experience differ. Have the customer's own team confirm what they see rather than asserting it.
- Mobile and unmanaged devices. Ask what's covered today and what isn't.
- Specialized systems — point-of-sale, industrial control, embedded, legacy operating systems past end of support. These are frequently uncovered and frequently the highest-risk assets in the environment.
- SOC workflow fit. If the security team's existing tooling and processes are built around a different console or SIEM, the integration and workflow cost is a real, quantifiable factor.
The second half of the play is the licensing-tier question: which plan do they actually hold, does every user carry it, and does that entitlement extend to servers and to every workload they need protected. Customers frequently believe coverage is universal when the entitlement is narrower than assumed. That's not a gotcha to spring — it's a question to ask so the customer discovers it themselves.
Where the honest answer is "the bundled option covers this segment adequately," the strong position is a tiered one: bundled coverage for the low-risk majority, your product on the tier-1 estate where detection depth and cross-platform coverage matter. That proposal is smaller than a full displacement and it closes, and it puts you inside the account for the next renewal.
Pricing, procurement, and the sequencing that protects margin
Ten minutes on commercial mechanics, because reps lose margin on process, not on price.
Understand the unit. EDR pricing is typically per-endpoint or per-user, per-month or annually, with tiering by feature set — a base detection tier, a fuller tier adding threat hunting or additional telemetry, and a managed service tier where the vendor's analysts operate it. Vendors publish some entry pricing and negotiate enterprise deals, so the list number a customer quotes back to you is rarely the number that matters. What matters is the fully-scoped annual figure against the endpoint count they'll actually deploy.
Scope honestly on endpoint count. Over-scoping to inflate the deal is the most common self-inflicted wound in this category. If you price 12,000 endpoints and they deploy 7,000, the year-two conversation opens with the customer feeling overcharged. Price the real deployable estate, and structure expansion as a pre-agreed rate card so growth is frictionless rather than a new negotiation.
Trade discount for term and for something you need. Multi-year commitments justify discount, and the discount should buy you something beyond term — a reference call, a case study right, a joint webinar, an executive relationship. Discounting for term alone teaches the customer that discount is available for asking.
Refuse the procurement-solo meeting. Once procurement is negotiating without the CISO or the SOC manager present, the conversation is purely price, because procurement has no access to the value side of the equation. The reasonable position, stated politely and early: "Happy to work through terms — I need the security team in the room for anything that changes scope, because scope changes are risk decisions, not commercial ones."
Watch for the mid-cycle displacement structure. When a customer is under contract with an incumbent but wants to move, there are two workable shapes: a non-overlapping deployment covering estate the incumbent doesn't (different operating systems, a specific business unit), or a co-term arrangement where you absorb some overlap in exchange for a longer term. Both are legitimate. What's not legitimate is pretending the overlap cost doesn't exist — the customer's finance team will find it.
Landmines to name out loud in the session: auto-renewal clauses in the incumbent's contract that quietly foreclose a switch; data retention pricing that scales separately from endpoint count and surprises the customer in month four; professional services scoped too thin so onboarding stalls; and any commitment about detection performance made verbally by a rep that the contract doesn't reflect.
Implementation, onboarding, and setting up the renewal at month one
The last segment covers what happens after signature, because in security software the renewal decision is largely made in the first ninety days.
Rollout rings, not big bang. Start with the IT team's own machines, then a friendly business unit, then general population. Each ring is a chance to catch a software conflict before it becomes an outage story. This sequencing is also what reassures the IT operations lead, who has been the most nervous buyer since the industry's high-profile update failure.
Schedule the tuning pass. Out-of-box alert policy is never right for a specific environment. Book a dedicated tuning session at week four with the SOC manager, and document every suppression rule and exclusion with a reason. Undocumented exclusions are how detection quietly degrades over two years, and an exclusion nobody remembers is a genuine security hole.
Integrate into the workflow the analysts already use. If alerts don't reach the ticketing and SIEM systems the team lives in, the product becomes a second console nobody opens. Treat integration as a launch requirement, not a phase two.
Set the ninety-day scorecard at kickoff. Three numbers, agreed in writing before deployment: coverage percentage, alert volume per analyst per day, and adversary-simulation detection coverage. Review them at day 90 with the same three buyers who bought. This is what makes the renewal a formality rather than a re-sell — the scoreboard is already built and already familiar.
Keep running simulations. A control validated once at purchase and never again is a control whose actual state nobody knows. Quarterly simulation, with results shown in the review, gives the CISO the defensibility they bought and gives you a recurring reason to be in the room.
Name the expansion path early. Additional endpoint tiers, added operating systems, a managed tier, or adjacent telemetry sources. If the expansion rate card was set at the original contract, expansion is an email. If it wasn't, it's a new negotiation at a moment when you have less leverage than you did at signature.
Related questions
How long should an EDR proof of concept run?
Thirty days minimum if false-positive rate is a decision criterion — shorter windows are dominated by initial tuning noise. Sixty days is common for large enterprise evaluations. Set the decision meeting date at kickoff regardless of length.
Who should own the EDR relationship after the sale?
The customer success or account team owns it, but the SOC manager is the person whose experience determines renewal. Build a direct, recurring channel to that role — not just to the CISO — within the first thirty days.
Should reps memorize MITRE evaluation results?
They should know their own product's results including weaknesses, and be able to explain the methodology. Reciting competitor scores without context reads as spin; discussing your own gaps honestly reads as credible.
What disqualifies an EDR opportunity early?
A homogeneous Windows fleet with adequate bundled licensing, no dedicated security operations function, no compliance driver, and no recent incident. That combination usually consumes two quarters and closes lost.
How do you sell into an account mid-contract with a competitor?
Deploy on estate the incumbent doesn't cover — different operating systems, a specific business unit, or unmanaged devices — and build a measured comparison for the renewal window. Learn the notice period first.
FAQ
What's the right length for an EDR sales training block?
Sixty minutes works if architecture material is sent as pre-work and the live hour covers buyers, discovery, proof design, the bundled-competition objection, and commercial sequencing. Trying to teach product architecture and sales motion in the same hour produces reps who are shallow on both.
Should sellers position against Microsoft Defender for Endpoint or alongside it?
Both, depending on the estate. Concede the segments where the bundled option is genuinely adequate and win on cross-platform coverage, specialized systems, and SOC workflow fit. A tiered proposal closes far more often than an attempted full displacement in a Microsoft-committed account.
How do you prove noise reduction without a long trial?
You can't prove it rigorously in under thirty days, so be explicit about that. Offer a directional two-week measurement with the caveat stated up front, or propose a longer proof. Cherry-picking a quiet week is the fastest way to lose a security buyer's trust permanently.
What role does adversary simulation play in the sales cycle?
It converts a subjective product debate into an objective scoreboard. Open-source projects like Atomic Red Team and MITRE Caldera are widely used, and running a defined technique set during the proof — then publishing the misses alongside the detections — builds more credibility than any deck.
Why does IT operations matter so much in an EDR deal?
Because they carry the risk when an agent destabilizes production endpoints. Since the industry's high-profile faulty-update incident, questions about update staging, rollout rings, and rollback capability have become standard. This buyer rarely champions, but routinely vetoes.
When should the renewal conversation actually start?
At kickoff. Agree three success metrics in writing, review them at day 90, and keep them in every quarterly review. By month nine the renewal is a confirmation of a known scoreboard rather than a fresh evaluation of an unmeasured control.
Sources
- https://attackevals.mitre-engenuity.org/
- https://attack.mitre.org/
- https://learn.microsoft.com/en-us/defender-endpoint/microsoft-defender-endpoint
- https://learn.microsoft.com/en-us/defender-endpoint/defender-endpoint-plan-1-2
- https://www.cisa.gov/news-events/alerts
- https://atomicredteam.io/
- https://caldera.mitre.org/
- https://csrc.nist.gov/pubs/sp/800/61/r2/final
- https://www.sans.org/white-papers/
- https://www.gartner.com/en/information-technology/glossary/endpoint-detection-and-response-edr-solutions
Related on PULSE
- [MDR (Managed Detection and Response) Services Selling to Mid-Market — 60-Min Training](/knowledge/st385)
- [Mobile Threat Defense (MTD) Selling to the CISO and Endpoint Management Lead — 60-Min Training](/knowledge/st403)
- [Incident Response (IR) Retainer Selling to the CISO and General Counsel — 60-Min Training](/knowledge/st397)
- [Cybersecurity Incident Response Engagement Selling — 60-Min Training](/knowledge/st367)
- [AI Safety / Red Team Services Selling to the CISO — 60-Min Training](/knowledge/st412)
- [Post-Quantum Cryptography (PQC) Crypto-Agility Selling to the CISO and Chief Cryptographer — 60-Min Training](/knowledge/st406)
This page will be disappearing soon. Save it to your device for $1 — or read it free while it is here.
@Kory-White- · if Venmo asks, the last 4 of my number are 2012
 sales-trainingHow do you train a sales team in Staffing & Recruiting in 2027?
 sales-trainingHow do you train a sales team in Consumer Products / CPG in 2027?
 sales-trainingHow do you train a sales team in Events & Venues in 2027?
 sales-trainingHow do you train a sales team in Financial Services in 2027?
 sales-trainingHow do you train a sales team in Solar & Renewables in 2027?
 sales-trainingHow do you train a sales team in SaaS & Software in 2027?
 sales-trainingHow do you train a sales team in Sports & Entertainment in 2027?
 sales-trainingHow do you train a sales team in Mortgage & Lending in 2027?
 sales-trainingHow do you train a sales team in Cleaning & Facilities in 2027?
 sales-trainingTop 10 sales training budget allocation strategies in 2027