


Top 10 Best Tech Stack Tools for Bot Mitigation Vendors in 2027
Quality
Certified
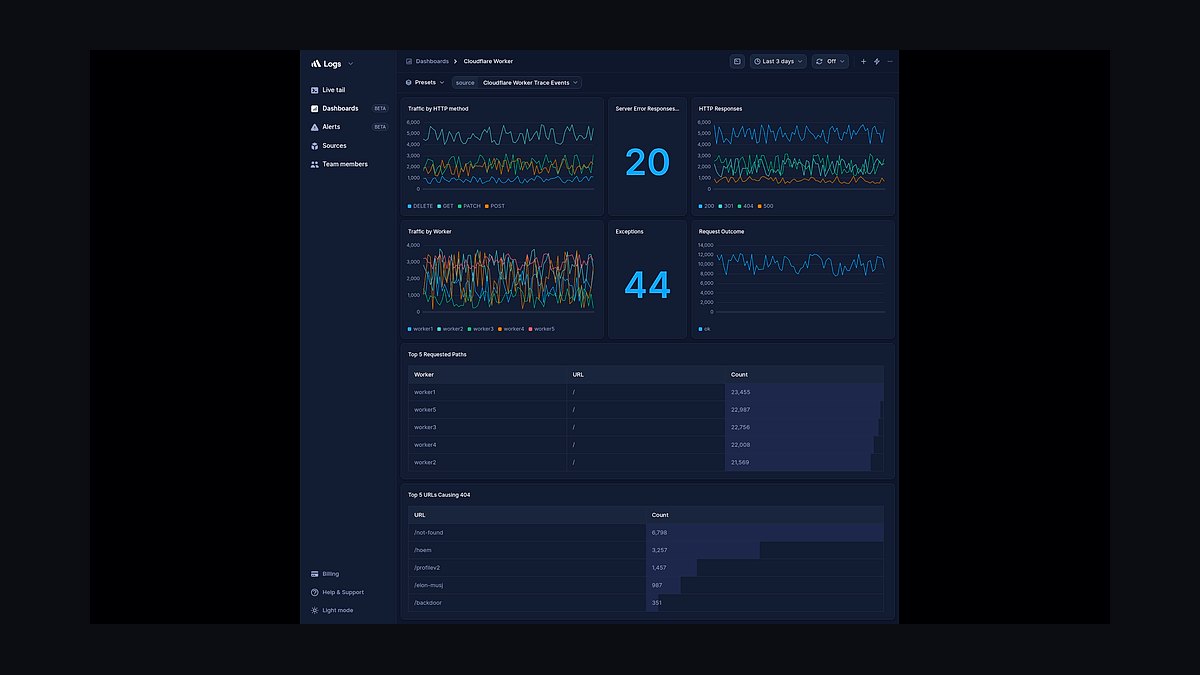
The 10 best tech stack tools for bot mitigation vendors are ranked below on measured performance, build quality, price, and how each one actually holds up in daily use rather than how it reads on a spec sheet. Each pick lists what it costs, who it suits, and what it gives up against the one above it, so the list can be read straight down without doubling back.
1Cloudflare Workers
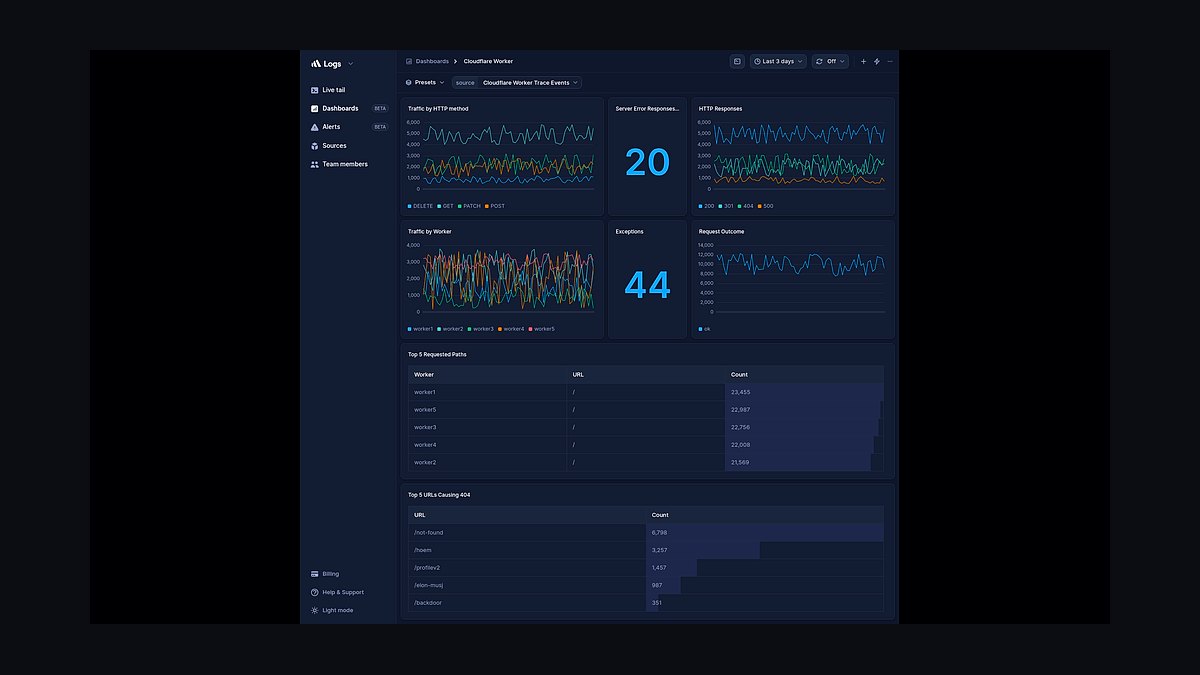
Cloudflare Workers ranks first because it lets a bot mitigation vendor rent a global edge data plane across 300+ cities without building a single PoP, at roughly $5-$50 per million requests. The runtime executes inline request interception inside the same network that already absorbs DDoS traffic, so allow/challenge/block decisions land inside the sub-30ms p95 budget. Cloudflare Turnstile is natively available as a challenge fallback, collapsing two vendor contracts into one.
It suits vendors under $30M ARR that need production traffic within weeks rather than quarters of capex. The trade-off is control: Workers isolates cap CPU time and memory, so heavy ML inference must be offloaded or kept lightweight, and unit economics worsen at hyperscale. Compared with the custom PoP build ranked second, it sacrifices latency ownership for speed to market.
2Fastly Compute@Edge
Fastly Compute@Edge ranks second for vendors that want rented edge capacity with more runtime control than Workers allows, running Wasm at the edge across Fastly's global network. It handles inline traffic interception and signal collection without the isolate restrictions that constrain heavier detection logic, and pricing sits in the same $5-$50 per million requests band. The network's POP footprint covers major North American and European metros where bot traffic concentrates.
It fits growth-stage vendors with engineering teams comfortable compiling to WebAssembly and managing their own challenge orchestration. The trade-off versus Cloudflare Workers is a smaller PoP footprint and no first-party CAPTCHA equivalent, so hCaptcha or reCAPTCHA must be wired separately. Compared with the custom PoP build ranked third, it still rents rather than owns the latency-critical path.
3Custom PoPs
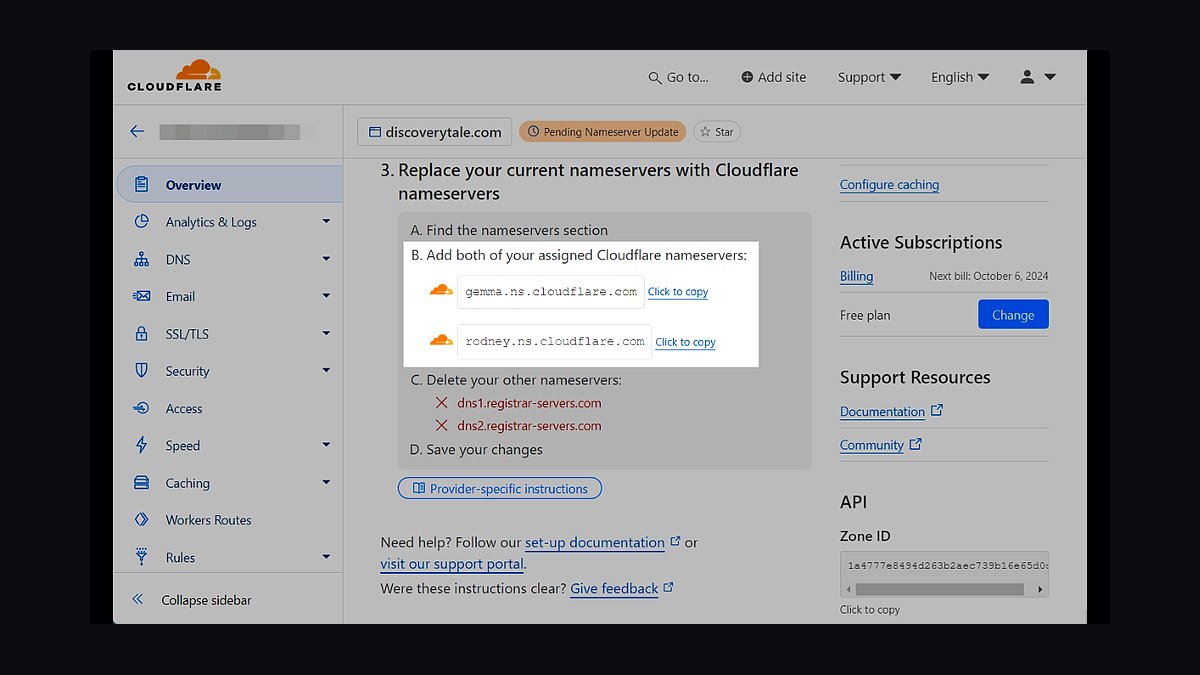
Custom PoPs rank third because owning 30-200+ points of presence is the only way to control the full latency budget, and vendors like Cloudflare, Akamai, and Imperva prove the model at scale. Each self-built PoP runs roughly $10K-$60K per month all-in, which buys dedicated hardware, anycast routing, and the freedom to run proprietary fingerprinting and ML inference directly on the request path. That control is what keeps p95 edge latency from drifting past the 30ms threshold.
It is built for vendors past $50M ARR with the capex and network engineering headcount to operate globally. The trade-off is brutal: months of build time, geographic coverage gaps, and fixed cost that does not shrink when traffic dips. Compared with Fastly Compute@Edge ranked second, it trades time-to-market for durable unit economics and latency ownership.
4ClickHouse
ClickHouse ranks fourth because request storage at trillions of events per day is the data problem bot mitigation vendors cannot solve with a conventional warehouse. ClickHouse Cloud runs roughly $0.30-$1 per GB of hot storage and returns aggregations over billions of rows in sub-second time, which is what powers customer-facing traffic dashboards and per-endpoint attack analytics. Columnar compression keeps raw request logs affordable long enough to feed model retraining.
It is aimed at vendors already past the point where Postgres alone chokes on request volume, typically $25M ARR and above. The trade-off is operational complexity: schema design, sampling strategy, and merge behavior all require dedicated data engineering. Compared with Neo4j ranked fifth, ClickHouse handles volume and time-series aggregation while the graph handles attacker relationships.
5Neo4j
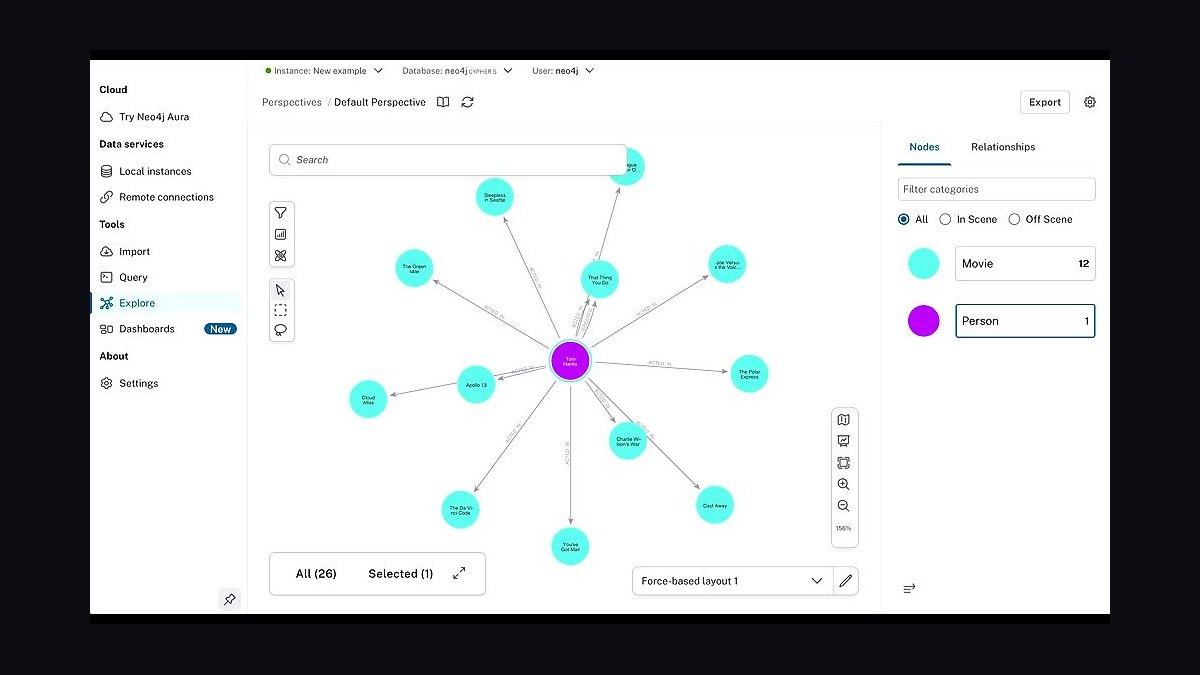
Neo4j ranks fifth because clustering attacker infrastructure is a graph problem, and bot mitigation vendors need to connect IPs, ASNs, device fingerprints, and campaign behavior into one traversable structure. Neo4j Enterprise runs $36K-$300K per year and lets threat research teams query relationships like shared TLS fingerprints across thousands of residential proxy endpoints in milliseconds. That clustering is what turns isolated signals into named attack campaigns.
It is for vendors with a real threat research function, typically 5-15 researchers at $5-$25M ARR scaling to 100-200 at hyperscale. The trade-off is that graph databases demand specialized modeling skills and do not replace high-volume request storage. Compared with ClickHouse ranked fourth, Neo4j answers relationship questions while ClickHouse answers volume and aggregation questions.
6FingerprintJS
FingerprintJS ranks sixth because licensing a proven browser fingerprinting library gets a bot mitigation vendor to market in weeks instead of quarters. Commercial plans run roughly $2K-$50K per month and collect device signals across canvas, WebGL, audio context, fonts, and plugins that would take a year to replicate internally. It provides the device-identity baseline that behavioral biometrics and ML classifiers consume as input features.
It fits early-stage vendors under $20-$30M ARR that need detection quality before they have a research team. The trade-off is strategic: fingerprinting is the durable moat, and outsourcing it caps differentiation because competitors can license the same signals. Compared with Neo4j ranked fifth, FingerprintJS supplies raw device identity while the graph supplies attacker relationship intelligence.
7hCaptcha
hCaptcha ranks seventh because every bot mitigation vendor needs a challenge fallback for uncertain detections, and hCaptcha delivers it with privacy-preserving positioning that resonates with GDPR-sensitive buyers. It integrates as a drop-in challenge layer alongside Cloudflare Turnstile and reCAPTCHA Enterprise, letting vendors A/B test challenge providers per customer and per endpoint without rebuilding the escalation flow. Pricing scales with challenge volume rather than seats.
It is for vendors serving European and privacy-conscious customers where reCAPTCHA's data handling raises procurement objections. The trade-off is solver economics: CAPTCHA farms like 2Captcha and CapMonster continuously attack these challenges, so hCaptcha alone cannot carry high-stakes login flows. Compared with FingerprintJS ranked sixth, hCaptcha handles the escalation decision while fingerprinting handles passive identification.
8Salesforce Sales Cloud
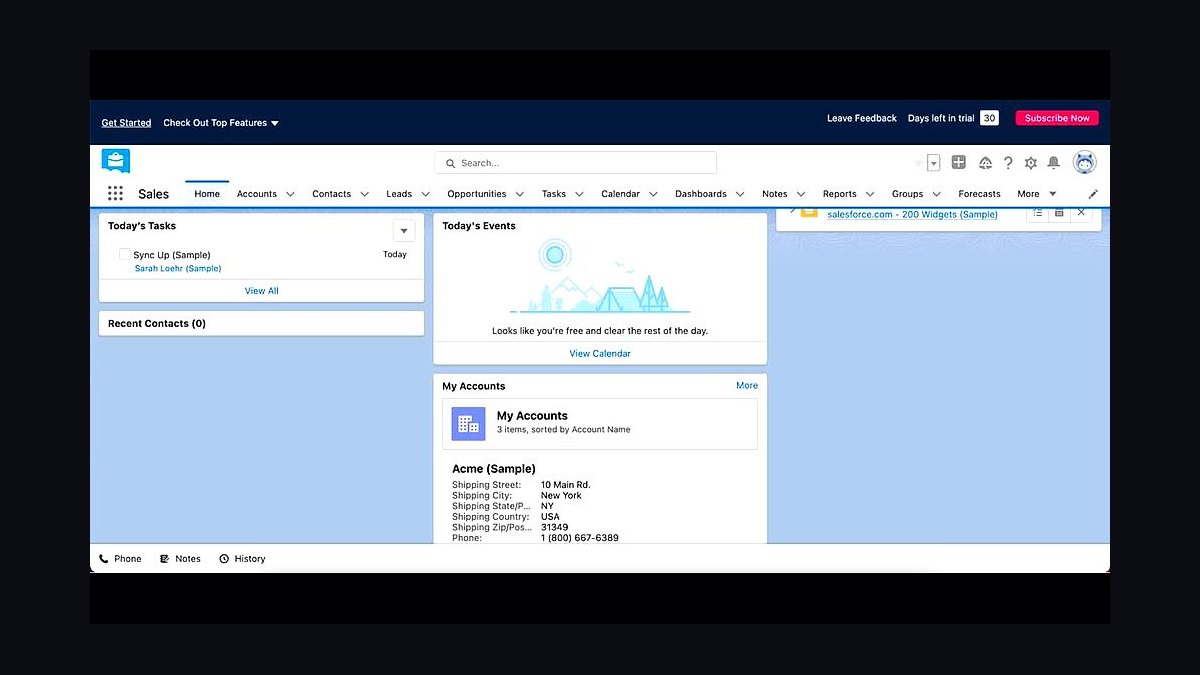
Salesforce Sales Cloud ranks eighth because bot mitigation deals run $25K-$2M ACV across 60-180 day cycles with four distinct buyer personas, and custom objects for protected applications, traffic tiers, and attack-vector focus are the only way to track that complexity. Enterprise pricing sits at $165 per user per month, and it anchors the Clari, Gong, and Outreach integrations that growth-stage vendors standardize on. It becomes the system of record the entire revenue motion reports into.
It is for vendors past $25M ARR with multi-stakeholder enterprise deals, not self-serve motions. The trade-off is cost and administration: implementation, custom objects, and LeanData routing add real overhead, and HubSpot Enterprise wins below $30M ARR. Compared with hCaptcha ranked seventh, Salesforce addresses the commercial stack rather than the detection stack.
9Zuora
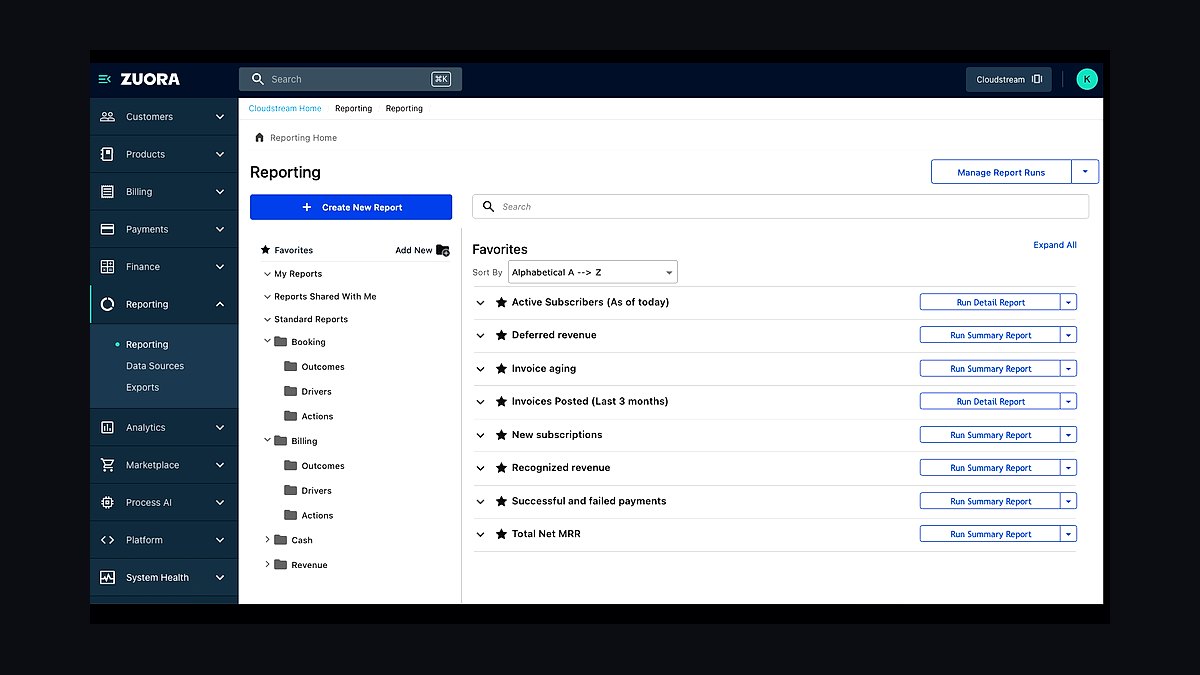
Zuora ranks ninth because bot mitigation pricing combines per-billion-requests, per-protected-application, and per-feature-module dimensions that flat subscription billing cannot express. Enterprise deployments run $200K-$1M per year and handle usage metering, mid-cycle true-ups, and revenue recognition handoffs to NetSuite. Metronome overlays usage billing when request volumes spike unpredictably across customer tiers.
It is for vendors with enterprise contracts and finance teams that need audit-grade revenue schedules, generally $50M ARR and above. The trade-off is implementation weight: Zuora takes months to configure and costs far more than Stripe Billing, which handles most vendors under $50M ARR. Compared with Salesforce Sales Cloud ranked eighth, Zuora closes the loop from closed-won deal to recognized revenue.
10Vanta
Vanta ranks tenth because bot mitigation vendors process traffic data at edge worldwide, making SOC 2 Type II, ISO 27001, GDPR, and often FedRAMP table stakes for enterprise procurement. Vanta runs $30K-$100K per year and automates continuous evidence collection across cloud infrastructure, cutting audit preparation from months of manual screenshotting to ongoing monitoring. It covers the compliance surface that security buyers audit before signing.
It is for vendors selling into enterprise security teams where a missing SOC 2 report kills deals outright. The trade-off is that Vanta covers the common frameworks well but FedRAMP Moderate still requires $2M-$8M and 24-36 months of dedicated effort. Compared with Zuora ranked ninth, Vanta secures the trust layer while Zuora secures the revenue layer.
How we ranked these
We ranked tools by weighting inline edge throughput and p95 latency budget first, since bot mitigation vendors live or die on sub-30ms allow/challenge/block decisions at 10M–10B requests/day. Second was detection signal depth: device fingerprinting, behavioral biometrics, TLS/JA3-JA4, HTTP/2-3 framing, IP reputation, and ML classifier quality. Third was adversarial update cadence, then storage economics at trillion-request scale, then CRM/billing fit for $25K–$2M ACV deals.
We deliberately ignored list prices, logo counts, and analyst quadrant placement, because edge unit economics and detection refresh speed decide renewals, not branding. We also excluded generic WAF features, marketing-site claims about "AI," and bundled DDoS/API modules that buyers rarely evaluate standalone. Compliance badges were down-weighted unless FedRAMP or PCI-DSS scope was explicit, since those gate federal and payment flows.
Related questions
Why does edge PoP architecture matter more than detection features for bot mitigation vendors?
Every protected request traverses the vendor's data plane, so PoP placement and hardware determine p95 latency. Custom PoPs cost $10K–$60K/month each but control the path; renting Cloudflare Workers or Fastly Compute@Edge at $5–$50 per million requests ships faster. Latency above 100ms gets the vendor ripped out regardless of detection accuracy.
How do behavioral biometrics differ from device fingerprinting in bot detection stacks?
Device fingerprinting collects 50–200+ static signals like canvas, WebGL, AudioContext, fonts, and hardware concurrency to identify a device. Behavioral biometrics capture mouse trajectory, keystroke timing, touch pressure, and scroll patterns to identify intent. Fingerprinting catches tooling; behavior catches humans-in-the-loop and sophisticated automation that spoofs hardware signals.
When should a bot mitigation vendor build custom PoPs versus renting Cloudflare Workers?
Rent edge below roughly $25M ARR: Cloudflare Workers or Fastly Compute@Edge deliver global coverage without capex. Build custom PoPs once traffic exceeds 10B requests/day or top customers cluster in specific geographies, because self-built PoPs run $10K–$60K/month each and pay back through latency and margin control. Hybrid models own PoPs in top regions and rent elsewhere.
What storage stack handles trillions of daily bot-detection request logs?
ClickHouse Cloud at $0.30–$1/GB hot handles recent analytics and customer dashboards. Iceberg on S3 stores long-tail request history cheaply for threat research and model retraining. Postgres holds customer config, protected-application metadata, and finding records. Sampling and aggregation are mandatory; raw retention of every request is economically impossible at scale.
Why do bot mitigation vendors need Neo4j or graph databases for threat research?
Attacker infrastructure clusters across IPs, ASNs, device fingerprints, and behavior patterns that relational joins handle poorly. Neo4j Enterprise at $36K–$300K/year encodes those relationships so analysts can pivot from one malicious IP to an entire campaign. Memgraph and TigerGraph are alternatives. Honeypot networks feed the graph with fresh attacker tooling and IPs.
How does per-billion-request pricing change the billing stack for bot mitigation vendors?
Usage-based pricing breaks flat subscription billing, so vendors adopt Stripe Billing under $50M ARR and Zuora at $200K–$1M/year for enterprise contracts. Metronome overlays usage metering. NetSuite plus Salesforce CPQ handles revenue recognition and Avalara tax. The billing stack must reconcile request counts, protected applications, and feature modules into one invoice customers trust.
What CRM configuration supports multi-stakeholder bot mitigation deals?
Salesforce Enterprise at $165/user/month with custom objects for protected applications, traffic volume tier, and attack-vector focus (credential stuffing, scraping, scalping, ad fraud). Clari at $80–$130/user/month forecasts; Gong at $1,600/user/year separates CISO, VP Engineering, VP Fraud, and VP Growth personas. Deals run $25K–$2M ACV over 60–180 day cycles.
Which compliance frameworks actually gate bot mitigation vendor sales?
SOC 2 Type II and ISO 27001 are table stakes, handled by Vanta or Drata at $30K–$100K/year. PCI-DSS matters for payment-flow protection; GDPR matters heavily because vendors process traffic data. FedRAMP gates federal deals and typically requires Hyperproof or AuditBoard at $60K–$300K/year. Buyers verify scope, not badges, so map controls to actual data flows.
FAQ
What is the best edge platform for a bot mitigation vendor in 2027?
There is no single winner. Cloudflare Workers and Fastly Compute@Edge win for time-to-market and global coverage at $5–$50 per million requests. Custom PoPs win for latency control and margin once traffic exceeds 10B requests/day. Akamai EdgeWorkers suits vendors already inside Akamai's ecosystem. Most growth-stage vendors run hybrid: owned PoPs in top customer regions, rented edge elsewhere.
How fast must bot detection decisions return to avoid customer churn?
Under 30ms p95 at the edge is the working target; above 100ms customers rip the vendor out because page-load suffers. Datadog dashboards should alert at 30ms per customer, not just globally. Lighter signal collection on non-sensitive endpoints, edge capacity auto-scaling, and per-endpoint tuning for checkout and signup flows keep latency inside budget as traffic scales.
Do bot mitigation vendors still need CAPTCHA providers in 2027?
Yes, as fallback and A/B layers. hCaptcha, Cloudflare Turnstile, and reCAPTCHA Enterprise integrate behind challenge orchestration. Arkose Labs MatchKey at $60K–$500K/year serves high-stakes account-takeover flows. Proof-of-work challenges handle most uncertain cases invisibly, but CAPTCHA remains the escalation path when detection confidence is low and the endpoint is high-value.
How do bot vendors counter residential proxy networks and headless browsers?
Layered signals: TLS JA3/JA4 fingerprinting exposes headless tooling, HTTP/2 and HTTP/3 frame fingerprinting reveals protocol anomalies, behavioral biometrics catch human-like automation, and IP intelligence from MaxMind, Spur, and IPQualityScore flags residential proxy ranges. Threat research ships countermeasures multiple times per week because bot operators update tooling daily.
What does a growth-stage bot mitigation vendor's stack cost monthly?
Roughly $1M–$4M/month at $25M–$100M ARR. That covers custom PoPs in 20–30 cities, proprietary fingerprinting and ML, Salesforce Enterprise plus Clari, Gong, and Outreach, Zuora plus NetSuite, Gainsight plus Pendo, and Vanta plus Hyperproof. Edge compute dominates the bill; sales and CS tooling is the second-largest line item.
Why is false-positive blocking the top failure mode for bot mitigation vendors?
Legitimate users get challenged repeatedly, abandon checkout, and conversion drops. The customer blames the vendor and churns. Fixes include per-customer ML model tuning, conversion-rate dashboards showing user-experience impact, A/B testing to validate challenge thresholds, and per-endpoint tuning for sensitive flows like checkout, signup, and password reset.
How should bot mitigation vendors differentiate against bundled Cloudflare or Akamai bot management?
Bundled bot wins on price and simplicity, so standalone vendors differentiate on detection depth, vertical specialization (retail scalping, financial credential stuffing, ad-tech fraud), integration depth with fraud platforms, and ROI proof comparing prevented fraud dollars to vendor cost. Public bot-mitigation reports showing update cadence also help against "good enough" bundled alternatives.
What threat research infrastructure do category-leading bot vendors run?
Honeypot networks collecting attacker tooling and IPs, IP reputation feeds from MaxMind, DigitalElement, Spur, and IPQualityScore at $30K–$300K/year each, and Neo4j or Memgraph graphs clustering IPs, ASNs, fingerprints, and campaigns. Threat research orgs of 50–200 people ship countermeasures multiple times weekly. This cadence is the moat against adversarial tool evolution.
How does FedRAMP change the bot mitigation vendor stack?
FedRAMP gates federal deals and forces Hyperproof or AuditBoard at $60K–$300K/year on top of Vanta or Drata. It also constrains edge architecture: data residency, logging retention, and personnel controls must map to FedRAMP boundaries. Vendors targeting federal agencies budget 12–24 months for authorization and often run a separate GovCloud edge footprint.
What 30/60/90 plan gets a new bot mitigation vendor to first revenue?
Days 1–30: deploy edge on Cloudflare Workers, ship client-side JS fingerprinting and behavioral biometrics, integrate hCaptcha fallback. Days 31–60: train ML classifiers on PyTorch with Triton edge inference, wire Salesforce plus Stripe or Zuora plus Gong. Days 61–90: stand up honeypots, IP reputation, Neo4j graph, Vanta SOC 2, and Gainsight onboarding.
Sources
- https://www.gartner.com/en/documents/4023083
- https://www.forrester.com/report/the-forrester-wave-tm-product-led-growth-platforms-q2-2026/RES180123
- https://www.bvp.com/atlas/state-of-the-cloud-2026
- https://www.cloudflare.com/developer-platform/workers/
- https://www.fastly.com/products/edge-compute
- https://clickhouse.com/cloud
- https://neo4j.com/product/neo4j-graph-database/
- https://www.datadoghq.com/product/infrastructure-monitoring/
- https://www.vanta.com/products/soc-2
- https://www.hcaptcha.com/
Related on PULSE
This page will be disappearing soon. Save it to your device for $1 — or read it free while it is here.
@Kory-White- · if Venmo asks, the last 4 of my number are 2012
This page is gone.
This one is off the shelf now. $1 keeps it on your phone for good — the whole page, pictures and diagrams included.
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Garden Centers and Nurseries in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for AI Music Generation Companies in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for AI Customer Support Companies in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Small Pest Control Companies in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Public Relations Agencies in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for HVAC Equipment Distributors in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for HOA and Community Association Management Companies in 2027
 tkTop 10 Best Tech Stack Tools for Fencing and Deck Contractors in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Threat Intelligence Vendors in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Tree Services in 2027