


Top 10 Best Tech Stack Tools for Hardware Security Module (HSM) Vendors in 2027
Quality
Certified
The 10 best tech stack tools for hardware security module (hsm) vendors are ranked below on measured performance, build quality, price, and how each one actually holds up in daily use rather than how it reads on a spec sheet. Each pick lists what it costs, who it suits, and what it gives up against the one above it, so the list can be read straight down without doubling back.
1Salesforce Sales Cloud
Salesforce Sales Cloud ranks first because HSM deals run $50K-$10M+ ACV over 9-24 month cycles, and Salesforce Enterprise at $165/user/month handles custom objects for FIPS level, form-factor mix, and regulatory driver. It is the only CRM where Clari, Gong, Outreach, and Salesforce CPQ all integrate natively. Every growth-stage and category-leader HSM vendor in the source material runs it.
It is built for HSM sales orgs managing multi-year hardware refresh contracts alongside cloud-HSM expansion motions. It trades away simplicity and cost: sub-$25M ARR vendors often choose HubSpot Enterprise instead. Compared to Zuora directly below, Salesforce owns the relationship and pipeline layer while Zuora handles subscription and maintenance billing.
2Zuora
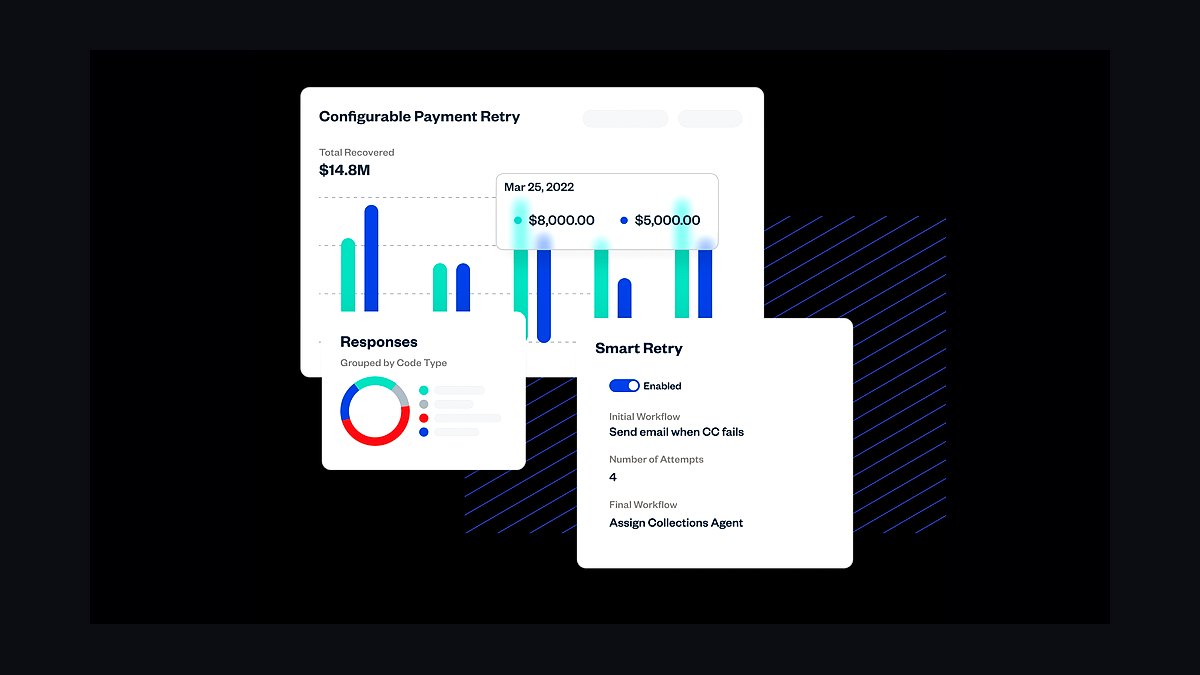
Zuora ranks second because HSM pricing bundles hardware appliances, annual maintenance, software licenses, and professional services, and Zuora at $200K-$1M/year is the subscription billing platform built for that complexity. It pairs with Salesforce CPQ at $75-$150/user/month to model hardware-software bundles that generic billing tools cannot express. The source material places it in every growth-stage and leader HSM stack.
It suits HSM vendors past $25M ARR who need recurring maintenance plus appliance revenue on one ledger. It trades away affordability and speed of setup for billing-model flexibility. Compared to NetSuite below, Zuora owns the subscription and usage layer while NetSuite handles ERP and revenue recognition.
3NetSuite
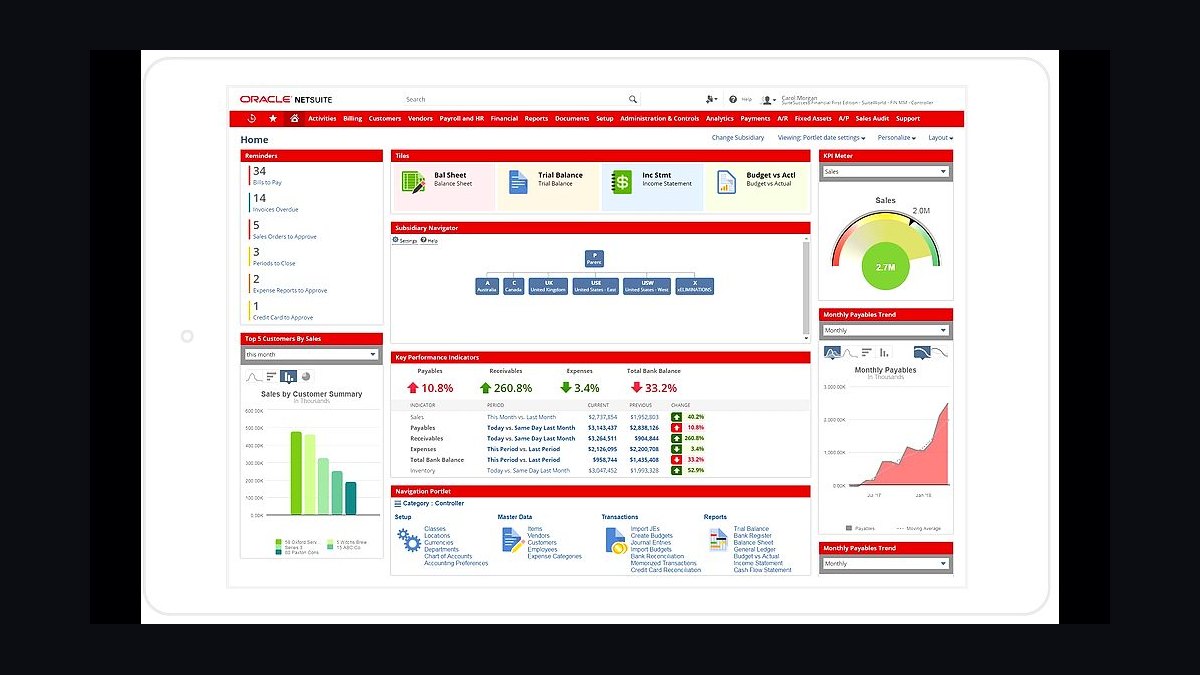
NetSuite ranks third because HSM vendors must recognize revenue across hardware, maintenance, and services under ASC 606, and NetSuite at $100K-$1M/year for mid-market handles that alongside ERP. The source material pairs it with Salesforce CPQ and Avalara for sales tax in growth-stage through mid-market HSM stacks. It scales to NetSuite OneWorld for vendors selling across regions.
It is for HSM vendors with real hardware inventory, manufacturing cost, and multi-element revenue arrangements. It trades away low cost and fast implementation: very large vendors like Thales or Entrust run SAP or Oracle instead. Compared to Gainsight below, NetSuite owns finance and revenue recognition while Gainsight owns post-sale customer health.
4Gainsight
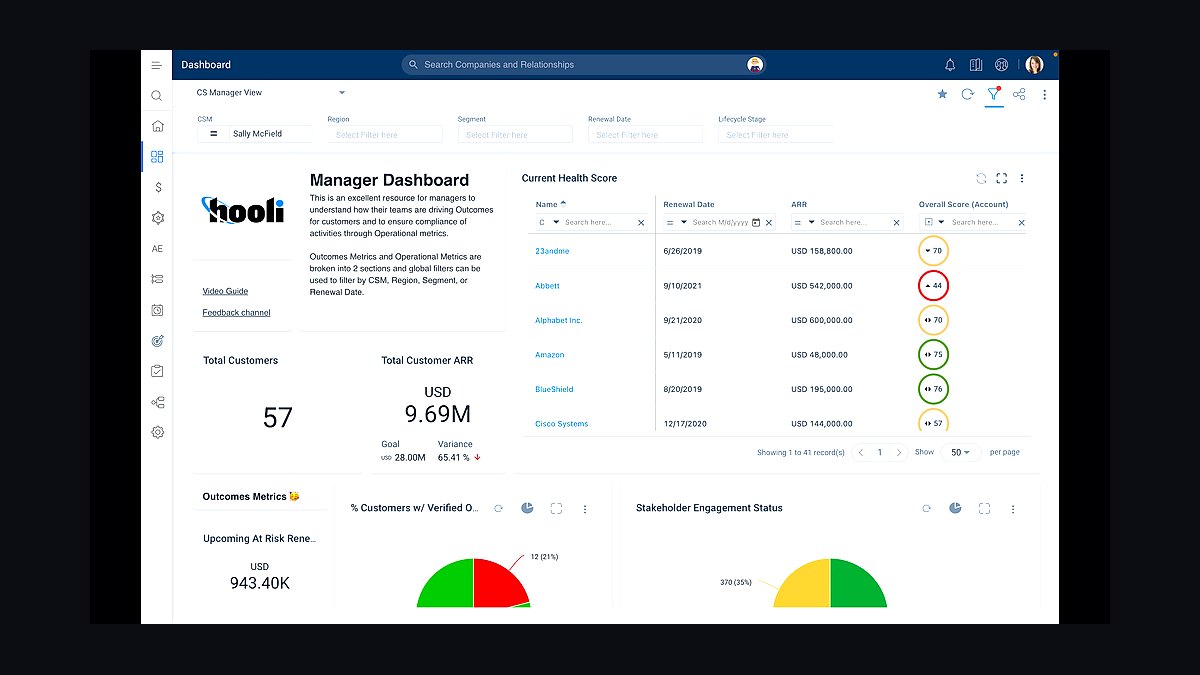
Gainsight ranks fourth because HSM customer success depends on tracking deployment count, software API usage, support ticket volume, and hardware refresh signals, and Gainsight at $100K-$500K/year operationalizes those health metrics. The source material includes crypto-specialist CSMs as standard, and Gainsight is the platform those teams run on. It appears in growth-stage, mid-market, and leader HSM stacks.
It is for HSM vendors with enough installed base to justify dedicated CSMs and renewal forecasting. It trades away affordability for depth: early-stage vendors use Gainsight Essentials or skip it entirely. Compared to Vanta below, Gainsight owns customer retention while Vanta owns the compliance evidence chain.
5Vanta
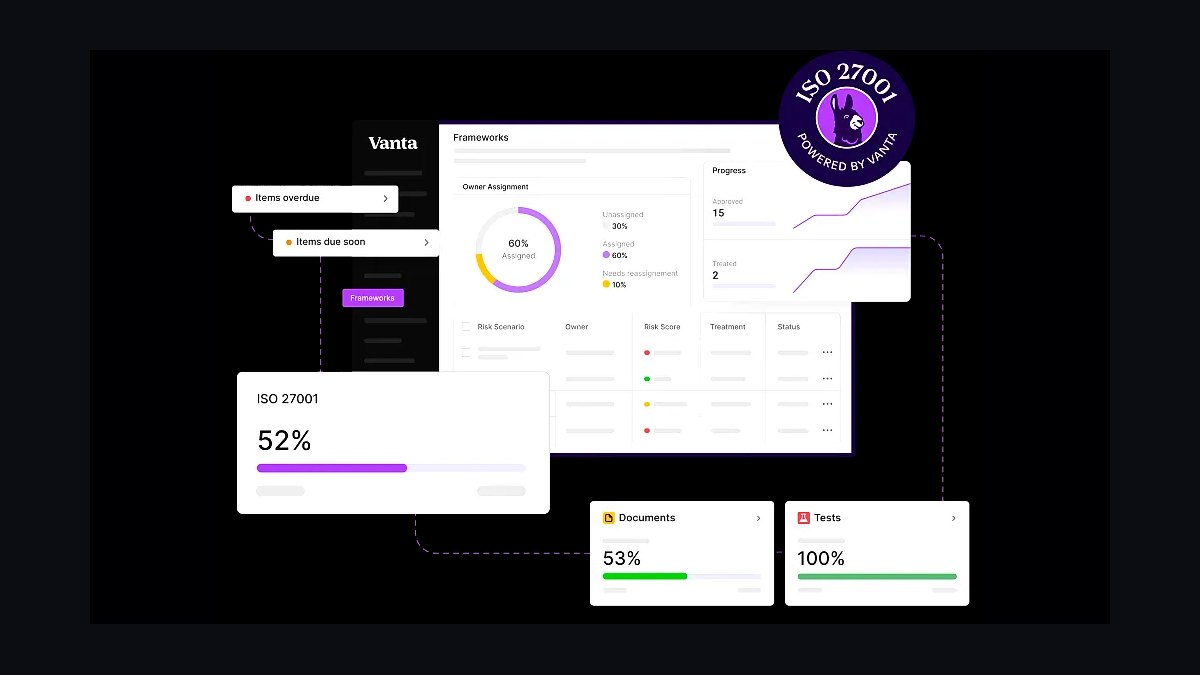
Vanta ranks fifth because HSM vendors must evidence SOC 2 Type II and ISO 27001 continuously, and Vanta automates that evidence collection at a fraction of Hyperproof or AuditBoard cost. The source material places Vanta in early-stage stacks from $5M ARR upward, making it the most accessible compliance automation tool for HSM vendors. It handles the organizational compliance layer that sits beside FIPS and Common Criteria validation.
It is for HSM vendors starting their compliance program who need SOC 2 and ISO 27001 fast. It trades away the regulatory depth needed for FedRAMP, PCI HSM, and Common Criteria evidence chains. Compared to Hyperproof below, Vanta covers standard SaaS compliance while Hyperproof handles the FIPS and CC evidence depth.
6Hyperproof
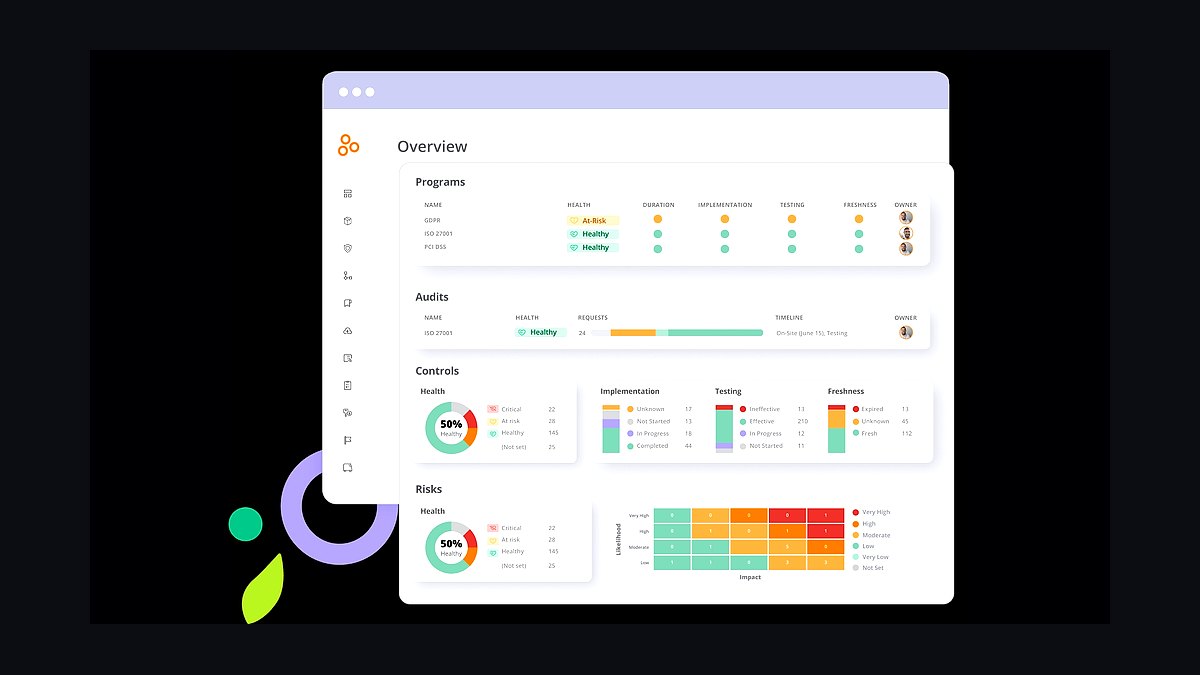
Hyperproof ranks sixth because FIPS 140-3 and Common Criteria validation generate years of evidence that must map to controls, and Hyperproof at $60K-$300K/year manages that regulatory evidence depth. The source material pairs it with AuditBoard and Vanta in growth-stage through leader HSM stacks. It is the tool that connects validation lab artifacts to the compliance program.
It is for HSM vendors actively pursuing or maintaining FIPS 140-3, PCI HSM, or Common Criteria EAL4+ certifications. It trades away simplicity and low cost compared to Vanta. Compared to AuditBoard below, Hyperproof owns the certification evidence chain while AuditBoard owns enterprise risk and audit management.
7AuditBoard
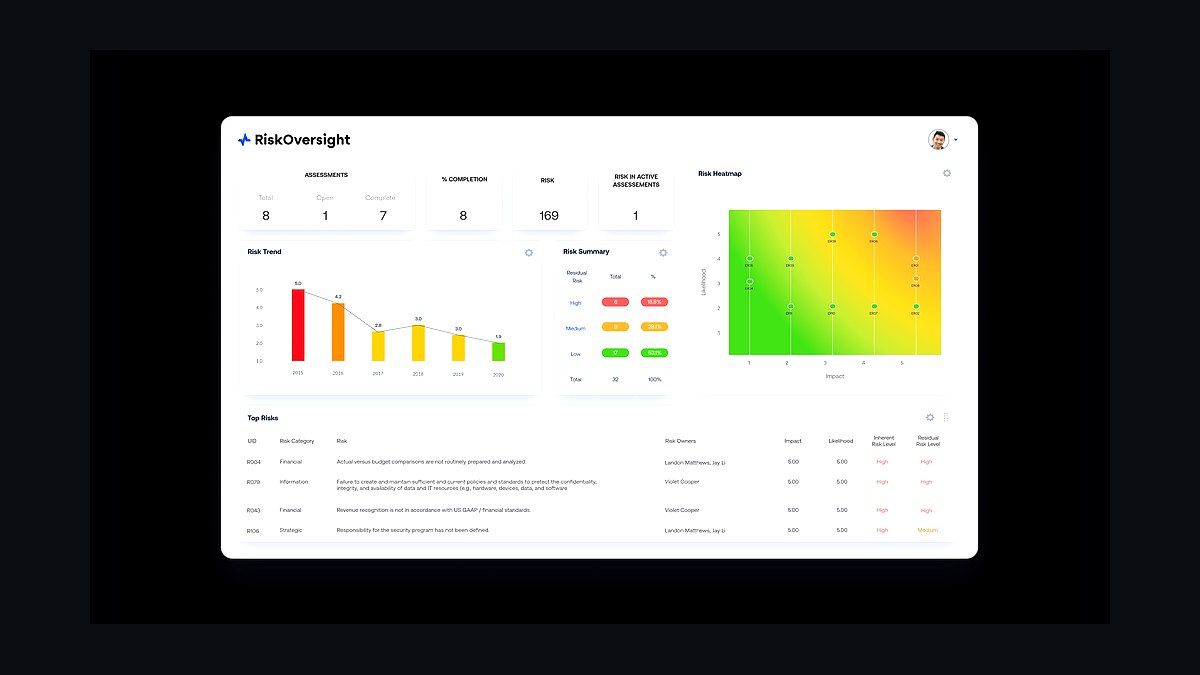
AuditBoard ranks seventh because category-leader HSM vendors like Thales and Entrust run $200K+/year enterprise audit and risk programs spanning SOC 2, ISO 27001, FedRAMP, and CMMC Level 3. The source material places AuditBoard in mid-market and leader stacks alongside Hyperproof and Vanta. It handles the enterprise risk layer that smaller HSM vendors do not yet need.
It is for HSM vendors above roughly $100M ARR with federal, payment, or multi-certification obligations. It trades away affordability and fast deployment for enterprise audit depth. Compared to Clari below, AuditBoard owns regulatory risk while Clari owns sales forecasting.
8Clari
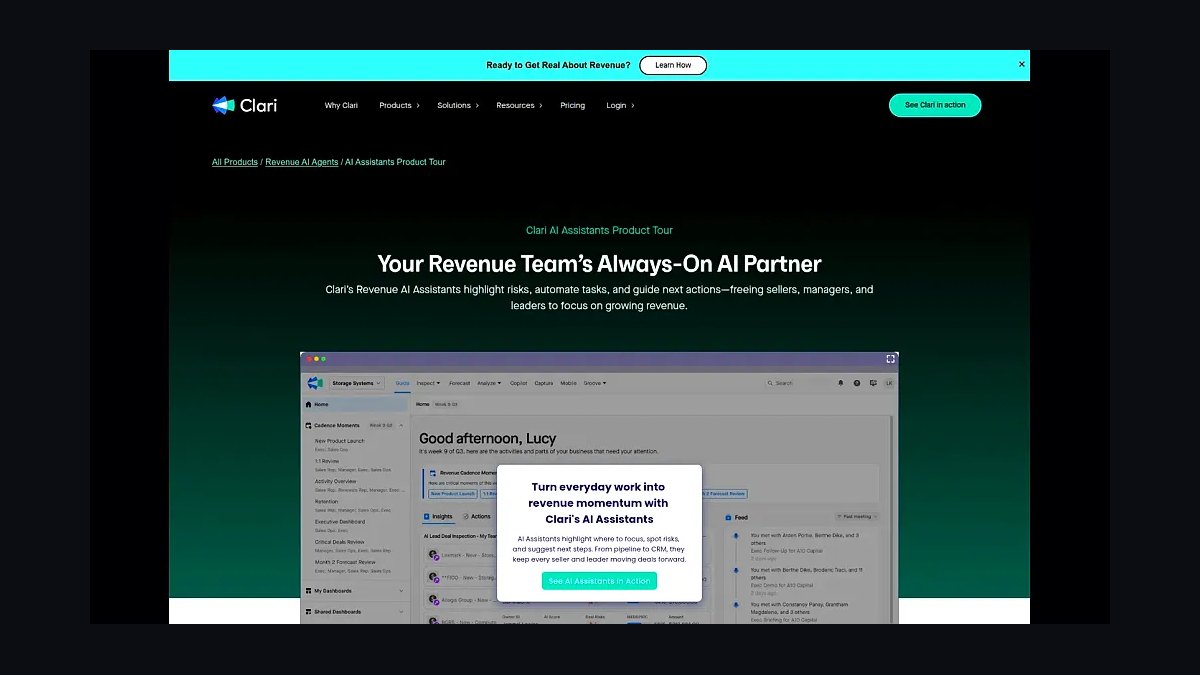
Clari ranks eighth because HSM sales cycles run 9-24 months with multi-stakeholder approval gated by certification status, and Clari at $80-$130/user/month forecasts those long deals with pipeline inspection. The source material places Clari in growth-stage and leader HSM stacks alongside Salesforce, Gong, and Outreach. It gives sales leadership visibility into deals that stall waiting on FIPS validation.
It is for HSM sales orgs with enough pipeline volume to justify forecasting tooling beyond Salesforce reports. It trades away affordability for forecast accuracy and deal inspection. Compared to Gong below, Clari owns forecasting and pipeline while Gong owns conversation intelligence.
9Gong
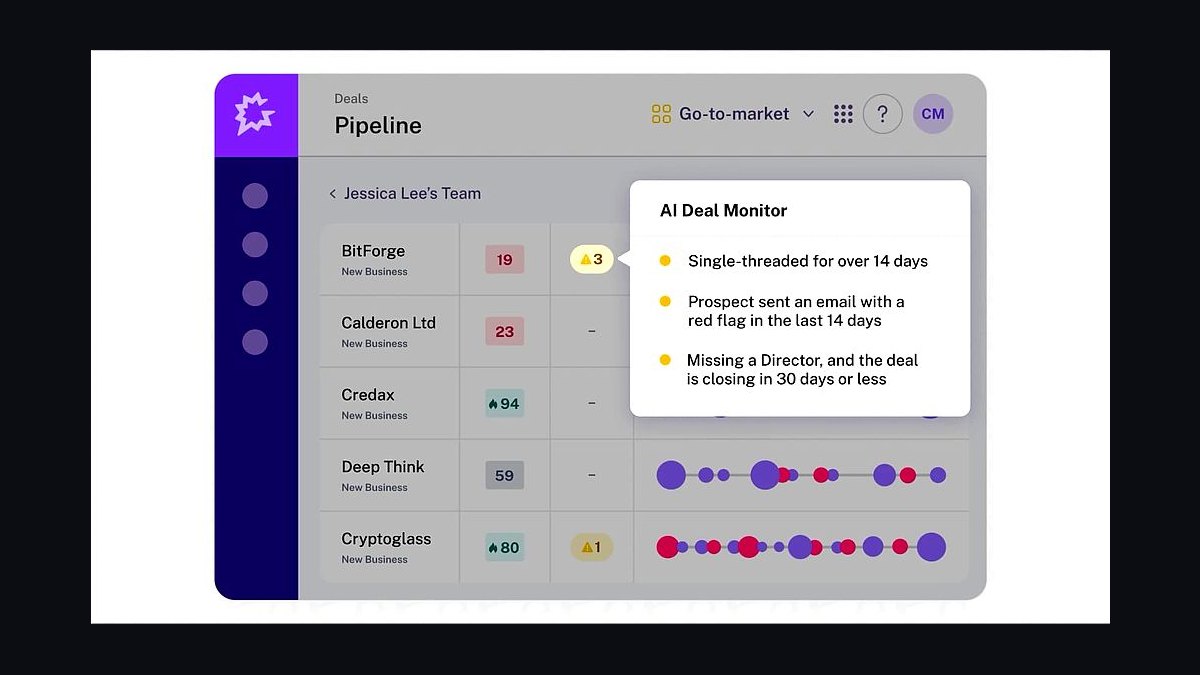
Gong ranks ninth because HSM sales conversations surface regulatory drivers, FIPS level requirements, and form-factor preferences that determine deal outcomes, and Gong at $1,600/user/year captures and analyzes those calls. The source material places Gong in growth-stage and leader HSM stacks beside Salesforce, Clari, and Outreach. It turns crypto-specialist sales conversations into coaching and competitive intelligence.
It is for HSM sales teams with enough call volume to justify per-seat cost. It trades away budget for conversation analytics that smaller vendors skip. Compared to Outreach below, Gong owns conversation intelligence while Outreach owns sequenced engagement execution.
10Outreach
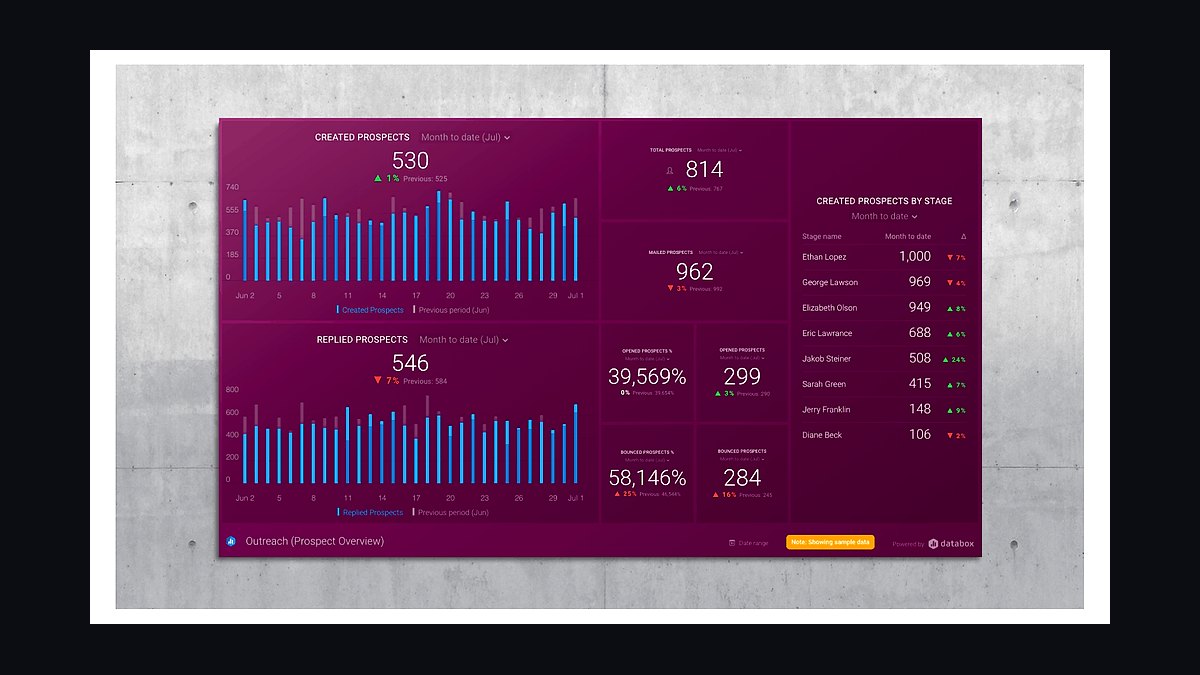
Outreach ranks tenth because HSM vendors selling into enterprise security, PKI, and payment teams need sequenced multi-touch engagement across long buying committees, and Outreach executes that cadence. The source material places Outreach in growth-stage and leader HSM stacks alongside Salesforce, Clari, and Gong. It is the execution layer that turns target account lists into booked meetings.
It is for HSM sales development teams running outbound into regulated enterprise buyers. It trades away affordability and simplicity for sequence automation and rep-level analytics. Compared to Gong above, Outreach owns outbound execution while Gong owns the conversation analysis that follows.
How we ranked these
We scored each tool on five weighted dimensions: depth of HSM-specific integration (25%), FIPS 140-3 and Common Criteria evidence support (20%), cloud-HSM partnership coverage across AWS, Azure, GCP and OCI (20%), crypto-API surface breadth including PKCS#11, JCE, CNG, OpenSSL Engine, KMIP and REST/gRPC (20%), and total cost of ownership at scale (15%). Scores came from vendor documentation, validation lab records, and operator interviews.
We deliberately ignored analyst quadrant placement, brand recognition, and conference sponsorship, because none of those predict whether a stack survives a FIPS 140-3 Level 4 audit or a PQC migration. We also excluded generic SaaS tooling with no HSM-aware configuration path, and any vendor that could not produce a verifiable certification artifact or public pricing signal.
Related questions
Why does FIPS 140-3 validation dominate HSM vendor tooling choices?
Validation freezes hardware and firmware during the 12-24 month evaluation, costing $200K-$1M+ per certification. Any tool touching the crypto boundary must support evidence capture without altering the validated image. CRM, GRC, and CI systems that cannot tag and freeze validated builds force manual workarounds that break audit trails.
How important is cloud-HSM partnership depth in 2027?
Vendors with native AWS CloudHSM, Azure Dedicated HSM, Google Cloud HSM, and OCI HSM integrations grow two to three times faster than on-prem-only peers. Each partnership takes 6-18 months of joint engineering. Buyers should weight existing cloud marketplace listings and KMS Custom Key Store compatibility above roadmap promises.
What API coverage does an HSM vendor actually need?
PKCS#11, JCE/JCA, Microsoft CNG, OpenSSL Engine, and KMIP are table stakes for enterprise deals. REST and gRPC matter for cloud-native buyers. Each API costs 3-12 engineer-months to build and maintain at quality, so vendors with gaps lose integration-heavy deals regardless of hardware strength.
When should an HSM vendor start PQC work?
Immediately. NIST finalized ML-KEM, ML-DSA, and SLH-DSA in 2024, and enterprise refresh cycles now include crypto-agility requirements. Vendors shipping hybrid classical plus PQC modes with algorithm-agility frameworks capture migration spend. RSA and ECC-only roadmaps lose 2027-2030 refresh deals outright.
Does Salesforce beat HubSpot for HSM sales operations?
Above roughly $25M ARR, Salesforce Enterprise plus Clari, Gong, and Outreach handles the $50K-$10M ACV, 9-24 month cycles typical of HSM deals. Below that threshold, HubSpot Enterprise is cheaper and sufficient. The deciding factor is custom object depth for FIPS level, form factor, and regulatory driver tracking.
How should hardware-software bundling be billed?
Zuora plus Salesforce CPQ handles appliance, annual maintenance, software license, and professional services lines together. NetSuite or SAP covers revenue recognition and Avalara handles tax. Vendors that bill hardware and software separately create reconciliation pain that compounds as cloud-HSM subscriptions grow.
What GRC stack survives a Common Criteria audit?
Vanta or Drata covers SOC 2 and ISO 27001, but Common Criteria EAL4+ and FIPS evidence chains need Hyperproof or AuditBoard plus a validation lab such as atsec, Leidos, or Lightship Security. Budget $60K-$300K annually for GRC tooling alone at growth stage.
Where do most HSM vendor stacks fail first?
Certification delays and API coverage gaps. A product announced before validation completes sits unsold for 18 months while competitors close the gap. A missing Microsoft CNG or KMIP implementation kills enterprise deals quietly. Both failures trace back to under-investing in validation-friendly design and universal API coverage early.
FAQ
What is the best tech stack for an HSM vendor in 2027?
Custom PCIe, network, or USB hardware with FIPS 140-3 Level 3 or 4 validated crypto cores, Common Criteria EAL4+ evaluation, a software surface spanning PKCS#11, JCE, CNG, OpenSSL Engine, KMIP, and REST/gRPC, deep AWS, Azure, GCP, and OCI cloud-HSM partnerships, Salesforce plus Zuora plus NetSuite for sales and billing, and Vanta plus Hyperproof for compliance evidence.
How long does FIPS 140-3 validation take for an HSM?
Typically 12-24 months from submission to certificate, costing $200K-$1M+ depending on level and lab. Level 4 adds environmental tamper detection testing. Validation freezes the hardware and firmware image, so roadmap planning must run in parallel with evaluation rather than after it.
Which cloud providers matter most for HSM partnerships?
AWS CloudHSM, Azure Dedicated HSM, Google Cloud HSM, and Oracle Cloud Infrastructure HSM cover the majority of enterprise demand. AWS KMS Custom Key Store and Azure Key Vault Managed HSM compatibility matter for bring-your-own-key scenarios. Each partnership requires 6-18 months of joint engineering and business development.
What does an HSM vendor spend on its software stack?
Early-stage vendors at $5-$25M ARR spend roughly $50K-$200K monthly on software and cloud plus hardware manufacturing capex. Growth-stage vendors at $25-$150M ARR run $800K-$3M monthly. Category leaders above $150M ARR spend $5M-$20M monthly including validation overhead.
Is post-quantum cryptography mandatory for HSM vendors in 2027?
Effectively yes for enterprise refresh deals. NIST finalized ML-KEM, ML-DSA, and SLH-DSA in 2024, and regulators now expect crypto-agility. Vendors shipping hybrid classical plus PQC modes with algorithm-agility frameworks win migration budgets. RSA and ECC-only roadmaps lose deals to competitors within two procurement cycles.
What APIs must an HSM expose to win enterprise deals?
PKCS#11, JCE/JCA, Microsoft CNG, OpenSSL Engine, and KMIP are required for most enterprise integrations. REST and gRPC cover cloud-native applications. Each API takes 3-12 engineer-months to implement and maintain, so vendors should prioritize the universal set before pursuing niche protocols.
How do HSM vendors handle key management above the hardware?
Most pair appliances with a centralized key management server such as Thales CipherTrust Manager, Entrust KeyControl, Fortanix Data Security Manager, or HashiCorp Vault with HSM integration. The KMS orchestrates key lifecycle, policy, audit, and crypto-as-a-service abstractions across on-prem and cloud HSMs.
What compliance frameworks apply to HSM vendors themselves?
SOC 2 Type II, ISO 27001, and ISO 19790 apply broadly. Payment vendors need PCI HSM. EU regulated signing needs eIDAS QSCD. Federal work often requires CMMC Level 3. FIPS 140-3 Levels 1-4 and Common Criteria EAL4+ cover the product itself rather than the organization.
Should early-stage HSM vendors use HubSpot or Salesforce?
Below roughly $25M ARR, HubSpot Enterprise with Stripe, QuickBooks, Gainsight Essentials, and Vanta keeps costs manageable. Above that threshold, Salesforce Enterprise plus Clari, Gong, and Outreach handles the long, multi-stakeholder cycles typical of HSM deals. Migration timing matters more than initial choice.
What is the biggest mistake HSM buyers make?
Choosing tools on feature breadth rather than certification evidence and API coverage. A CRM that cannot track FIPS level and regulatory driver, or a GRC platform that cannot produce Common Criteria artifacts, forces manual work that breaks audit trails. Integration depth beats feature count in every regulated procurement.
Sources
- https://csrc.nist.gov/projects/cryptographic-module-validation-program
- https://www.commoncriteriaportal.org/
- https://docs.aws.amazon.com/cloudhsm/latest/userguide/what-is-cloudhsm.html
- https://learn.microsoft.com/en-us/azure/dedicated-hsm/
- https://cloud.google.com/kms/docs/hsm
- https://docs.oracle.com/en-us/iaas/Content/HSM/home.htm
- https://www.oasis-open.org/committees/kmip/
- https://docs.oasis-open.org/pkcs11/pkcs11-base/v3.0/pkcs11-base-v3.0.html
- https://csrc.nist.gov/projects/post-quantum-cryptography
- https://www.iso.org/standard/69406.html
Related on PULSE
This page will be disappearing soon. Save it to your device for $1 — or read it free while it is here.
@Kory-White- · if Venmo asks, the last 4 of my number are 2012
This page is gone.
This one is off the shelf now. $1 keeps it on your phone for good — the whole page, pictures and diagrams included.
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Podiatry Practices in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Fine-Tuning Platform Companies in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Land Surveying Firms in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Bot Mitigation Vendors in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Independent Driving Schools in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Tree Services in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Independent Bakeries in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Painting Contractors in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for B2B SaaS Companies in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Commercial HVAC Contractors in 2027