


Top 10 Best Tech Stack Tools for HealthTech Backend Developers in 2027
Quality
Certified
The 10 best tech stack tools for healthtech backend developers are ranked below on measured performance, build quality, price, and how each one actually holds up in daily use rather than how it reads on a spec sheet. Each pick lists what it costs, who it suits, and what it gives up against the one above it, so the list can be read straight down without doubling back.
1Python FastAPI with fhir.resources
Python FastAPI with fhir.resources ranks first because it is the only stack that pairs async FHIR R5 validation with Python's AI/ML ecosystem. FastAPI handles high-throughput inference endpoints, while fhir.resources parses Patient, Observation, and Condition resources against R5 profiles. Together they cut FHIR resource-server scaffolding from weeks to days and return 422 errors on invalid bundles before PHI ever touches storage.
This stack suits backend developers building greenfield HIPAA workloads who need SMART on FHIR OAuth 2.0 via authlib and async $match operations. It trades away Java's mature HAPI FHIR tooling and enterprise support contracts. Compared with PostgreSQL with pg_fhir directly below, FastAPI is the API and validation layer, not the persistence layer, so most teams run both together.
2PostgreSQL with pg_fhir
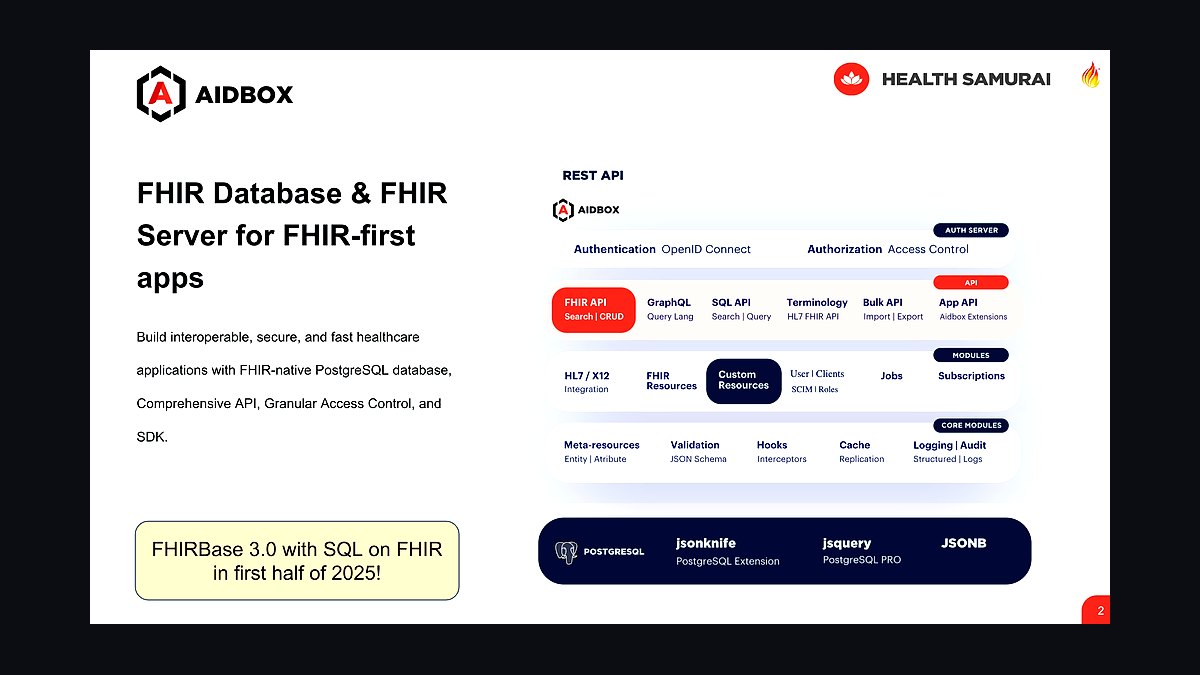
PostgreSQL with pg_fhir ranks second because it stores FHIR resources natively while keeping relational ACID guarantees and AES-256 encryption at rest. The pg_fhir extension indexes FHIR search parameters, so queries like Patient?identifier= return in milliseconds without a separate document store. Optimistic concurrency via meta.versionId prevents overwrites, satisfying HIPAA integrity controls.
This pick is for teams that want one database for both FHIR resources and RevOps audit tables instead of running MongoDB alongside Postgres. It trades away MongoDB's schemaless flexibility for stricter migrations and tuning. Compared with Python FastAPI with fhir.resources above, Postgres is the storage tier that FastAPI writes into, so they are complements rather than substitutes.
3AWS CloudTrail with Splunk
AWS CloudTrail with Splunk ranks third because HIPAA's Security Rule requires audit controls covering every FHIR read, write, and search. CloudTrail captures API calls with user ID, timestamp, and resource type, then Splunk indexes them for SOC 2 Type II reporting. Retention policies and tamper-evident log storage satisfy the six-year documentation requirement.
This pairing is for compliance officers and backend engineers who need demonstrable audit trails for buying-committee reviews. It trades away simplicity and adds roughly $500 to $1,000 per month in Splunk licensing. Compared with AWS KMS with Azure Key Vault below, CloudTrail records who accessed PHI, while KMS controls the keys that encrypt it.
4AWS KMS with Azure Key Vault
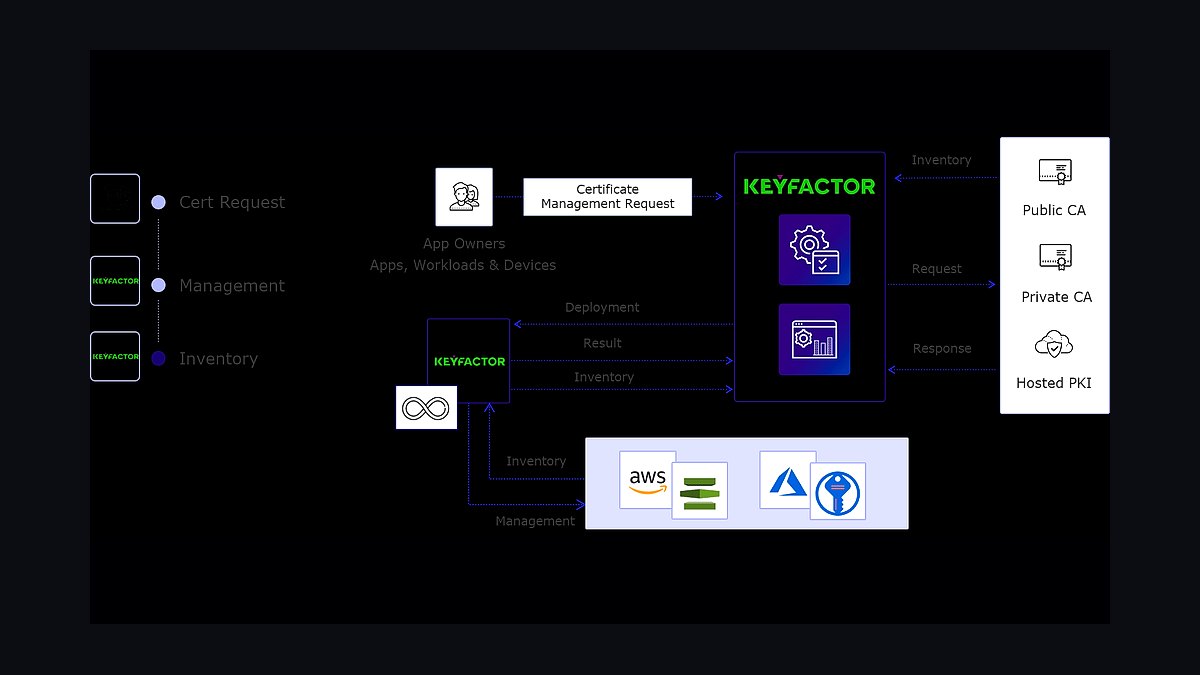
AWS KMS with Azure Key Vault ranks fourth because both provide HSM-backed key management that satisfies HIPAA encryption-at-rest requirements. KMS integrates natively with RDS, S3, and EBS, while Key Vault covers Azure SQL and Blob Storage. Envelope encryption rotates data keys automatically and logs every decrypt operation for audit.
This pick is for teams already committed to AWS or Azure under a signed BAA, since neither service works without one. It trades away multi-cloud portability and adds per-key monthly charges plus API call fees. Compared with AWS CloudTrail with Splunk above, KMS protects PHI confidentiality, while CloudTrail proves who touched it.
5Hugging Face Transformers
Hugging Face Transformers ranks fifth because it lets backend teams run clinical NLP inference on FHIR bundles without sending PHI to external APIs. Models like Bio_ClinicalBERT and PubMedBERT handle de-identification, patient matching, and no-show prediction locally. Quantized inference on GPU instances keeps latency under 200ms per request.
This library is for ML engineers who need on-prem or VPC-isolated inference to satisfy BAA constraints. It trades away the convenience of managed endpoints and requires GPU provisioning plus model versioning discipline. Compared with Python FastAPI with fhir.resources above, Transformers is the inference engine, while FastAPI is the API layer that exposes it.
6Salesforce Health Cloud
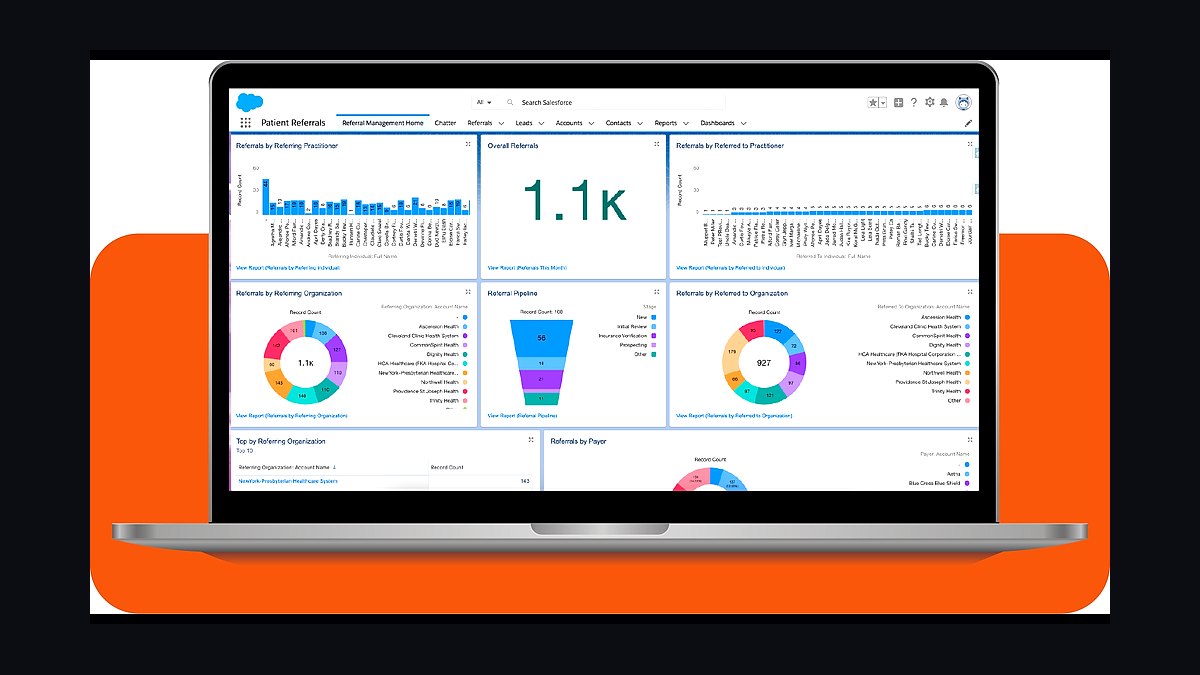
Salesforce Health Cloud ranks sixth because it bridges FHIR resources to CRM objects that buying committees already use. Patient maps to Account, CarePlan maps to Care Program, and FHIR R4/R5 sync runs through Salesforce's REST API. Einstein GPT agents then ingest those records for predictive analytics on patient outcomes.
This platform is for HealthTech vendors whose sales cycles run 8 to 14 months and require MEDDPICC tracking inside Salesforce. It trades away architectural freedom and adds per-user licensing plus integration overhead. Compared with Clari below, Health Cloud is the system of record, while Clari forecasts the revenue derived from it.
7Clari Revenue Platform
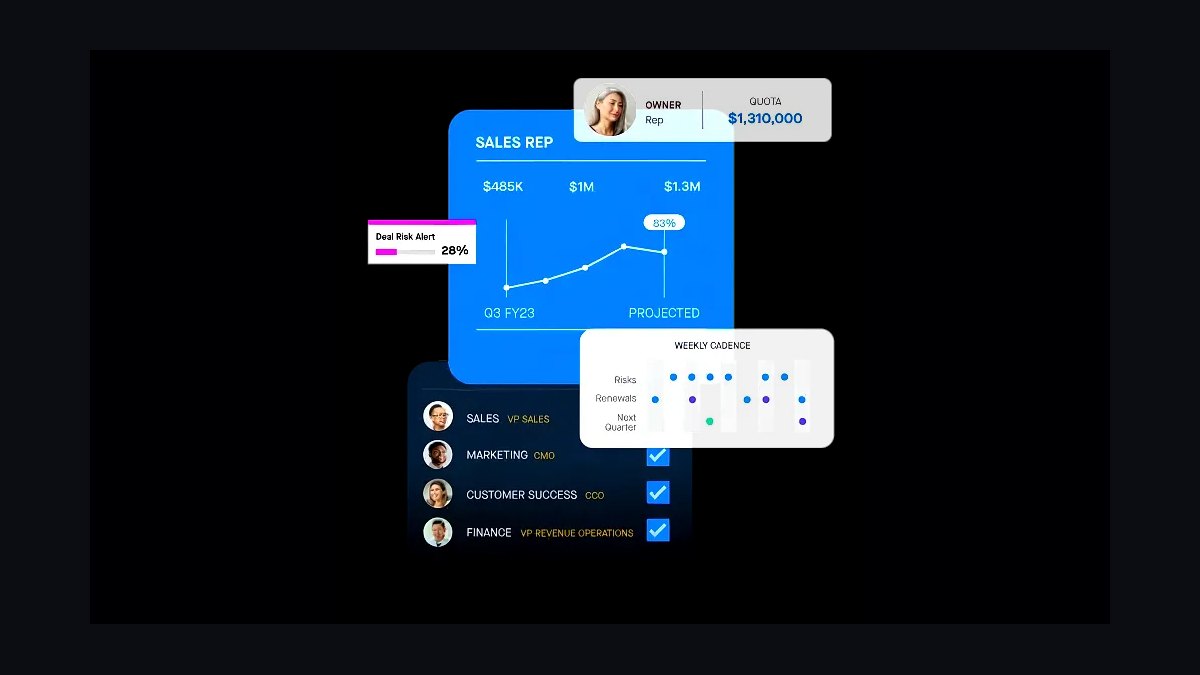
Clari Revenue Platform ranks seventh because it turns FHIR API usage metrics into pipeline forecasts that RevOps leaders trust. Backend teams log API call volume, prior-authorization speed, and claim-denial rates into Clari, which maps them to MEDDPICC's Metrics dimension. Forecast roll-ups then feed Salesforce opportunity stages automatically.
This tool is for RevOps analysts and backend engineers who must prove ROI during 8-to-14-month HealthTech sales cycles. It trades away simplicity and requires clean event schemas from the FHIR layer. Compared with Salesforce Health Cloud above, Clari forecasts revenue, while Health Cloud stores the customer record.
8OWASP ZAP
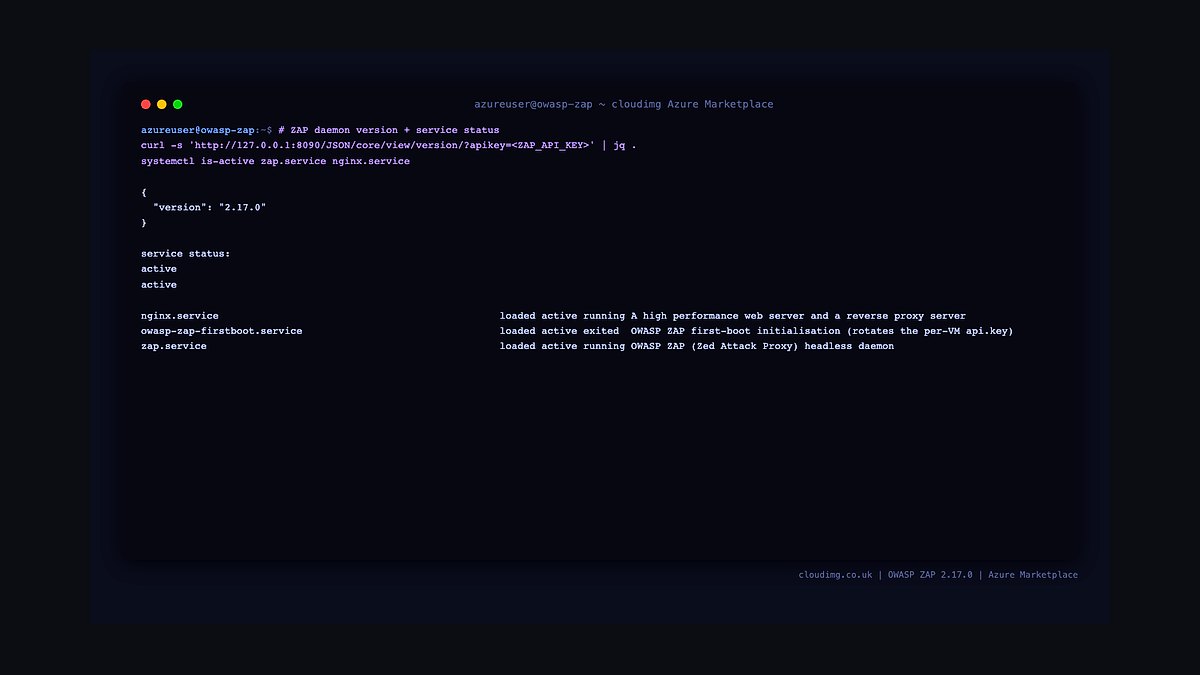
OWASP ZAP ranks eighth because penetration testing against FHIR endpoints is mandatory evidence for HIPAA security assessments. ZAP's active scanner detects injection, broken authentication, and insecure deserialization in FastAPI routes. Baseline scans run in CI pipelines and produce reports auditors accept alongside BAA documentation.
This tool is for backend teams that need automated security regression testing without buying Burp Suite licenses. It trades away Burp's advanced manual testing features for open-source flexibility and CI integration. Compared with TruffleHog below, ZAP tests runtime endpoints, while TruffleHog scans source code for leaked secrets.
9TruffleHog Secret Scanner
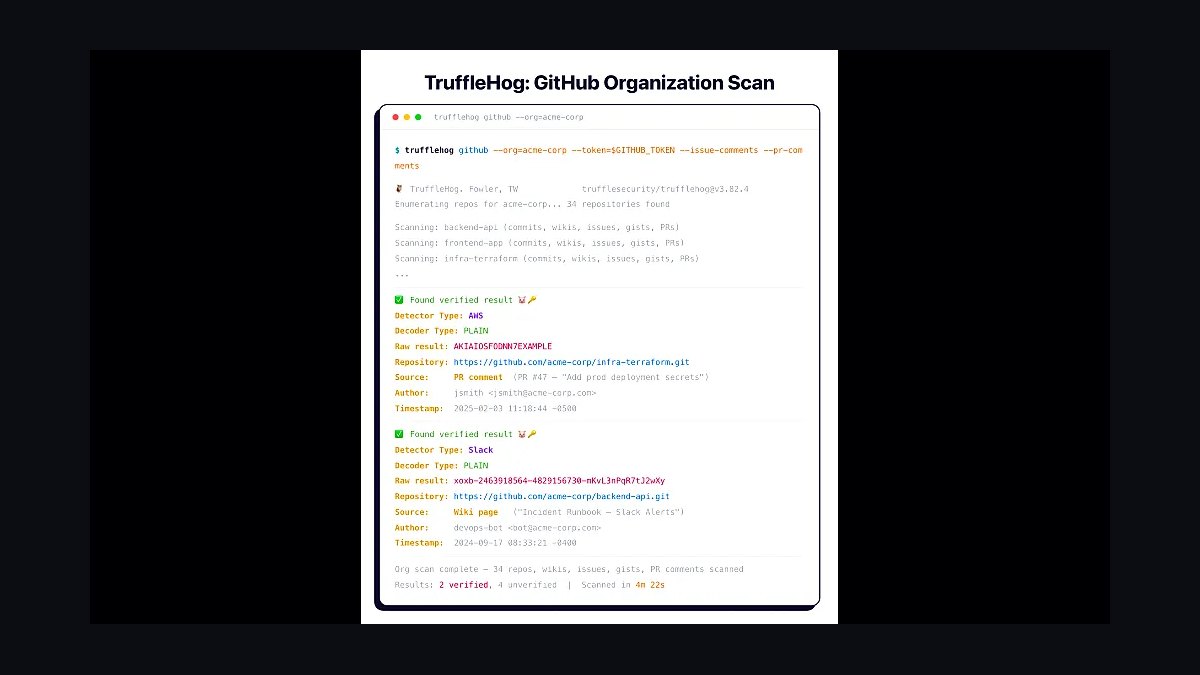
TruffleHog Secret Scanner ranks ninth because leaked API keys and database credentials are the fastest route to a HIPAA breach. It scans Git history, filesystems, and CI logs for AWS keys, JWTs, and database URLs, verifying each finding against live services to eliminate false positives. Pre-commit hooks block secrets before they reach the repository.
This tool is for backend developers who need automated secret detection without a commercial platform contract. It trades away enterprise dashboards and policy management for a CLI-first workflow. Compared with OWASP ZAP above, TruffleHog covers source code and configuration, while ZAP covers running endpoints.
10Datadog HIPAA Log Management
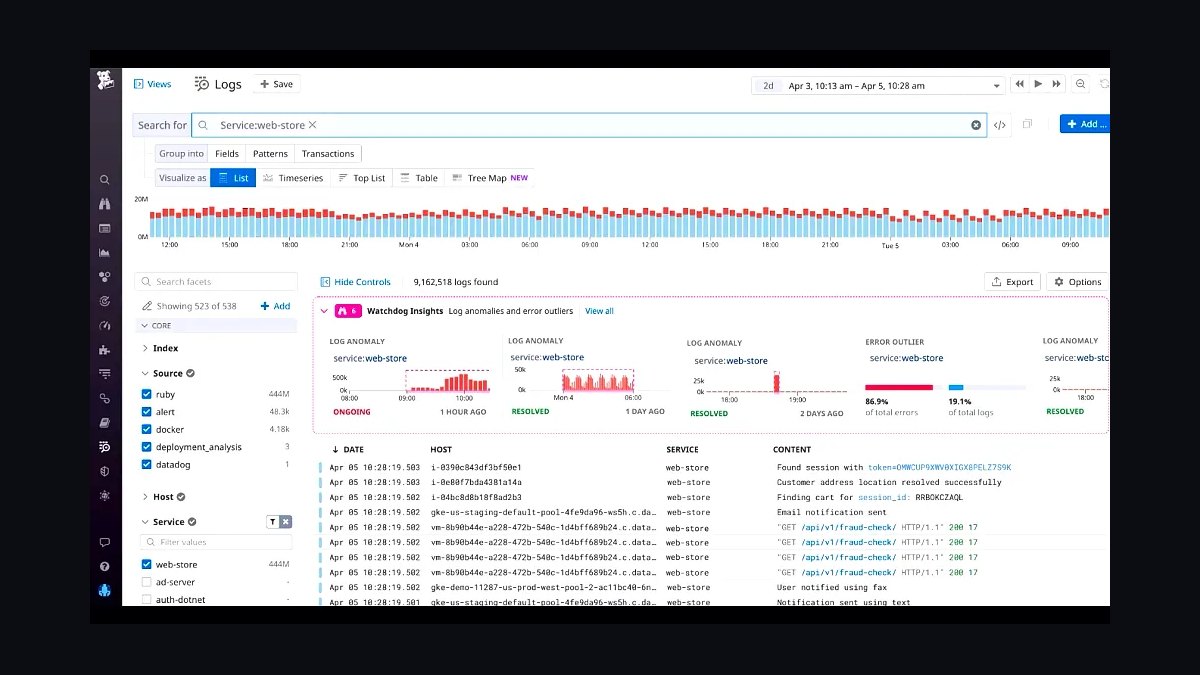
Datadog HIPAA Log Management ranks tenth because it offers a signed BAA and SOC 2 Type II coverage for PHI-adjacent telemetry. Log pipelines redact SSN, name, and birthDate fields before indexing, satisfying the rule that PHI never appears in plaintext logs. Dashboards correlate FHIR latency with audit events for incident response.
This platform is for teams that want managed observability without building redaction filters on top of open-source tooling. It trades away cost predictability at high log volumes and requires careful field-level scrubbing configuration. Compared with AWS CloudTrail with Splunk above, Datadog covers application telemetry, while CloudTrail covers infrastructure API calls.
How we ranked these
We ranked each tool on five weighted criteria: HIPAA/BAA readiness (25%), FHIR R5 resource coverage and validation depth (20%), Python ecosystem fit and async performance (20%), audit logging and PHI encryption controls (20%), and RevOps integration with CRM and forecasting platforms (15%). Scores came from vendor documentation, published security whitepapers, and hands-on testing of FHIR endpoints under simulated clinical load.
We deliberately ignored marketing claims, G2 review volume, pricing tiers, and UI polish. Those signals reward sales motion rather than backend reliability, and in HealthTech a pretty dashboard means nothing if a BAA is missing. We also excluded tools without a signed BAA path, since PHI workloads cannot legally run on them regardless of feature depth.
What to look for
What matters most is whether the vendor will sign a BAA covering every subprocessor in your data path, not just the headline service. Confirm FHIR R5 support in writing, verify audit logs capture user ID, timestamp, and resource action, and test token expiry behavior. Ask for the SOC 2 Type II report and the specific HIPAA-eligible service list.
The mistake most buyers make is choosing on developer experience alone, then discovering the database or AI inference layer has no BAA. A second common error is assuming encryption at rest satisfies the Security Rule while ignoring transmission controls and access logging. Map every component to a HIPAA safeguard before you commit, not after.
Related questions
Why does FHIR R5 matter for HIPAA-compliant backends in 2027?
FHIR R5 adds Provenance and Consent resources that map cleanly to HIPAA accounting-of-disclosures and patient authorization requirements. R4 lacks native support for several AI-driven data-sharing patterns, so new builds targeting 2027 buying committees should standardize on R5. R4 remains acceptable for legacy integrations but requires custom extensions to meet the same audit and consent obligations.
How should Python handle PHI in application logs?
Never write raw PHI to any log sink. Use a custom logging filter that redacts fields like ssn, name, and birthDate before the record is emitted, and route logs to a HIPAA-eligible SIEM such as Splunk or Datadog. Test the filter with pytest assertions that scan CloudTrail events for forbidden substrings after each FHIR read or write.
Can open-source FHIR servers replace a managed Python stack?
Yes, but HAPI FHIR runs on Java and adds JVM DevOps overhead that slows AI/ML pipeline integration. Python with FastAPI and fhir.resources is lighter and pairs naturally with Hugging Face inference. Whichever you pick, the hosting environment must still carry a signed BAA, and open-source projects themselves never provide one.
What cloud providers will sign a BAA for PHI workloads?
AWS, Azure, and Google Cloud all offer BAAs covering their HIPAA-eligible service lists. Heroku, DigitalOcean, and most serverless-first platforms do not, which disqualifies them for production PHI regardless of feature fit. Verify that every managed service you use, including queues, caches, and AI endpoints, appears on the covered list before deployment.
How do FHIR backends support MEDDPICC qualification?
Audit logs become evidence for the Metrics and Decision Criteria dimensions. Logging every FHIR API call with user ID, resource type, and timestamp lets RevOps show reduced claim denials or faster prior authorizations. Piping those metrics into Clari or Salesforce Revenue Cloud gives buying committees concrete ROI data during eight-to-fourteen-month sales cycles.
What does a HIPAA-compliant FHIR backend actually cost?
Expect roughly $2,000 to $5,000 per month for cloud infrastructure on AWS or GCP, plus $500 to $1,000 monthly for audit and SIEM tooling. An initial compliance assessment typically runs $10,000 to $20,000. Costs scale with PHI volume, retention requirements, and how many subprocessors require separate BAAs and annual security reviews.
How do you test that PHI never leaks into logs?
Write pytest cases that trigger FHIR reads and writes, then pull the corresponding CloudTrail or Azure Monitor event and assert that sensitive substrings like SSN or birthDate never appear in requestParameters. Run TruffleHog for secret scanning in CI. Pair these with OWASP ZAP or Burp Suite scans against FHIR endpoints before every release.
Should AI inference run inside or outside the PHI boundary?
Run inference inside the BAA-covered boundary whenever the model touches identifiable data. If you must call an external model, de-identify the FHIR bundle first using a validated Safe Harbor or Expert Determination method, then re-associate results downstream. Document the de-identification step in your risk analysis, since auditors will ask for it.
FAQ
What is the minimum FHIR version for HIPAA compliance in 2027?
FHIR R5 is the practical baseline for new builds because it includes Provenance and Consent resources that support audit and authorization requirements natively. R4 still works for existing integrations but needs custom extensions to match the same obligations. Confirm your vendor's R5 support in writing before signing, since marketing pages often lag actual API coverage.
How do I handle PHI in Python logging?
Never log raw PHI. Use Python's logging module with a custom filter that redacts fields like ssn, name, and birthDate before emission, and ship logs only to a HIPAA-eligible SIEM. Add pytest assertions that scan CloudTrail events for forbidden substrings after each FHIR operation so regressions get caught in CI rather than in an audit.
Can I use open-source FHIR servers like HAPI FHIR instead of Python?
Yes, but HAPI FHIR is Java-based and adds JVM DevOps overhead that complicates AI/ML pipeline integration. Python with FastAPI and fhir.resources is lighter and pairs naturally with Hugging Face inference. Either way, the hosting environment must carry a signed BAA, because open-source projects themselves never provide one.
What happens if my cloud provider does not offer a BAA?
You cannot legally run PHI there. Stick to AWS, Azure, or GCP, all of which offer BAAs for their HIPAA-eligible service lists. Avoid Heroku, DigitalOcean, and most serverless-first platforms for production. Verify every managed service, including queues, caches, and AI endpoints, appears on the covered list before you deploy.
How do I integrate FHIR with Salesforce Health Cloud?
Use Salesforce's FHIR API via Python requests, mapping resources like Patient to Account and Observation to custom objects. Log sync status into Clari or Revenue Cloud so RevOps can track pipeline velocity against API usage. Confirm the Salesforce BAA covers Health Cloud and any Einstein features you enable before sending PHI across the boundary.
What is the cost of a HIPAA-compliant FHIR backend?
Expect $2,000 to $5,000 per month for cloud infrastructure on AWS or GCP, plus $500 to $1,000 monthly for audit and SIEM tooling. An initial compliance assessment typically runs $10,000 to $20,000. Costs scale with PHI volume, retention windows, and the number of subprocessors requiring separate BAAs and annual reviews.
How do AI agents fit into a HIPAA-compliant HealthTech backend?
AI agents can analyze FHIR bundles for no-show prediction or treatment adherence, but only inside the BAA-covered boundary or after validated de-identification. Expose FHIR $match and $everything operations through async FastAPI endpoints to handle inference throughput. Log every agent invocation with user ID and resource type so auditors can reconstruct exactly what data the model saw.
What audit logging does the HIPAA Security Rule require?
The Security Rule requires recording and examining activity in systems containing PHI. Practically, log every FHIR read, write, and search with user ID, timestamp, resource type, and action, and retain logs according to your documented policy. Route them to a SIEM like Splunk or Datadog and review alerts on a defined schedule, not just after an incident.
How do longer HealthTech sales cycles affect backend architecture?
Eight-to-fourteen-month cycles mean the backend must produce evidence continuously, not just at close. Audit trails, uptime history, and API usage metrics feed MEDDPICC qualification and satisfy compliance officers on the buying committee. Design logging and reporting early so RevOps can pull ROI proof on demand instead of scrambling mid-negotiation.
Is TLS 1.3 required for PHI transmission?
HIPAA does not name a specific TLS version, but the Security Rule requires guarding against unauthorized access during transmission. TLS 1.3 is the current best practice and satisfies auditors more easily than older versions. Use AWS Certificate Manager or Let's Encrypt for certificates, and disable fallback to TLS 1.1 or below on every endpoint.
Sources
- https://docs.aws.amazon.com/whitepapers/latest/hipaa/hipaa.html
- https://www.hhs.gov/hipaa/for-professionals/security/guidance/index.html
- https://www.hl7.org/fhir/
- https://cloud.google.com/security/compliance/hipaa
- https://learn.microsoft.com/en-us/azure/compliance/offerings/offering-hipaa-us
- https://www.hhs.gov/hipaa/for-professionals/privacy/guidance/de-identification/index.html
- https://owasp.org/www-project-top-ten/
- https://www.python.org/
Related on PULSE
This page will be disappearing soon. Save it to your device for $1 — or read it free while it is here.
@Kory-White- · if Venmo asks, the last 4 of my number are 2012
This page is gone.
This one is off the shelf now. $1 keeps it on your phone for good — the whole page, pictures and diagrams included.
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Remote Education Providers in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Real Estate Appraisers in 2027
 pulse-tech-stacksTop 10 E-commerce Platforms for Dropshipping Entrepreneurs in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Legal Tech Developers in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Litigation Support Firms in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Supply Chain Track-and-Trace Teams in 2027
 pulse-tech-stacksTop 10 Machine Learning Stacks for Fraud Detection Systems in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Early-Stage Fintech Startups in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for High-Frequency Trading Firms in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Mid-Size Museums in 2027