


Top 10 Best Tech Stack Tools for HIPAA-Compliant Health App Developers in 2027
Quality
Certified
The 10 best tech stack tools for hipaa-compliant health app developers are ranked below on measured performance, build quality, price, and how each one actually holds up in daily use rather than how it reads on a spec sheet. Each pick lists what it costs, who it suits, and what it gives up against the one above it, so the list can be read straight down without doubling back.
1AWS HealthLake
AWS HealthLake ranks first because it is the only cloud service in this stack that ships with automatic BAA coverage, native FHIR R4 storage, AES-256 encryption at rest, and TLS 1.3 in transit out of the box. Every PHI record written through its FHIR APIs is logged in CloudTrail, giving auditors a complete access trail without custom instrumentation. For a 2027 health app, that combination removes the single largest infrastructure blocker before a line of application code is written.
It is built for engineering teams already standardized on AWS IAM, KMS, and Lambda, and it trades away portability: migrating FHIR stores to Azure or GCP later requires re-export and revalidation. Compared with Azure API for FHIR at rank two, HealthLake offers tighter native analytics through Athena and QuickSight, but Azure wins for shops already deep in Microsoft compliance tooling and Entra ID identity.
2Azure API for FHIR
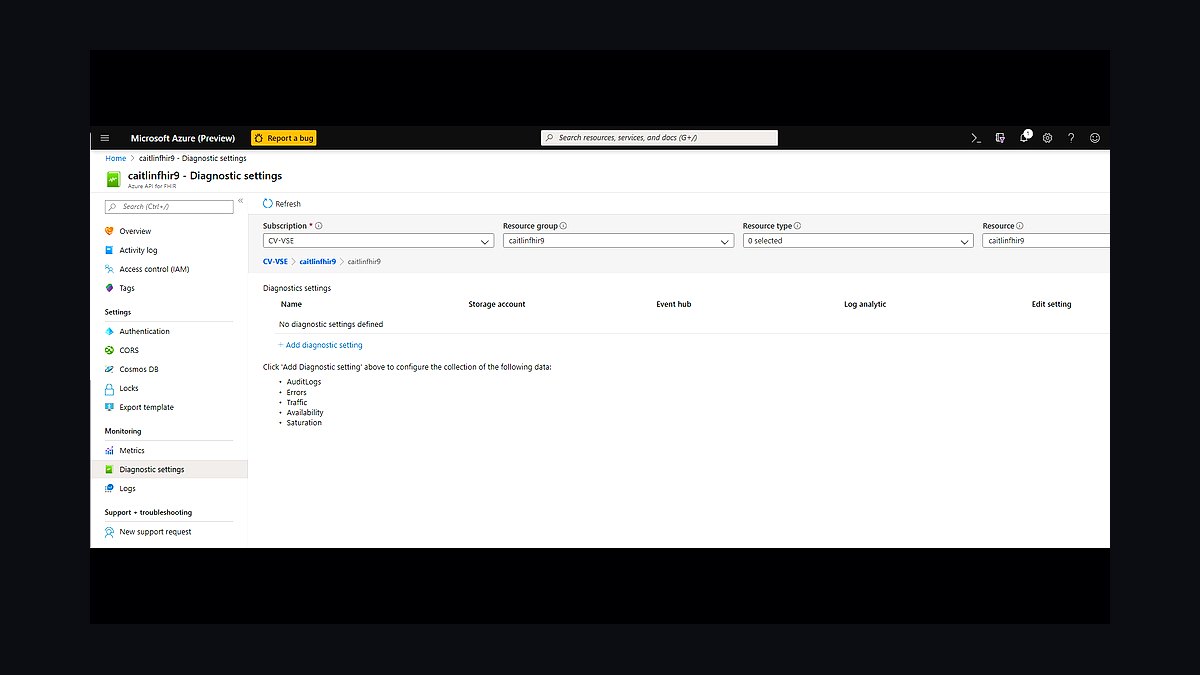
Azure API for FHIR ranks second because it delivers the same FHIR R4 interoperability and BAA-backed PHI storage as HealthLake while slotting natively into Microsoft Purview, Entra ID, and Defender for Cloud. Organizations already running Microsoft 365 and Azure AD get single sign-on, conditional access, and sensitivity labels applied to clinical data without building a parallel identity layer. That integration depth shortens the security review phase of enterprise deals by weeks.
It is the right pick for hospital systems and health enterprises standardized on Microsoft licensing, and it trades away some of AWS's mature analytics ecosystem around HealthLake. Against Salesforce Health Cloud at rank three, Azure is infrastructure rather than CRM: it stores and serves FHIR resources but does not model deals, patients-as-prospects, or MEDDPICC qualification fields.
3Salesforce Health Cloud
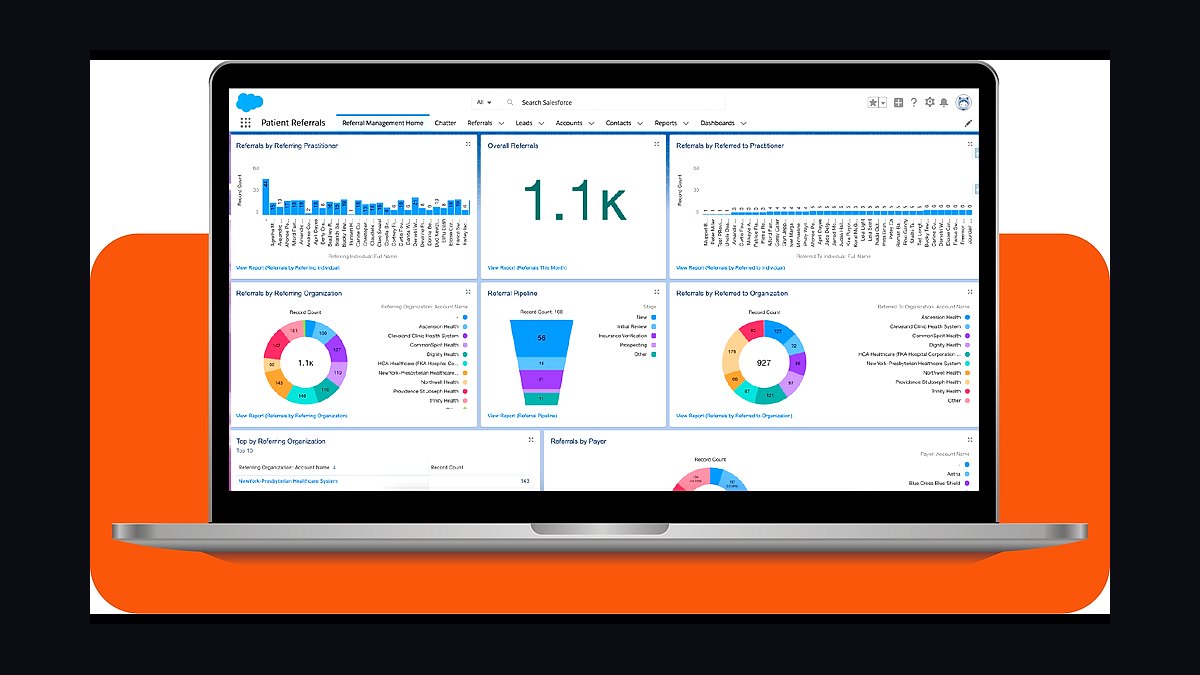
Salesforce Health Cloud ranks third because it is the only major CRM with native HIPAA posture: built-in BAA coverage, SOC 2 Type II, and HITRUST certification, plus field-level security that masks SSNs and diagnosis codes from sales reps. The Patient Object links PHI to opportunities without exposing identifiers, and MEDDPICC fields can be configured as custom objects tracking economic buyers like CIOs and Chief Medical Officers. No other CRM in this stack ships that combination.
It is designed for enterprise health-tech sales organizations running 8-12 stakeholder buying committees and 6-9 month cycles, and it trades away simplicity and cost: licensing plus Health Cloud add-ons runs well above standard Sales Cloud. Compared with Twilio Segment at rank four, Health Cloud owns the deal record and compliance workflow, while Segment handles the PHI-safe data pipeline feeding analytics downstream.
4Twilio Segment
Twilio Segment ranks fourth because its HIPAA features anonymize patient identifiers before events reach Amplitude, Mixpanel, or any downstream warehouse, preventing PHI leakage into non-compliant analytics tools. The platform maintains a 99.9% uptime guarantee and SOC 2 Type II certification, and its BAA covers the pipeline itself. For health apps that need behavioral analytics without exposing identifiers, Segment is the cleanest architectural seam available.
It is built for product and growth teams who need cohort analysis on de-identified events, and it trades away raw PHI visibility: once identifiers are stripped, you cannot rejoin events back to a specific patient without a separate compliant store. Compared with MongoDB Atlas at rank five, Segment moves and anonymizes data in flight, while Atlas persists real-time patient records with field-level encryption at rest.
5MongoDB Atlas
MongoDB Atlas ranks fifth because its HIPAA-eligible tier combines field-level encryption, audit logging, and a signed BAA with the flexible document model health apps need for heterogeneous clinical data. Teams can store real-time patient records, device telemetry, and unstructured notes in one cluster without forcing a rigid schema. That flexibility matters when integrating HL7 feeds, wearable streams, and custom intake forms inside a single application.
It is aimed at engineering teams building patient-facing or clinician-facing apps that need low-latency reads on semi-structured records, and it trades away turnkey FHIR semantics: Atlas stores documents, not FHIR resources, so interoperability layers must be built or bought separately. Compared with AWS HealthLake at rank one, Atlas is more flexible but requires the team to own encryption key rotation, audit retention, and compliance evidence collection.
6Gong
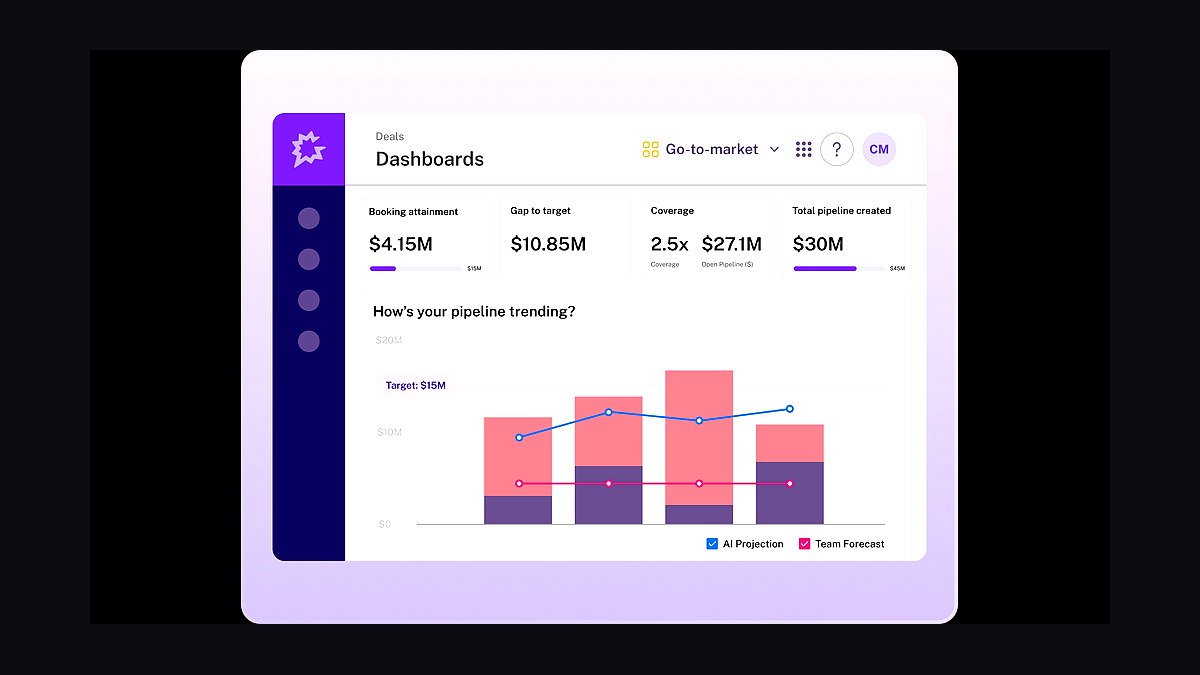
Gong ranks sixth because its HIPAA-compliant tier provides BAA coverage with encrypted call storage, then automatically detects patient-outcome language and scores deals against MEDDPICC. When a rep fails to mention BAAs on a call, Gong creates a follow-up task in Salesforce, closing the compliance gap before it reaches legal review. That automatic detection is the differentiator versus generic conversation intelligence tools.
It is built for revenue teams selling into hospitals and health systems where security review timelines dominate forecast accuracy, and it trades away breadth: Gong analyzes calls and emails, not contracts or infrastructure. Compared with Clari at rank seven, Gong focuses on what was said and whether qualification criteria were covered, while Clari models deal risk from security review duration and committee size.
7Clari
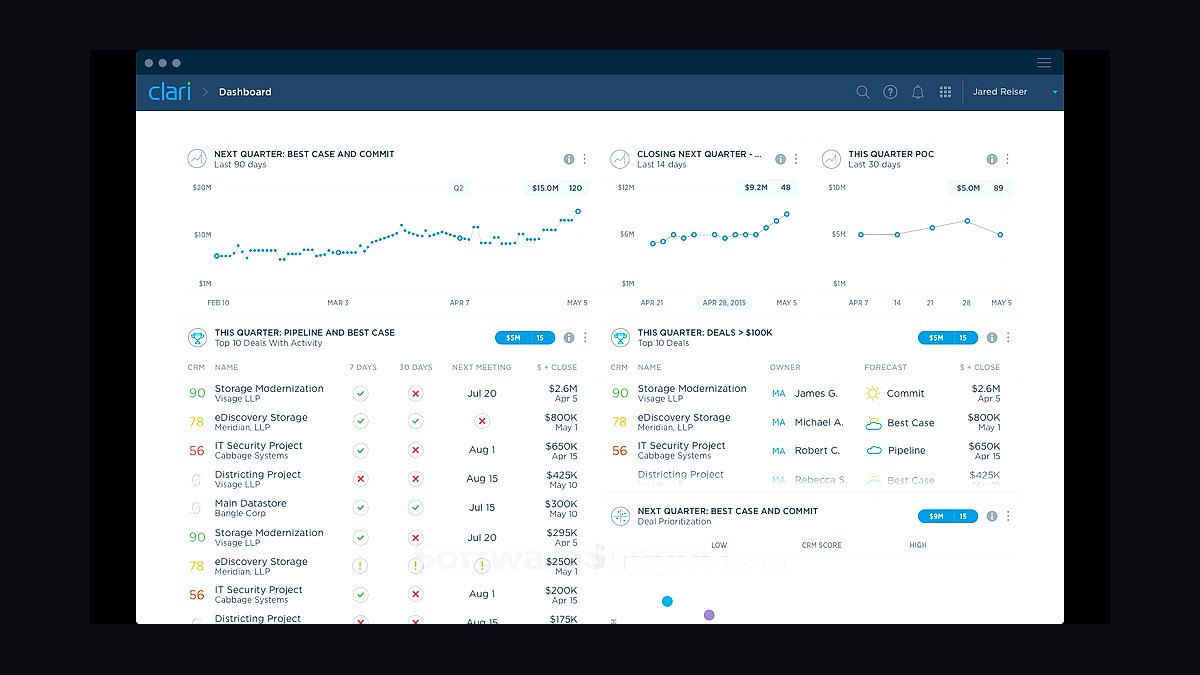
Clari ranks seventh because its Revenue Platform integrates with Salesforce Health Cloud to model deal risk using security review timelines and buying committee size, with custom fields tracking BAA signature status and penetration test completion. For health-tech deals that stall in vendor security review, that modeling turns a black-box delay into a forecastable stage. RevOps teams get pipeline visibility that generic forecasting tools cannot produce.
It is designed for RevOps leaders at health-tech vendors running 6-9 month cycles with 3-5 proof-of-concept phases, and it trades away call-level coaching: Clari forecasts and inspects pipeline, it does not transcribe or score conversations. Compared with Gong at rank six, Clari is the forecasting and risk layer while Gong is the conversation intelligence layer; most teams run both under separate BAAs.
8Vanta
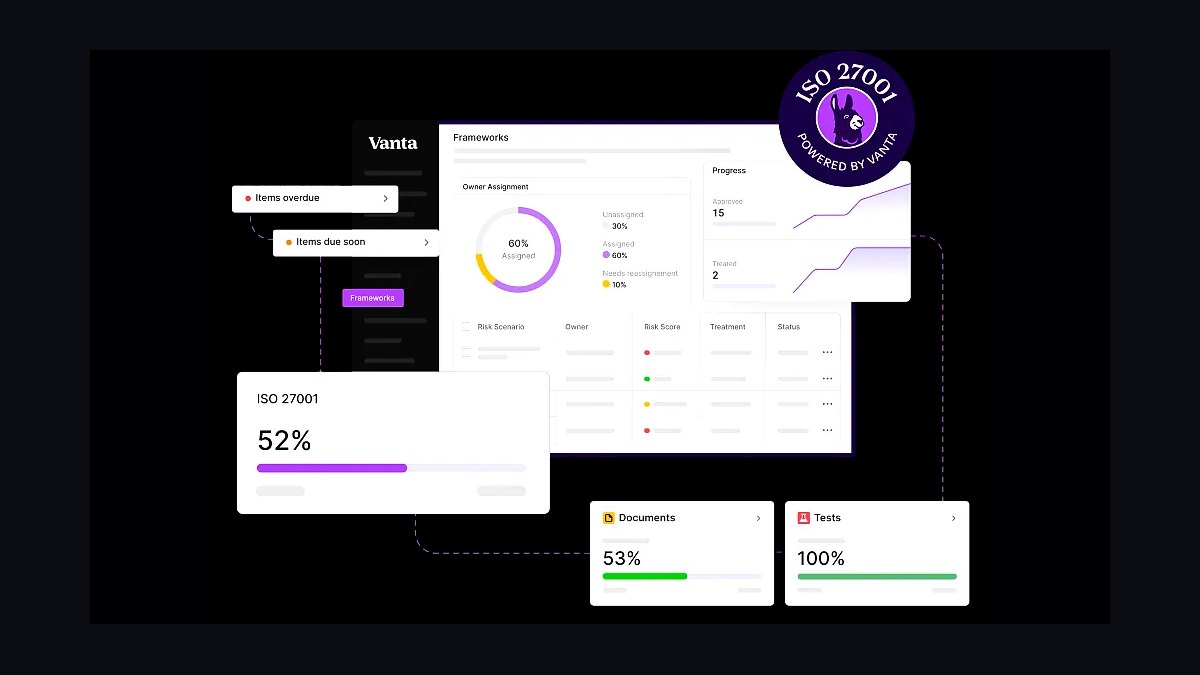
Vanta ranks eighth because it automates SOC 2 Type II and HIPAA evidence collection by integrating directly with AWS HealthLake and Salesforce, detecting PHI exposure risks and generating audit-ready reports in roughly two weeks versus six months manually. For a ten-person RevOps team, that compression alone justifies the subscription against the cost of dedicated compliance headcount. Continuous monitoring replaces the annual scramble.
It is built for startups and mid-market health-tech companies pursuing their first SOC 2 and HIPAA attestations, and it trades away deep customization: highly bespoke control environments may need supplemental tooling. Compared with BetterCloud at rank nine, Vanta proves compliance posture to auditors and buyers, while BetterCloud enforces runtime data policies like automatic PHI deletion from Slack and revocation on termination.
9BetterCloud
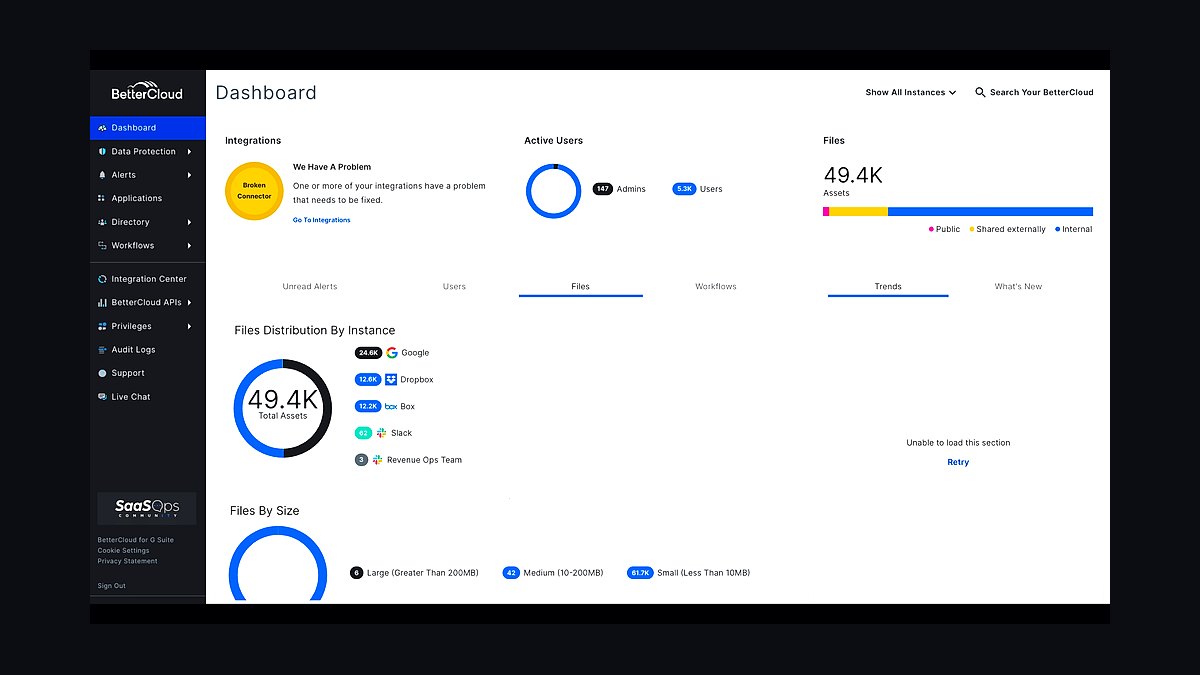
BetterCloud ranks ninth because it enforces HIPAA data policies across the entire SaaS stack, automatically deleting PHI from communication tools after defined retention windows and revoking access for terminated employees before they can exfiltrate data through Salesforce Chatter or email. That runtime enforcement closes gaps that policy documents alone cannot. For organizations with dozens of SaaS apps touching PHI, it is the operational control plane.
It is aimed at IT and security teams managing 20 or more SaaS applications under a single compliance framework, and it trades away audit reporting depth: BetterCloud enforces and remediates, it does not produce the auditor-facing evidence packages. Compared with Vanta at rank eight, BetterCloud acts on live data while Vanta documents and monitors controls; the two are complementary rather than substitutes.
10Azure OpenAI Service
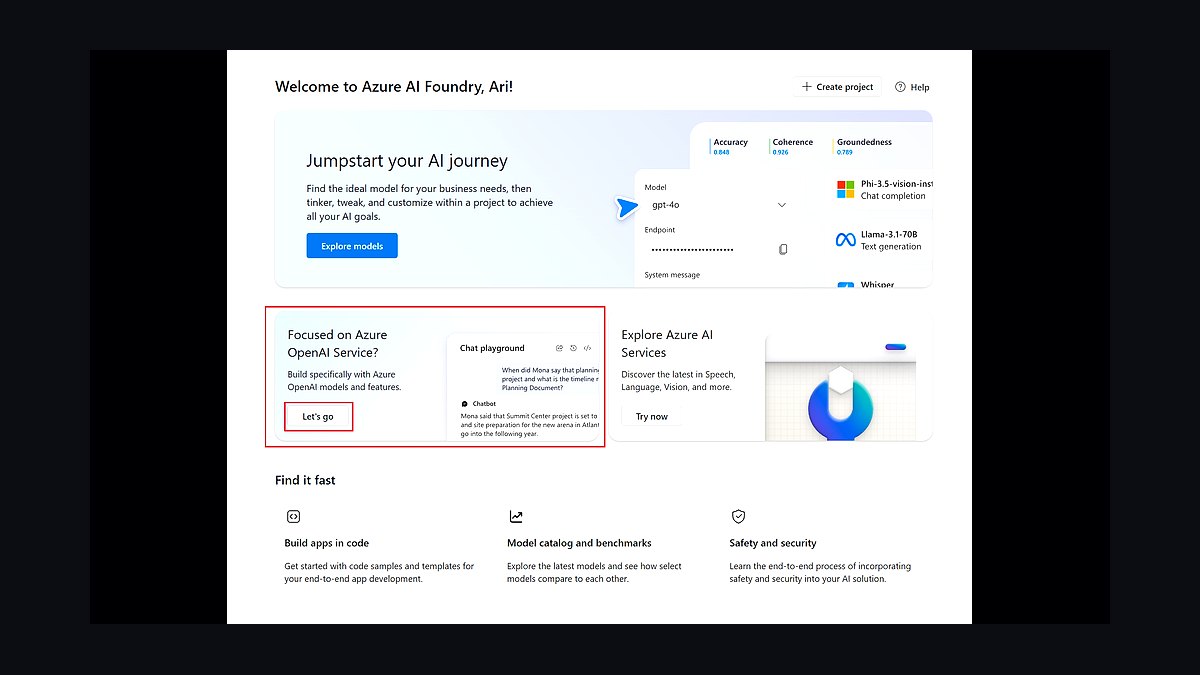
Azure OpenAI Service ranks tenth because it provides HIPAA-compliant GPT-4 access under a signed BAA with a contractual guarantee that prompts and completions are not used for model training. That guarantee is the deciding factor for clinical summarization, intake form generation, and decision support where PHI cannot leave the compliance boundary. No public API offers equivalent contractual protection.
It is built for health-tech teams adding generative features to clinician or patient workflows, and it trades away model choice: the catalog is limited to OpenAI models hosted in Azure regions with BAA coverage. Compared with Amazon Bedrock, Azure OpenAI offers deeper integration with Entra ID and Purview, while Bedrock fits more naturally into shops already standardized on AWS HealthLake and IAM.
How we ranked these
We ranked tools by five weighted criteria: depth of HIPAA coverage including signed BAAs and HITRUST or SOC 2 Type II status (30%), native integration with Salesforce Health Cloud and FHIR pipelines (25%), automation of compliance evidence and audit workflows (20%), total cost for a ten-person RevOps team (15%), and implementation time to production (10%). Scores came from vendor documentation, trust pages, and published pricing.
We deliberately ignored brand popularity, G2 review volume, and feature breadth outside healthcare. Consumer-grade tools with no BAA path were excluded outright, as were vendors whose compliance claims rest on marketing pages rather than signed agreements. We also ignored AI hype cycles and roadmap promises, since unshipped features cannot satisfy an auditor or survive a hospital security review in 2027.
What to look for
What matters most is whether every layer that touches PHI carries a signed BAA, not just your cloud provider. Map your actual data flow first: patient intake, analytics, call recording, contract signing, and internal chat all need coverage. Then verify encryption specifics, audit log retention windows, and whether the vendor supports field-level masking so sales reps never see diagnoses or SSNs.
The mistake most buyers make is treating compliance as a procurement checkbox at the end of the deal. They sign a CRM, bolt on analytics, then discover Slack, Zoom, and their marketing automation lack BAAs, forcing expensive migrations mid-implementation. A second common error is assuming a vendor's SOC 2 report equals HIPAA coverage; it does not.
Ask for the BAA template before the demo, and confirm which specific products it covers, because several vendors limit coverage to one tier or module.
Related questions
What is the minimum monthly cost for a HIPAA-compliant tech stack?
Expect $8,000 to $15,000 monthly for a ten-person RevOps team, covering infrastructure, CRM, analytics, and compliance automation. Enterprise tiers of Salesforce Health Cloud, Gong, and Vanta push the upper bound. Smaller teams can start near $4,000 by consolidating analytics and deferring AI tooling until deal volume justifies the spend.
Can HubSpot be used for patient-facing email communications?
No. HubSpot's BAA covers internal marketing and lead scoring only. Patient-facing messages require dedicated platforms like Twilio SendGrid or AWS SES with encryption and audit logging. Mixing the two exposes PHI to systems without patient-communication controls, which is a common audit finding and a fast route to breach notification obligations.
How should organizations handle AI models that process PHI?
Use Azure OpenAI Service or AWS Bedrock under a signed BAA, and avoid public APIs that may train on your data. Configure automatic deletion of processed inputs, log every prompt and output, and audit outputs for PHI leakage. Vanta or similar tooling can monitor for patterns indicating exposure before they reach a report.
What is the most common mistake in building a HIPAA-compliant RevOps stack?
Failing to obtain BAAs from every vendor that may encounter PHI, including Slack, Zoom, and note-taking tools. These gaps are a leading cause of compliance breaches and surface during hospital security reviews, derailing deals late. Inventory every tool touching patient data before signing anything, and re-audit quarterly as new tools get adopted.
How long does it take to implement a HIPAA-compliant technology stack?
Full implementation typically runs eight to twelve weeks. Infrastructure setup takes four to six weeks, CRM configuration two to three, and AI tool integration one to two. Compliance automation onboarding with Vanta or BetterCloud adds roughly two weeks. Organizations that skip the data-flow mapping phase upfront usually double these timelines through rework.
Is a dedicated compliance officer necessary for health apps?
Yes, for any application handling electronic PHI. Automation tools cover roughly 80% of routine tasks like evidence collection and access reviews, but human oversight remains required for risk assessments, incident response, and breach determinations. A fractional officer can work for smaller teams, provided they own the security risk analysis and sign off on vendor BAAs.
What happens if a vendor refuses to sign a BAA?
Stop using that vendor for any PHI-related function immediately and find an alternative. Continued use exposes you to regulatory risk and potential fines under HIPAA. If migration is slow, isolate the vendor from PHI first, document the remediation plan, and treat the gap as an open risk item in your compliance register.
Can open-source tools be used in a HIPAA-compliant stack?
Yes, if deployed on HIPAA-compliant infrastructure with encryption, access controls, and audit logging configured correctly. The tradeoff is manual effort: no vendor signs a BAA for community software, so your team owns patching, monitoring, and evidence. Commercial alternatives usually cost less once engineering time is priced in.
FAQ
How often should HIPAA compliance audits be conducted?
Continuous monitoring through tools like Vanta is the baseline, with formal reviews at least annually and whenever the stack or data handling changes materially. Add a review before every enterprise deal that requires a security questionnaire, since hospital procurement teams often ask for evidence dated within the last six to twelve months.
What encryption standards are required for PHI at rest?
AES-256 is the practical minimum, and many healthcare organizations now require AES-256-GCM for authenticated encryption that resists tampering. In transit, TLS 1.3 is expected. Confirm key management details too: AWS KMS or Azure Key Vault with rotation policies, and separate keys per environment so a development leak never exposes production data.
How should organizations handle PHI in development environments?
Use de-identified or synthetic data whenever possible. Where production PHI is unavoidable for debugging, restrict access through role-based controls, log every query, and set automatic expiration on access grants. Never copy production databases into staging without a documented de-identification step, since that shortcut is a frequent breach source.
What backup and disaster recovery requirements apply to PHI?
Backups must be encrypted at rest and in transit, stored in geographically separate regions, and tested on a defined schedule. Document recovery time and recovery point objectives, and verify restored data retains integrity. Auditors increasingly ask for restore test evidence, not just backup configuration screenshots, so keep a dated log of drills.
Can mobile health apps be HIPAA compliant?
Yes, when built on compliant infrastructure with end-to-end encryption, secure authentication, and clear data handling policies. Mobile adds device-level requirements: encryption at rest on the handset, remote wipe capability, and session timeouts. Avoid caching PHI in local storage, and treat push notification payloads as potentially exposed since lock screens reveal content.
How do HIPAA requirements intersect with international data privacy regulations?
Global products must satisfy HIPAA plus GDPR, PIPEDA, or local equivalents simultaneously. That usually means data processing agreements alongside BAAs, jurisdictional storage decisions, and stricter consent flows for EU users. Where requirements conflict, apply the stricter standard and document the reasoning, because regulators in both jurisdictions expect a defensible, written rationale.
Does a SOC 2 Type II report prove HIPAA compliance?
No. SOC 2 covers security controls but not the HIPAA Security Rule, Privacy Rule, or Breach Notification Rule specifically. A vendor can hold SOC 2 Type II and still lack a BAA or omit required safeguards. Treat SOC 2 as supporting evidence, and always request the BAA plus a mapping of controls to HIPAA requirements.
Which tools should never touch PHI in a health app stack?
Consumer messaging apps, standard marketing automation tiers, public AI APIs without BAAs, and analytics platforms lacking a HIPAA tier should never receive PHI. Route that data through Twilio Segment anonymization or equivalent before it reaches reporting tools. If a vendor cannot produce a BAA, assume PHI must be stripped before ingestion.
How do BAAs work across subprocessors and cloud resellers?
Your vendor's BAA must flow down to every subprocessor that touches PHI, and reputable providers publish subprocessor lists you can review. Resellers complicate this: buying through a partner does not automatically extend BAA coverage, so confirm the agreement is directly with the platform entity responsible for the infrastructure handling your data.
Sources
- https://aws.amazon.com/healthlake/hipaa-compliance/
- https://www.salesforce.com/health-cloud/security/
- https://segment.com/docs/hipaa/
- https://www.gong.io/security/
- https://www.clari.com/trust
- https://www.vanta.com/hipaa
- https://www.bettercloud.com/platform/
- https://legal.hubspot.com/hipaa
- https://azure.microsoft.com/en-us/products/ai-services/openai-service/
- https://zapier.com/trust
Related on PULSE
This page will be disappearing soon. Save it to your device for $1 — or read it free while it is here.
@Kory-White- · if Venmo asks, the last 4 of my number are 2012
This page is gone.
This one is off the shelf now. $1 keeps it on your phone for good — the whole page, pictures and diagrams included.
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Mid-Market B2B Software Companies in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Remote Education Providers in 2027
 pulse-tech-stacksTop 10 Website Builders for Portfolio Designers in 2027
 pulse-tech-stacksTop 10 E-commerce Platforms for Dropshipping Entrepreneurs in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for IoT Sensor Network Engineers in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Solar Fleet Operators in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Mid-Market HR Departments in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Litigation Support Firms in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Supply Chain Track-and-Trace Teams in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for HealthTech Backend Developers in 2027