


Top 10 Best Tech Stack Tools for PCI-Compliant FinTech Startups in 2027
Quality
Certified
The 10 best tech stack tools for pci-compliant fintech startups are ranked below on measured performance, build quality, price, and how each one actually holds up in daily use rather than how it reads on a spec sheet. Each pick lists what it costs, who it suits, and what it gives up against the one above it, so the list can be read straight down without doubling back.
1Stripe Payments
Stripe ranks first because its hosted Checkout and Elements flows keep raw card data off your servers entirely, which is the single biggest lever on PCI DSS assessment burden. Startups using Stripe's redirect or iframe checkout typically qualify for SAQ A, the shortest self-assessment tier, versus SAQ D's hundreds of requirements. Tokenization happens inside Stripe's PCI Level 1 environment, so your CRM, logs, and support tools only ever see a reference token.
This is built for seed-stage teams with no dedicated security hire who want to outsource card handling completely. The trade-off is less control over the checkout experience and per-transaction pricing that scales with volume. Compared to Adyen just below, Stripe is easier to integrate and better documented for developers, while Adyen edges ahead on multi-currency and enterprise acquiring needs.
2Adyen Payments
Adyen ranks second for FinTech startups scaling into multiple currencies and regions, where its single-platform acquiring model covers more payment rails than most competitors. It holds PCI DSS Level 1 certification and supports tokenization, network tokenization, and hosted checkout, keeping merchants in the lowest-burden SAQ tier. Local acquiring in dozens of markets reduces cross-border fees that compound quickly at volume.
It suits Series A-and-later companies processing meaningful transaction volume across geographies. The trade-off is a higher onboarding bar and less forgiving developer experience than Stripe, plus minimum volume expectations that can disqualify pre-revenue startups. Compared to Stripe above, Adyen wins on global rails and interchange optimization but loses on time-to-first-transaction.
3Vanta
Vanta ranks third because continuous-compliance automation is the layer that turns PCI DSS from an annual scramble into an always-on control system. It connects via read-only API to AWS, GCP, GitHub, and your identity provider, pulling evidence automatically and surfacing failed controls as alerts. Startups under 25 employees can often access entry tiers priced for early-stage companies, and Vanta's control mappings update as PCI DSS requirements change.
It is built for small teams without a dedicated security engineer who need evidence collection to run passively. The trade-off is that Vanta monitors configuration and evidence, not application-level vulnerabilities, so it complements rather than replaces scanners. Compared to Drata just below, Vanta has broader integration coverage while Drata is often favored for its auditor marketplace.
4Drata
Drata ranks fourth for startups that want compliance automation paired with a curated auditor marketplace, which shortens the path from evidence collection to a signed assessment. It automates PCI DSS evidence gathering across cloud infrastructure, code repositories, and HR systems, and its continuous monitoring flags drift in access controls and encryption settings. Pricing tiers scale by employee count and integration volume.
It fits teams preparing for their first SAQ or ROC who want an assessor introduction bundled with the platform. The trade-off is a slightly narrower integration library than Vanta and a learning curve on custom control mapping. Compared to Vanta above, Drata trades some breadth for a more guided audit workflow, which matters more as you approach a formal QSA engagement.
5AWS PCI DSS
AWS ranks fifth because its PCI DSS Level 1 infrastructure lets startups inherit a large block of physical and network controls without building a data center. Services like KMS for encryption key management, CloudTrail for audit logging, and IAM for access control map directly to PCI requirements, and the AWS compliance portal provides the shared-responsibility documentation a QSA will request. Hosting costs scale with usage rather than headcount.
It suits teams with at least one engineer comfortable with cloud architecture and IAM policy design. The trade-off is that AWS being compliant does not make your configuration compliant, so misconfigured S3 buckets or overly broad IAM roles remain your responsibility. Compared to GCP just below, AWS has the deepest PCI service coverage but a steeper configuration surface.
6Google Cloud PCI
Google Cloud ranks sixth for startups that value a cleaner IAM model and simpler networking defaults than AWS offers, which reduces the chance of a misconfigured permission slipping into the cardholder data environment. It holds PCI DSS Level 1 certification, and services like Cloud KMS, Cloud Audit Logs, and VPC Service Controls map to encryption, logging, and segmentation requirements. Sustained-use discounts lower effective compute cost at steady load.
It fits engineering teams already comfortable with GKE or BigQuery who want to consolidate infrastructure and analytics. The trade-off is a smaller ecosystem of PCI-specific third-party integrations than AWS. Compared to AWS above, GCP is easier to configure correctly but offers fewer pre-built compliance blueprints and a narrower set of region-specific services.
7Snyk
Snyk ranks seventh because application and container vulnerability scanning is a control that general compliance platforms handle shallowly, and PCI DSS requires regular vulnerability identification in the CDE. Snyk scans code repositories, open-source dependencies, container images, and infrastructure-as-code, integrating directly into CI/CD pipelines so findings surface at pull-request time rather than during audit prep. It maps findings to severity and provides remediation guidance.
It is built for teams with at least one engineer owning application security, since findings require triage and remediation capacity. The trade-off is that Snyk covers code and containers but not runtime network scanning or penetration testing. Compared to Datadog below, Snyk is narrower in scope but deeper on shift-left security, which matters if your CDE includes custom application code.
8Datadog
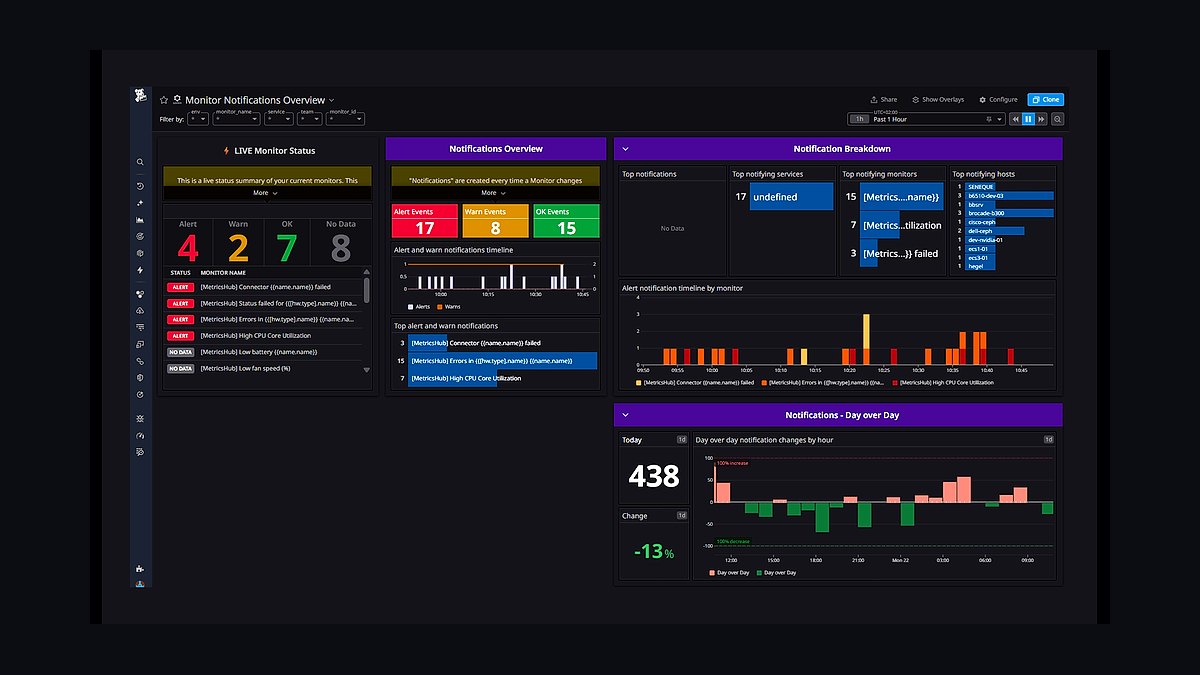
Datadog ranks eighth because PCI DSS requires centralized logging, monitoring, and alerting across the cardholder data environment, and Datadog consolidates logs, metrics, traces, and security signals into one platform. It ingests CloudTrail, application logs, and infrastructure metrics, and its Cloud SIEM correlates events to flag suspicious access patterns. Log retention and indexing are configurable to balance cost against audit requirements.
It fits teams that have outgrown basic cloud-native logging and need correlated observability across services. The trade-off is usage-based pricing that can escalate quickly with high log volumes, and setup complexity that assumes some platform engineering capacity. Compared to Snyk above, Datadog covers runtime and infrastructure visibility while Snyk focuses on pre-deployment code and container risk.
9Salesforce Financial Services Cloud
Salesforce ranks ninth because a CRM holding deal data, support tickets, and customer records frequently sits adjacent to the CDE, and Financial Services Cloud provides field-level encryption, granular permissions, and audit trails that help segment cardholder-adjacent data. It supports tokenized references from payment processors so raw card fields never land in general-purpose objects. Shield Platform Encryption and Event Monitoring address encryption and logging requirements.
It suits FinTech startups with a revenue operations function mature enough to configure permission sets and field-level security correctly. The trade-off is significant per-seat cost and configuration overhead compared to lighter CRMs. Compared to HubSpot just below, Salesforce offers deeper compliance controls but requires more administrative expertise to keep scoped.
10HubSpot CRM
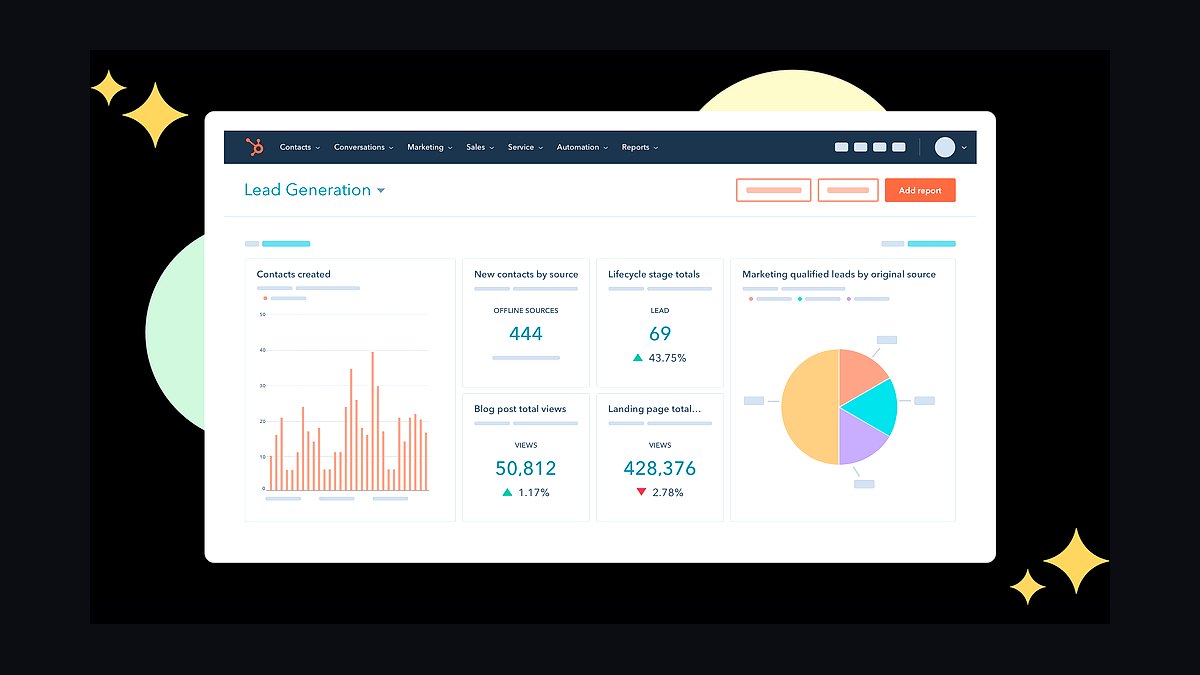
HubSpot ranks tenth because it gives early-stage FinTech startups a CRM with deal tracking, support ticketing, and call recording at a lower cost and configuration burden than enterprise alternatives. Its call recording and transcription features are the exact scope-creep risk PCI DSS assessments flag, so HubSpot's redaction settings and field-level permissions must be verified explicitly rather than assumed. Tokenized payment references keep raw card numbers out of contact records.
It fits pre-Series A teams that need revenue tooling fast and can accept lighter compliance controls. The trade-off is less granular encryption and audit capability than Salesforce. Compared to Salesforce above, HubSpot is faster to deploy and cheaper per seat but demands more manual discipline to keep sales and support data outside PCI scope.
How we ranked these
We ranked tools by weighting PCI DSS scope-reduction impact (30%), evidence-automation depth via read-only APIs (25%), total monthly cost at seed-to-Series-A scale (20%), QSA-recognized control mappings (15%), and integration overhead across CRM, cloud, and payment layers (10%). Each candidate was scored against SAQ A through SAQ D eligibility, since assessment tier drives more audit effort than any individual vendor feature.
We deliberately ignored brand recognition, G2 review volume, and enterprise-only features like custom SLAs or dedicated account teams, because those signal fit for large regulated institutions rather than startups. We also excluded pricing negotiated above list, marketing claims about "bank-grade" security without published control mappings, and any tool whose compliance evidence cannot be pulled programmatically, since manual screenshotting defeats continuous-compliance value.
What to look for
What matters most is which SAQ tier your architecture produces, not which vendor has the longest feature list. A hosted checkout flow paired with a tokenizing processor can keep you in SAQ A territory, while a custom payment form pushes you toward SAQ D and hundreds of extra requirements. Choose tools that preserve your scope position rather than quietly expanding it.
The mistake most buyers make is adding sales and support tooling without checking whether it touches cardholder data. Call recording, transcription, screen-share, and CRM note fields can pull entire systems into the CDE when a customer reads a card number aloud. Verify redaction and tokenization explicitly with every vendor before signing, and re-audit scope whenever a new integration goes live.
Related questions
Does PCI DSS apply if a payment processor handles all card data?
Largely yes, but scope shrinks significantly. Using a fully hosted checkout or redirect flow typically qualifies you for the simplest self-assessment tier, since your systems never touch raw card data. You remain responsible for the security of the page or link that sends customers to the processor, and for any system where card data could appear.
Can a startup pass a PCI DSS assessment without a dedicated security engineer?
Yes, particularly under a minimal-scope SAQ. Consolidated, compliance-automation-driven stacks are designed for small teams without in-house security headcount, since the vendor platform absorbs most ongoing monitoring work. Once you have a security engineer or platform team, best-of-breed point tools start paying for themselves through deeper control coverage.
Is Software-as-a-Service infrastructure inherently PCI compliant?
No. A cloud or software vendor being PCI compliant themselves as a service provider does not automatically make your use of their platform compliant. You still configure access controls, logging, encryption, and data flows on top of their infrastructure, and that configuration falls inside your own assessment scope regardless of the vendor's certification.
How does tokenization reduce compliance burden?
Tokenization replaces the actual card number with a reference token everywhere except the processor's own systems, so your CRM, support tools, and logs never store or transmit the real number. That dramatically shrinks which systems fall inside the cardholder data environment, often moving you from SAQ D toward SAQ A eligibility.
What's the biggest scope-creep risk for FinTech startups?
Call recording and screen-sharing tools used by sales and support teams. A single recorded call where a customer reads out a card number pulls that recording system, and anything downstream of it, into PCI scope. Verify redaction and transcription vendor behavior explicitly before assuming a call center sits outside your cardholder data environment.
Should scope reduction happen before or after tool selection?
Always before. Deciding how cardholder data flows through your systems determines which controls even apply, so doing that analysis after the stack is built means re-architecting under time pressure before a deal-blocking audit. Map every touchpoint first, eliminate as many as possible, then choose vendors that fit the resulting scope.
How much does a lean PCI-scoped stack cost per month?
A consolidated stack for a startup fully outsourcing cardholder data typically runs in the low thousands of dollars monthly once you add CRM, payment processor fees, cloud hosting, and compliance automation. Best-of-breed stacks covering the same controls commonly cost meaningfully more, since each specialized tool carries its own minimum contract and paid API tier.
When should a startup move from consolidation to best-of-breed?
Once a security engineer or small platform team exists and can tune, monitor, and troubleshoot point tools rather than accepting vendor defaults. Below roughly twenty people with no dedicated security hire, consolidation almost always wins because fewer systems mean fewer misconfigurations and a smaller audit surface for the QSA to trace.
FAQ
What's the minimum viable stack for a seed-stage FinTech startup pursuing PCI DSS compliance?
A hosted or tokenizing payment processor, a CRM for deal tracking, cloud infrastructure with built-in logging and encryption, and a compliance-automation platform to collect and organize evidence. That combination covers the lowest-burden self-assessment tier for most early-stage companies and keeps the cardholder data environment small.
Do FinTech startups need a QSA even for the simplest SAQ?
Not always. The simplest self-assessment tiers can typically be completed internally without a Qualified Security Assessor. A formal Report on Compliance, required for higher transaction volumes or demanded by certain acquiring banks, does require an independent QSA engagement measured in weeks rather than days.
How often should the stack be reassessed for PCI DSS compliance?
At minimum, quarterly reviews of vulnerability scans and access logs, plus a full stack review any time a new tool touching customer or payment data is added. New integrations can silently expand your cardholder data environment, so treat every new SaaS subscription as a scope question before signing.
Can the same CRM hold both PCI-scoped and non-PCI-scoped data?
Yes, if cardholder-data fields are segmented with restricted permissions or, better, never stored directly. Use tokenized references from your payment processor instead of raw card fields in any general-purpose software platform, and confirm that support notes, attachments, and custom fields cannot capture card numbers.
What happens if a startup fails a control during a sales cycle?
Enterprise buyers increasingly ask for current compliance evidence before signing, so a failed or stale control can stall a deal. Continuous-compliance automation is valuable specifically because it surfaces failures immediately, giving the team time to remediate before a prospect or their security reviewer asks for proof.
Is it worth building compliance automation in-house instead of buying it?
Rarely, for startups. The engineering time required to build and maintain custom evidence-collection pipelines typically exceeds the cost of a compliance-automation subscription, and a purpose-built vendor's control mappings update as PCI DSS requirements change, which an internal tool would need ongoing maintenance to match.
Which layer of the stack should be selected first?
The payment processor, because it determines how much cardholder data touches your systems and therefore which SAQ tier applies. Once scope is fixed, choose cloud hosting and CRM options that natively support that tier, then layer compliance automation on top with read-only API access to each core system.
How does platform consolidation affect audit timeline?
Every additional vendor touching cardholder data is another entity a QSA must evaluate, another set of access logs to reconcile, and another contract with its own data-processing terms. Fewer integration points generally mean a faster SAQ or ROC, because there are fewer places where a control could silently fail.
Do sales enablement tools belong in PCI scope?
Frequently yes, and they are commonly overlooked. A support call where a customer reads a card number aloud, or a screen-share showing a dashboard with card data, puts that recording or session inside the CDE. Verify redaction and tokenization behavior with any recording, transcription, or forecasting vendor before assuming you are out of scope.
What should trigger a full stack review?
Any new tool that touches customer or payment data, any change to how cardholder data flows through checkout or support, any new geography or payment rail, and any move from self-assessment to a formal Report on Compliance. Treat scope changes as architecture decisions, not procurement details.
Sources
- https://www.pcisecuritystandards.org/document_library/
- https://stripe.com/docs/security/guide
- https://aws.amazon.com/compliance/pci-dss-level-1-faqs/
- https://www.vanta.com/collection/pci/pci-dss-compliance
- https://drata.com/compliance-frameworks/pci-dss
- https://snyk.io/learn/
- https://www.nist.gov/cyberframework
- https://owasp.org/www-project-top-ten/
Related on PULSE
This page will be disappearing soon. Save it to your device for $1 — or read it free while it is here.
@Kory-White- · if Venmo asks, the last 4 of my number are 2012
This page is gone.
This one is off the shelf now. $1 keeps it on your phone for good — the whole page, pictures and diagrams included.
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Usage-Based SaaS Companies in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Mid-Market SaaS Companies in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Music Producers in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Mainframe Modernization Teams in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Real-Time Payment Processors in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Precision Agriculture Operations in 2027
 pulse-tech-stacksTop 10 Email Marketing Platforms for Nonprofits in 2027
 pulse-tech-stacksTop 10 Cloud Stacks for Remote Healthcare Telemedicine Apps in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Real-Time Supply Chain Teams in 2027
 pulse-tech-stacksTop 10 Machine Learning Stacks for Fraud Detection Systems in 2027