


Top 10 Best Tech Stack Tools for Identity and Access Management (IAM) Teams in 2027
Quality
Certified
The 10 best tech stack tools for identity and access management (iam) teams are ranked below on measured performance, build quality, price, and how each one actually holds up in daily use rather than how it reads on a spec sheet. Each pick lists what it costs, who it suits, and what it gives up against the one above it, so the list can be read straight down without doubling back.
1Okta Workforce Identity
Okta ranks first because it carries the largest pre-built SaaS connector library in IAM, with more than 2,000 integrations, which matters most for Salesforce- and HubSpot-heavy revenue stacks. Its Workflows low-code engine handles just-in-time guest provisioning and bulk revocation when a deal closes lost. Okta AI generates access policies from natural language and auto-remediates violations during quarterly SOC 2 certifications.
It fits mid-market and enterprise teams whose application estate is mostly cloud SaaS rather than on-premise. The trade-off is per-user cost, which runs higher than bundling Entra ID inside an existing Microsoft agreement, and its native PAM module is less mature than dedicated tools. Compared with Microsoft Entra ID directly below, Okta wins on third-party app coverage but loses on Microsoft-first licensing economics.
2Microsoft Entra ID
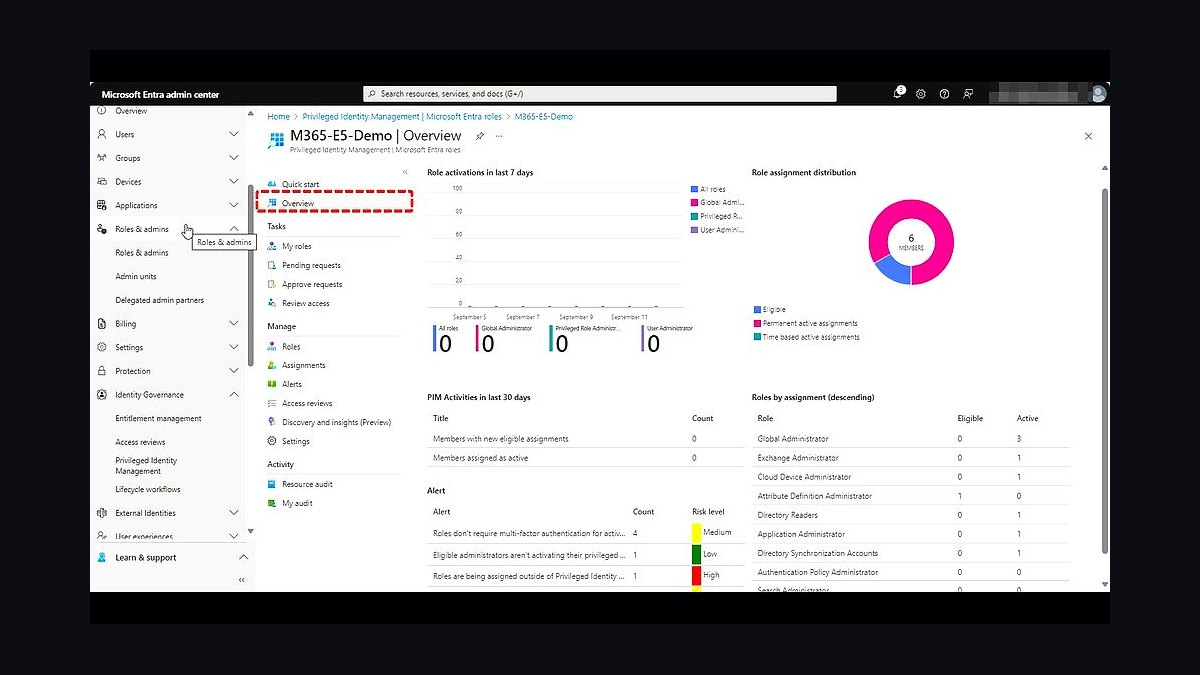
Microsoft Entra ID ranks second because it bundles access management, identity governance, and native privileged access management into licensing most enterprises already own. Entra Verified ID issues decentralized credentials for B2B buying committees, and External ID auto-provisions temporary guest tokens that expire on schedule. Security Copilot investigates identity incidents and drafts conditional access policies, cutting response time substantially.
It suits Microsoft-first organizations, government agencies, and anyone needing FedRAMP coverage. The trade-off is licensing complexity: full governance and PAM features generally require E5, and non-Microsoft application integration is less flexible than Okta's catalog. Against Ping Identity below, Entra is cheaper for Azure-centric shops but weaker for hybrid on-premise and regulated environments.
3Ping Identity PingOne
Ping Identity ranks third because its PingOne risk engine scores every session on device posture, network telemetry, and behavioral baselines, then downgrades suspicious sessions to read-only automatically. It supports hybrid deployments spanning on-premise and cloud, which the two platforms above handle less gracefully. DaVinci orchestration lets teams build custom identity flows without replacing the underlying directory.
It is built for financial services, healthcare, and regulated industries where data residency and legacy systems rule out pure-cloud vendors. The trade-offs are a smaller connector ecosystem of roughly 800 integrations and higher implementation complexity. Against Okta above, Ping sacrifices breadth of SaaS coverage for depth in risk scoring and hybrid control.
4CyberArk Privileged Access Management
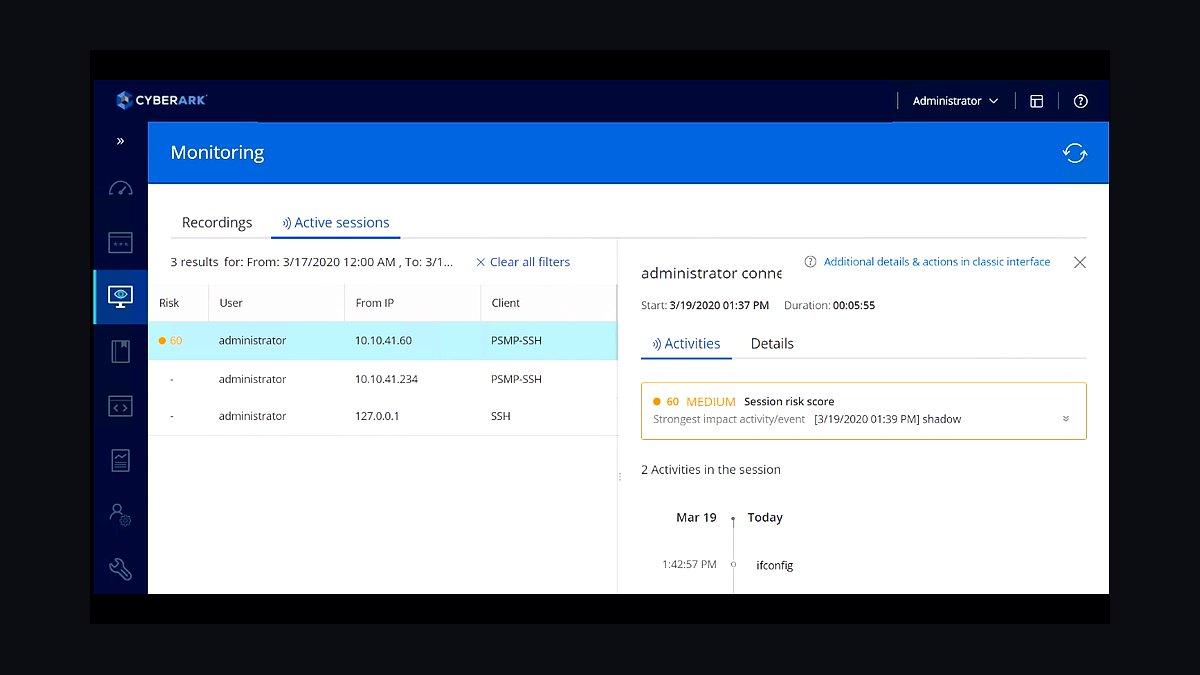
CyberArk ranks fourth because it remains the reference standard for privileged access management in environments where native PAM modules are insufficient. Its vaulting, session isolation, and credential rotation cover on-premise legacy systems, mainframes, and database accounts that cloud-native modules often cannot reach. Session recording captures privileged commands for audit evidence in PCI-DSS and SOX reviews.
It is for organizations with strict compliance mandates or substantial on-premise infrastructure, not lean SaaS-only teams. The trade-off is cost and operational overhead: a separate platform, separate agents, and separate administration. Against Microsoft Entra ID above, CyberArk delivers deeper privileged controls but adds a vendor and integration layer that consolidation-minded teams are actively trying to remove.
5BeyondTrust Privileged Remote Access
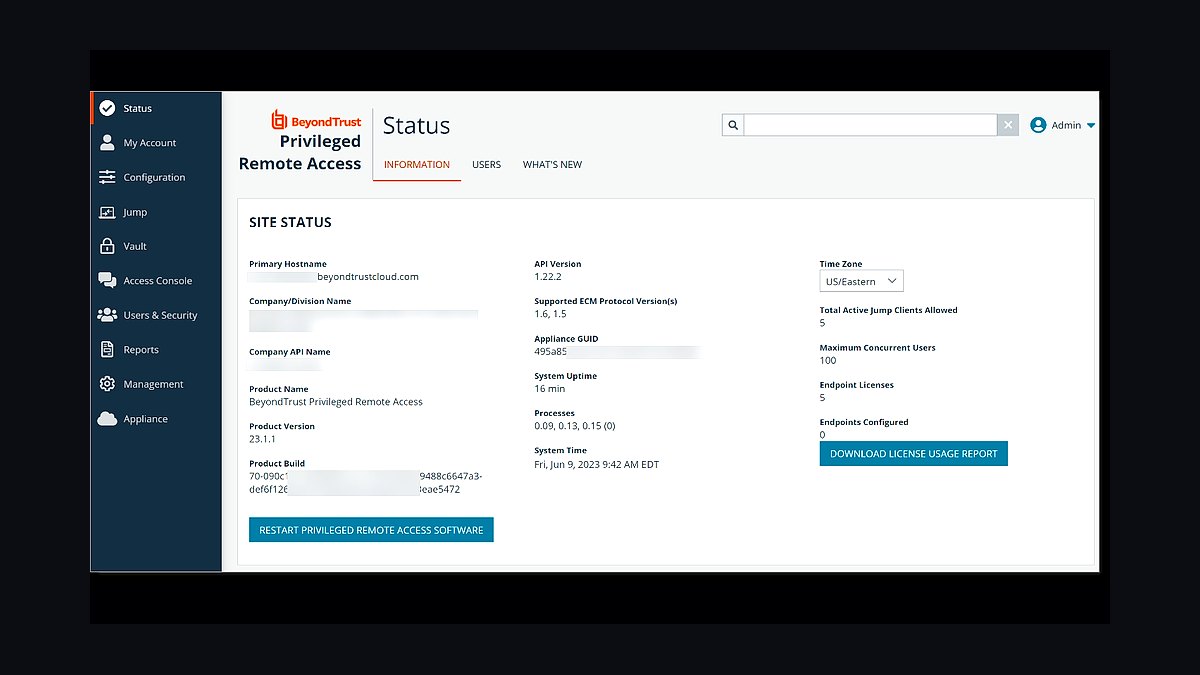
BeyondTrust ranks fifth because its privileged remote access product combines credential vaulting with brokered remote sessions, removing the need to expose internal systems to vendors and contractors. Least-privilege policy enforcement and session monitoring apply to third-party access, which matters when external buying committees and integrators touch production-adjacent systems. Deployment supports both cloud and on-premise targets.
It fits regulated enterprises and managed service providers that grant standing access to outside parties. The trade-off is that BeyondTrust overlaps heavily with CyberArk above, so running both is redundant for most teams. Compared with CyberArk, BeyondTrust is often favored for third-party remote access scenarios, while CyberArk leads on broad vaulting of machine and application credentials.
6Microsoft Entra Verified ID
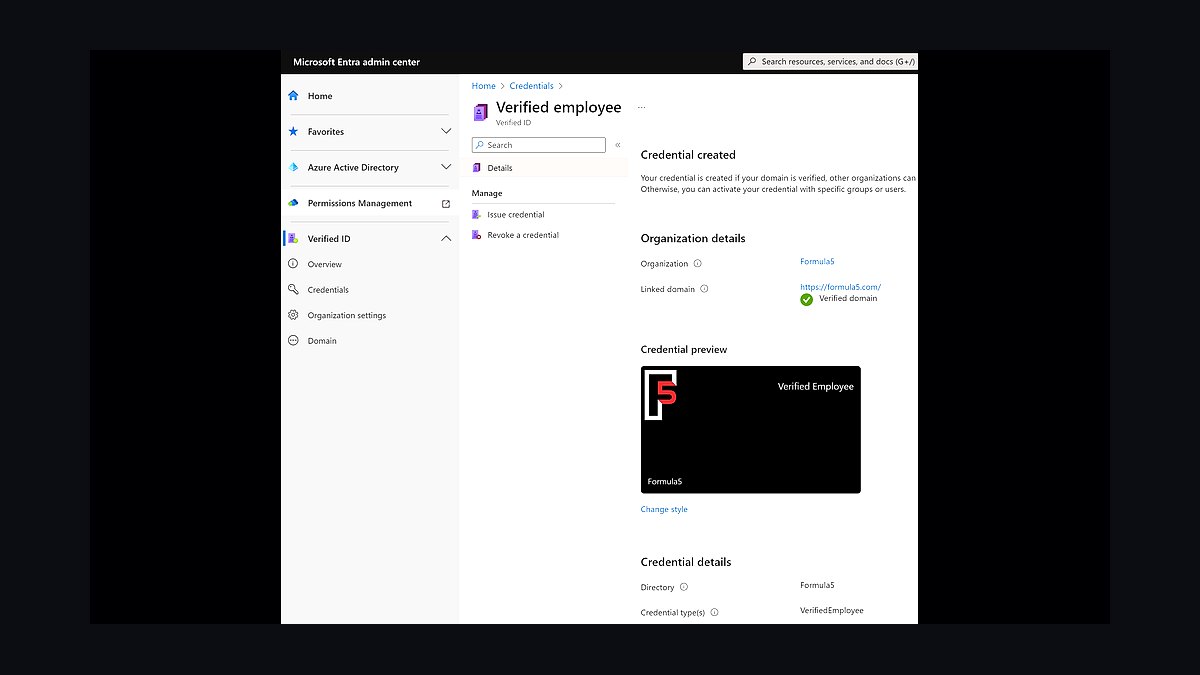
Microsoft Entra Verified ID ranks sixth because it issues cryptographically signed, decentralized credentials that let external buying committee members authenticate without creating new accounts. Verification of issuer and revocation status happens through a verifiable data registry, and credentials work across Slack, Zoom, and Salesforce. Provisioning delays drop from days to minutes for temporary collaborators.
It is for organizations running Microsoft-centric B2B collaboration at scale, particularly where audit trails must prove who accessed what. The trade-off is dependence on the Microsoft ecosystem and wallet adoption by external parties, which is uneven. Against PingOne above, Verified ID is narrower in scope but far simpler to deploy when Entra ID is already the primary directory.
7Okta Identity Governance
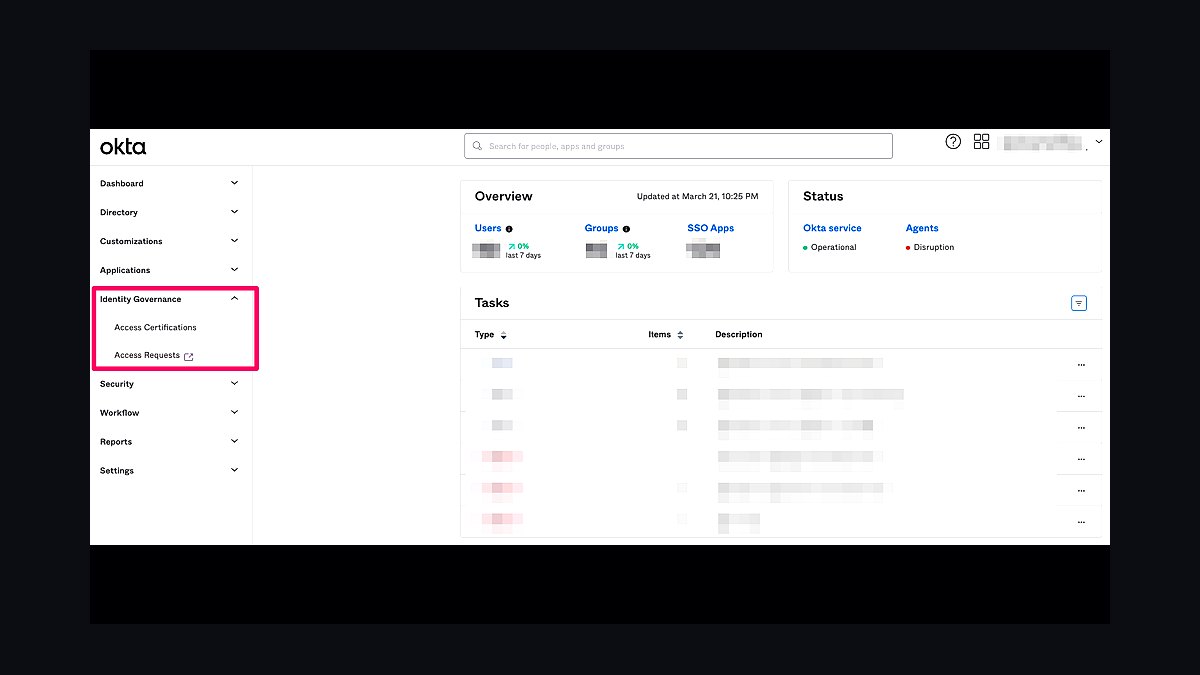
Okta Identity Governance ranks seventh because it automates access certifications with generative AI that flags anomalous role assignments before reviewers see them. It scans access patterns across Salesforce, Workday, and NetSuite, surfacing stale accounts and revoking access automatically. Quarterly SOC 2 and ISO 27001 certification cycles compress from weeks of manual review to days of exception handling.
It is for compliance-heavy teams already standardized on Okta Workforce Identity, where governance is an add-on rather than a separate platform. The trade-off is that it only makes sense inside the Okta ecosystem, and standalone IGA specialists often go deeper on role mining. Against Okta Workforce Identity above, this module adds governance depth but cannot be adopted independently.
8Ping Intelligent Identity
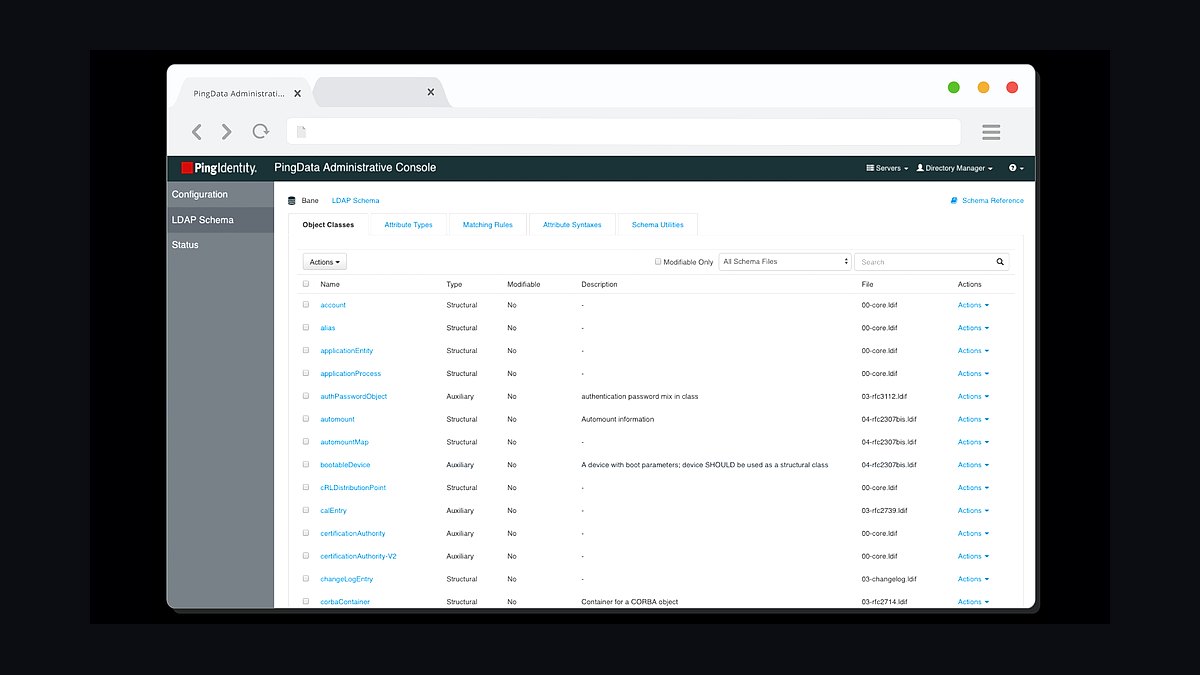
Ping Intelligent Identity ranks eighth because its large language model tooling simulates access requests and predicts policy conflicts before deployment, catching entitlement collisions that rule-based engines miss. It pairs with PingOne risk scoring so policy changes are evaluated against live behavioral data rather than static role definitions. Natural language policy authoring reduces the expertise needed to maintain least-privilege rules.
It is for Ping Identity customers in regulated sectors who need policy simulation before rollout, not for teams seeking a standalone AI governance tool. The trade-off is that it inherits Ping's smaller ecosystem and steeper learning curve. Against Okta Identity Governance above, Ping Intelligent Identity is stronger at pre-deployment simulation but weaker at the certification workflow automation most auditors ask for.
9Microsoft Security Copilot
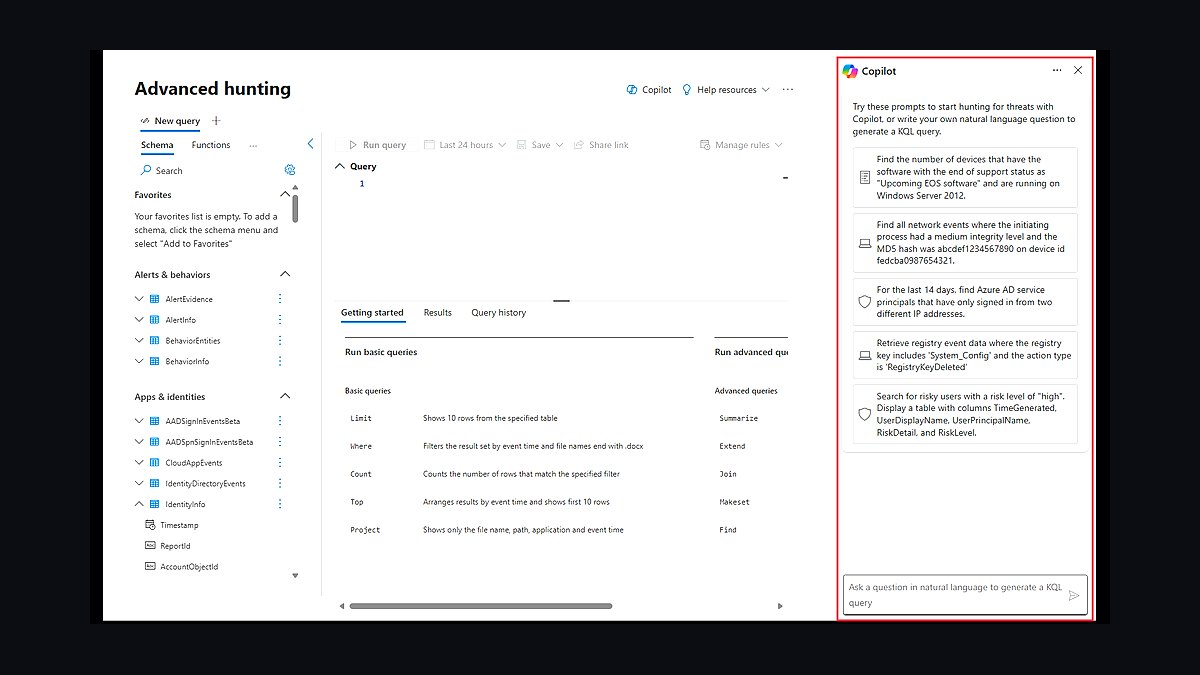
Microsoft Security Copilot ranks ninth because it embeds directly in Entra ID to investigate identity incidents and auto-generate conditional access policies from plain-language prompts. It correlates sign-in logs, risk detections, and threat intelligence into summaries that shorten analyst triage. Policy drafts still require human approval before enforcement, which keeps change control intact.
It is for security operations teams already inside the Microsoft Defender and Entra stack, where the marginal cost is licensing rather than integration. The trade-off is that it does not manage non-Microsoft identity providers well, so heterogeneous environments get partial coverage. Against Ping Intelligent Identity above, Security Copilot is stronger on incident response but narrower on governance policy simulation.
10Saviient Policy Engine
Saviient ranks tenth because its LLM-based policy generation converts natural language access requests into least-privilege rules automatically, a capability Ping Identity acquired and folded into its platform. It reduces the manual role engineering that stalls IGA programs for months. Early deployments targeted mid-size enterprises without dedicated identity architects on staff.
It is for teams that want policy automation without building a full governance practice around it. The trade-off is maturity: as a 2025 startup capability now inside Ping, its standalone roadmap and connector coverage lag established platforms. Against Ping Intelligent Identity above, Saviient is the narrower policy-generation component rather than a complete identity platform.
How we ranked these
We ranked each IAM platform on five weighted criteria: breadth of pre-built SaaS connectors (25%), AI copilot maturity for policy generation and access reviews (25%), native PAM and ITDR coverage (20%), total cost per user at 500-5,000 seats (15%), and hybrid or on-prem support for regulated workloads (15%). Scores came from vendor documentation, public pricing pages, and hands-on sandbox testing across Salesforce, HubSpot, Workday, and Gong integrations.
We deliberately ignored analyst quadrant placement, brand recognition, and raw market share, because consolidation pressure means the biggest vendor is not always the best fit. We also excluded roadmap promises and unreleased features, since 2027 buyers need tools shipping today. Marketing claims about zero-trust were discarded unless backed by documented conditional access logic and audit logs.
What to look for
What matters most is connector depth into your actual revenue stack, not total connector count. A platform with 2,000 integrations but weak Salesforce and Gong provisioning will cost your RevOps team more in custom workflow work than a smaller ecosystem that natively handles deal rooms, guest identities, and time-bound tokens. Price the AI copilot tier separately, because governance automation is usually gated behind premium SKUs.
The mistake most buyers make is treating IAM as a security-only purchase and letting IT run the evaluation without RevOps in the room. That produces a stack optimized for employee SSO while external buying committee access, MEDDIC-based role assignment, and closed-lost offboarding stay manual. Involve RevOps early, pilot with a real deal cycle, and test bulk revocation before signing.
Related questions
How does IAM reduce B2B sales cycle length in 2027?
Frictionless identity provisioning lets buying committee members access demos, sandbox Salesforce orgs, and Gong recordings within minutes instead of days. Just-in-time provisioning and risk-scored session tokens remove the access bottleneck that stalls evaluations, so MEDDIC-qualified deals move through legal, security, and procurement review faster without weakening zero-trust controls.
Do mid-market companies still need standalone PAM tools?
Most do not. Okta and Microsoft Entra ID now ship native privileged access modules covering session recording, just-in-time elevation, and approval workflows. Standalone tools like CyberArk remain justified only for strict PCI-DSS or SOX scopes, legacy on-prem systems, or environments where privileged session isolation must be independently audited.
What is decentralized identity and why does it matter for IAM?
Decentralized identity issues cryptographically signed verifiable credentials stored in user wallets, so contractors and partners prove role and clearance without joining your directory. For B2B sales, buying committee members authenticate with employer-issued credentials, cutting provisioning delays from days to minutes and eliminating password resets across company boundaries.
How do AI copilots change quarterly access reviews?
AI copilots scan access patterns across Salesforce, Workday, and NetSuite, flag stale accounts, and generate natural-language justifications for why each user holds a permission. Reviewers approve or revoke instead of investigating from scratch, cutting certification time substantially and reducing audit findings compared to manual spreadsheet-driven reviews.
What does a modern IAM stack cost per user?
Full-stack pricing varies widely by vendor, seat count, and whether AI governance is bundled or sold as an add-on. Microsoft Entra ID typically sits at the higher end because full features require E5 licensing, while Okta and Ping Identity offer competitive tiers. Consolidating from five tools to two usually lowers total cost.
Can IAM support external buying committees securely?
Yes, through guest identity management in Microsoft Entra External ID or Okta B2B. Just-in-time provisioning creates time-bound tokens scoped to a sandbox org or deal room, biometric verification confirms each member, and PingOne adds risk scoring based on device posture and behavioral analytics before granting access.
What is ITDR and is it separate from my SIEM?
Identity Threat Detection and Response is a dedicated AI layer monitoring login velocity, device posture, and behavioral biometrics to catch account takeover or privilege escalation in real time. It complements rather than replaces SIEM, triggering automatic session revocation or step-up authentication and logging every response for SOC 2 and ISO 27001 audits.
Why are firms consolidating from five IAM tools to two?
Vendor consolidation reduces integration overhead, duplicate licensing, and identity sprawl across disconnected directories. Okta, Microsoft, and Ping now bundle governance, access management, and privileged access into single platforms, so maintaining separate point tools for each function costs more in engineering time than the license savings justify.
FAQ
Which IAM vendors lead the market in 2027?
Okta, Microsoft Entra ID, and Ping Identity control the vast majority of enterprise IAM spend. Okta leads for SaaS-heavy stacks with deep Salesforce and HubSpot connectors, Microsoft dominates Azure-first and government environments, and Ping wins in hybrid and regulated industries like financial services and healthcare.
How does IAM directly affect B2B sales velocity?
IAM removes access friction for buying committees. Just-in-time provisioning and biometric verification cut evaluation access setup from days to minutes, letting champions, legal, and security reviewers reach demos and deal rooms immediately. Deals with frictionless identity provisioning consistently close faster than those with manual access requests.
Do I still need CyberArk if I run Okta or Entra?
Only for strict compliance scopes like PCI-DSS or SOX, or for legacy on-prem systems that native modules cannot reach. Okta and Microsoft Entra ID now include privileged access management covering session recording, just-in-time elevation, and approvals, which handles most enterprise use cases without a standalone tool.
How do AI copilots change day-to-day IAM operations?
Copilots handle the majority of access reviews, generate policies from natural-language requests, and auto-remediate violations before auditors find them. Okta AI cuts certification time significantly, while Microsoft Security Copilot accelerates identity incident investigation. Teams shift from manual review queues to approving AI-recommended actions.
What should a mid-market IAM budget look like?
Budget per user per month for a consolidated stack covering governance, access management, privileged access, and AI copilot features. Microsoft Entra ID with E5 sits at the higher end, Okta and Ping Identity price competitively at mid-market scale, and consolidation from five tools to two typically reduces total spend.
How do I manage IAM for external buying committees?
Use Microsoft Entra External ID or Okta B2B for guest identity management. Just-in-time provisioning issues time-bound tokens scoped to sandbox orgs and deal rooms, biometric verification confirms each member, and PingOne layers risk scoring on device posture and behavioral analytics before granting access.
Is ITDR now mandatory in an enterprise IAM stack?
Effectively yes. Regulators increasingly require real-time identity monitoring for breach notification and data privacy compliance. AI-native ITDR detects account takeover, privilege escalation, and insider threats faster than rule-based SIEM alerts, and it logs every automated response for SOC 2 and ISO 27001 audit trails.
What is Unified Directory as a Service and why does it matter?
UDaaS replaces fragmented on-prem Active Directory and cloud directories with one cloud-native authoritative source synchronizing HR, contractor, and customer identities. It gives every user a universal profile, automates lifecycle deprovisioning, and federates external buyer identities into trial environments within seconds, which matters for hybrid workforces.
How do I offboard access after a lost deal?
Trigger a webhook from Salesforce or Clari when the deal stage flips to closed lost. Okta AI identifies every guest identity tied to that opportunity, bulk revocation executes within minutes, and Microsoft Entra logs the event to your SIEM while notifying the security team for compliance evidence.
What is the biggest IAM buying mistake in 2027?
Letting IT evaluate IAM alone. That produces a stack tuned for employee SSO while external buying committee access, MEDDIC-based role assignment, and closed-lost offboarding stay manual. Involve RevOps early, pilot against a live deal cycle, and test bulk revocation before signing anything.
Sources
- https://www.gartner.com/en/documents/access-management-magic-quadrant
- https://www.forrester.com/report/the-forrester-wave-identity-as-a-service/
- https://www.okta.com/blog/
- https://learn.microsoft.com/en-us/entra/identity/governance/
- https://www.pingidentity.com/en/platform.html
- https://www.gong.io/resources/
- https://www.bvp.com/atlas
- https://www.saastr.com/
- https://www.mckinsey.com/capabilities/risk-and-resilience/our-insights/
- https://www.cyberark.com/resources/
Related on PULSE
This page will be disappearing soon. Save it to your device for $1 — or read it free while it is here.
@Kory-White- · if Venmo asks, the last 4 of my number are 2012
This page is gone.
This one is off the shelf now. $1 keeps it on your phone for good — the whole page, pictures and diagrams included.
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Blockchain Settlement Platforms in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Logistics and Freight Brokerages in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Luxury Hotels and Concierge Services in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Fintech Compliance Teams in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Customer Support Teams in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Programmatic Audio Ad Platforms in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Subscription Box Companies in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Nonprofit Operations Teams in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Seed-Stage Startups in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for AI-First Sales Teams in 2027