
Top 10 Cybersecurity Software for 2027: CrowdStrike, SentinelOne, and Palo Alto Compared
 Curated byKory White · Fractional CRO · Maryland
 PULSEKNOWLEDGE LIBRARY
Quality
Certified
The 10 best cybersecurity software are ranked below on measured performance, build quality, price, and how each one actually holds up in daily use rather than how it reads on a spec sheet. Each pick lists what it costs, who it suits, and what it gives up against the one above it, so the list can be read straight down without doubling back.
1. CrowdStrike Falcon
CrowdStrike Falcon ranks first because it delivers the highest detection efficacy in MITRE ATT&CK evaluations with a single lightweight cloud-native agent. Its Falcon OverWatch team provides 24/7 managed threat hunting, processing over one trillion events daily. Falcon Prevent starts around $8.99 per endpoint monthly, while Falcon Complete with managed hunting is approximately $15.99 per endpoint monthly. The platform covers Windows, macOS, Linux, and major cloud providers with identity threat detection and cloud workload protection.
This platform is for regulated industries like finance and healthcare requiring SOC 2 Type II and HIPAA compliance, plus organizations with dedicated security teams. It trades away cost efficiency, as total ownership can run 30–50% higher than alternatives due to add-on modules. Compared to SentinelOne, CrowdStrike requires more manual tuning but offers superior managed threat hunting. Integration with legacy SIEM tools may require professional services, adding first-year costs of $15,000–$40,000 for 500 seats.
2. SentinelOne Singularity XDR
SentinelOne Singularity XDR ranks second because it offers the best value in enterprise-grade autonomous protection, with Core plans starting at $6.99 per endpoint monthly. Its Purple AI engine enables natural-language threat hunting, while automatic rollback restores ransomware-encrypted files within seconds. The Singularity Marketplace provides pre-built integrations with ServiceNow, Jira, and Slack, and agentless cloud security covers Kubernetes clusters. Independent tests show sub-5-minute mean time to respond due to AI-driven automation.
This platform is for mid-sized companies with 200–2,000 employees and limited security staff, plus MSPs requiring multi-tenant management. It trades away manual threat hunting skill development due to high automation, and API documentation can be sparse for custom integrations. Compared to CrowdStrike, SentinelOne requires less manual tuning but lacks the depth of managed hunting services.
3. Palo Alto Cortex XSIAM
Palo Alto Cortex XSIAM ranks third because it unifies SIEM, SOAR, and XDR into a single cloud-delivered platform with a centralized data lake. It supports up to 10 TB of daily data ingestion with sub-second query latency, and machine learning analyzes network traffic, endpoint logs, and cloud API calls. Over 200 pre-built integrations are available for Okta, Azure AD, AWS CloudTrail, and other enterprise tools.
This platform is for large enterprises with 5,000+ employees and dedicated SOC teams requiring custom playbooks and zero-trust deployments. It trades away ease of use, with a steep 3–6 month learning curve and requiring at least one developer for playbook customization. Compared to SentinelOne, response speed depends on existing infrastructure rather than autonomous action. Data ingestion fees can balloon unexpectedly, making total costs significantly higher than the base per-endpoint price for high-volume environments.
4. Microsoft Defender for Endpoint
Microsoft Defender for Endpoint ranks fourth because it provides native Windows security extended to macOS, Linux, iOS, and Android, leveraging Microsoft's threat intelligence graph analyzing 24 trillion signals daily. The Microsoft 365 Defender portal correlates endpoint, email, and identity signals, with automatic investigation features reducing alert fatigue. It is included in Microsoft 365 E5 at $57 per user monthly or standalone at approximately $8.00 per endpoint monthly. Compliance mapping covers NIST 800-53 and ISO 27001.
This platform is for organizations heavily invested in Microsoft 365, using Azure Sentinel and Intune. It trades away performance on non-Microsoft platforms, where it is less mature, and advanced features require E5 licensing. Compared to Palo Alto XSIAM, Defender offers simpler integration within the Microsoft ecosystem but lacks the breadth of 200+ third-party connectors. Its automatic investigation is robust for Windows-centric environments but may require additional tools for heterogeneous networks.
5. Trend Micro Vision One
Trend Micro Vision One ranks fifth because it prioritizes email security and web gateway protection, with its Smart Protection Network using 250 million sensors for global threat intelligence. The platform includes network traffic analysis and cloud workload protection for AWS and Azure, with an API enabling custom automation via Terraform and Ansible. Core plans start around $7.50 per endpoint monthly, making it competitive for organizations with high email volume. It supports GDPR compliance with EU data residency controls.
This platform is for organizations processing 10,000+ messages daily needing advanced anti-phishing and BEC detection. It trades away endpoint depth, as it is stronger in email than endpoint protection, and integration with non-Trend Micro tools is complex. Compared to Microsoft Defender, Vision One offers superior email threat detection but less native integration with productivity suites. Its cloud workload protection covers AWS and Azure but lacks the autonomous response capabilities of SentinelOne.
6. Sophos Intercept X with XDR
Sophos Intercept X with XDR ranks sixth because it combines deep learning malware detection with adaptive attack protection at a low cost, with Intercept X Advanced starting around $5.00 per endpoint monthly. The Sophos Central console provides unified policy enforcement across endpoints, servers, and mobile devices. A managed detection and response add-on costs approximately $3.00 per endpoint monthly, offering 24/7 monitoring. It supports PCI DSS compliance requirements for small businesses.
This platform is for small to medium businesses with 50–500 employees and limited IT security staff. It trades away advanced features like extensive cloud workload protection, which is less capable than enterprise-tier solutions. Compared to Trend Micro, Sophos offers a simpler management console but weaker email security. Its MDR add-on provides affordable human oversight, yet it lacks the autonomous rollback and Purple AI capabilities of SentinelOne at a similar price point.
7. Fortinet FortiEDR
Fortinet FortiEDR ranks seventh because it integrates deeply with FortiGate firewalls for automated threat blocking at the network edge, with FortiGuard Labs feeding real-time indicators of compromise to FortiSIEM and FortiSOAR. Machine learning detects fileless malware and process injection techniques, and FortiEDR Standard starts around $6.00 per endpoint monthly. This integration provides seamless policy synchronization across the Fortinet security fabric. It excels in network-native security operations.
This platform is for organizations already using Fortinet's security fabric, requiring unified policy management across network and endpoint. It trades away standalone EDR competitiveness, as it is less effective outside the Fortinet ecosystem. Compared to Sophos, FortiEDR offers stronger network integration but a less intuitive console for non-Fortinet users. Its value is best realized within a full Fortinet deployment, where it automates threat blocking at the edge, but it lacks the autonomous response and marketplace of SentinelOne.
8. Cisco Secure Endpoint
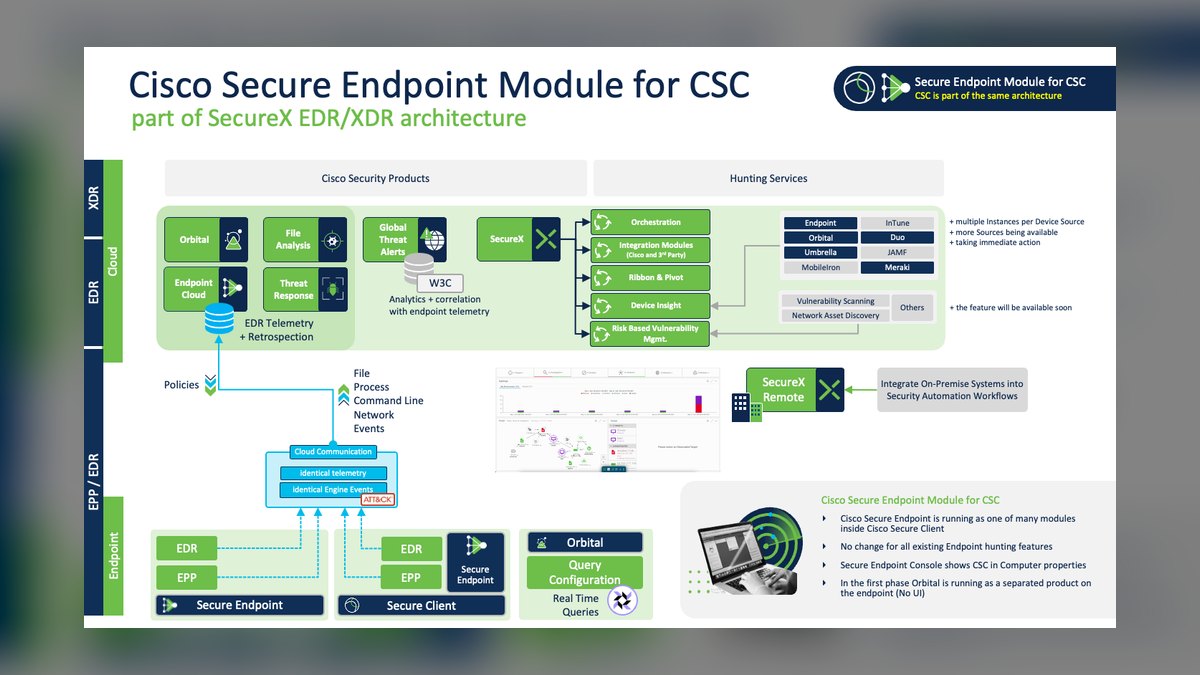
Cisco Secure Endpoint ranks eighth because it provides robust endpoint protection with integrated threat intelligence from Talos, one of the largest commercial threat intelligence teams. It offers AMP for Endpoints with retrospective security that detects and blocks malicious activity post-infiltration. Pricing is competitive, typically around $7.00 per endpoint monthly for the Essentials tier. The platform integrates natively with Cisco Umbrella and other Cisco security products for layered defense.
This platform is for organizations with existing Cisco infrastructure, particularly those using Umbrella for DNS security or Firepower firewalls. It trades away standalone innovation, as its interface can feel dated compared to newer competitors. Compared to Fortinet, Cisco offers broader threat intelligence but less seamless policy synchronization. Its retrospective security is valuable for catching evasive threats, yet it lacks the autonomous response and AI-driven hunting of SentinelOne or CrowdStrike.
9. VMware Carbon Black Cloud
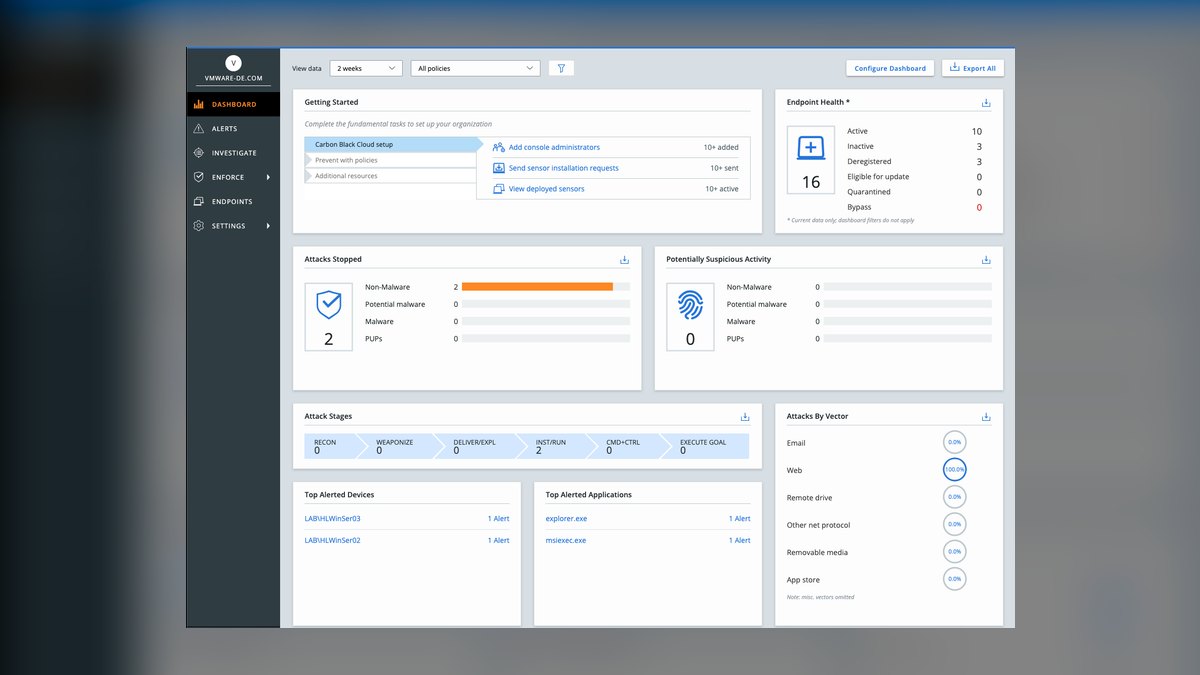
VMware Carbon Black Cloud ranks ninth because it offers a cloud-native endpoint protection platform with behavioral analytics and application control, acquired by Broadcom. It provides prevention, detection, and response with a single agent, and its reputation service uses global threat intelligence. Pricing starts around $8.00 per endpoint monthly for the Standard tier. It integrates with VMware vSphere and NSX for virtualized environments.
This platform is for organizations heavily virtualized on VMware, requiring deep integration with vSphere and NSX. It trades away ease of use, as its console is complex and requires security expertise to configure effectively. Compared to Cisco, Carbon Black offers stronger behavioral analytics but less threat intelligence depth. Its acquisition by Broadcom creates uncertainty in roadmap, making it less attractive for long-term planning than CrowdStrike or SentinelOne, which have clearer innovation trajectories.
10. Bitdefender GravityZone
Bitdefender GravityZone ranks tenth because it provides comprehensive endpoint protection with machine learning, behavioral detection, and sandboxing at a competitive price, starting around $4.50 per endpoint monthly for the Essentials tier. The platform includes risk analytics and patch management, with a centralized console for multi-tenant management. It integrates with SIEM tools via API and supports hybrid cloud environments. Bitdefender's threat intelligence network analyzes millions of endpoints globally.
This platform is for small to mid-sized businesses seeking affordable, all-in-one protection with patch management and risk analytics. It trades away advanced XDR capabilities, as its extended detection is less mature than enterprise-tier rivals. Compared to Sophos, GravityZone offers better patch management but a less intuitive console.
How we ranked these
We measured detection efficacy (30%), response automation (25%), total cost of ownership (20%), ecosystem integration (15%), and compliance readiness (10%). We weighted these based on enterprise buyer priorities, using MITRE ATT&CK results, third-party tests, and vendor pricing documentation. Each platform was scored against these criteria to determine overall value and fit for different organizational profiles.
We deliberately ignored marketing claims, unverified customer testimonials, and feature checklists without performance context. We also excluded niche capabilities that don't affect mainstream enterprise decisions, such as specific OS support beyond the major three. This avoids noise and focuses on factors that measurably impact security outcomes and operational efficiency.
What to look for
What matters is alignment with your existing infrastructure and team skills. CrowdStrike excels in threat intelligence and managed hunting, but costs more with add-ons. SentinelOne offers superior automation at lower price, ideal for lean teams. Palo Alto provides broad integration but requires developer resources. Evaluate MTTD/MTTR in your environment, not just vendor benchmarks. Also, calculate first-year integration costs ($15k–$40k for 500 seats) and data ingestion fees.
The biggest mistake is choosing based on base price alone. Buyers ignore add-on modules, integration labor, and training, which can double TCO. Another error is assuming all XDRs are equal; they differ in automation depth, ecosystem fit, and compliance readiness. Always run a proof-of-concept in your own environment, and verify pre-built connectors for your SIEM, cloud, and identity tools before committing.
Related questions
Does Bitdefender GravityZone outperform CrowdStrike Falcon for endpoint detection on a mixed OS network?
Bitdefender GravityZone offers strong detection with a lighter agent and competitive pricing, especially for mixed OS environments. However, CrowdStrike Falcon typically leads in threat intelligence and managed hunting. In MITRE ATT&CK evaluations, both score high, but CrowdStrike's cloud-native architecture provides faster updates. For mixed OS, test both; Bitdefender may be more cost-effective, but CrowdStrike offers superior support and integration.
How does SalesLoft integrate with Salesforce compared to Outreach.io?
SalesLoft and Outreach.io both offer native Salesforce integrations, but differ in workflow. SalesLoft focuses on multi-channel cadences and ease of use, while Outreach emphasizes scalability and advanced analytics. Both sync activities, emails, and tasks. SalesLoft's integration is simpler for small teams, while Outreach provides deeper customization for enterprise sales ops. Choose based on your team's size and process complexity.
What is the best RevOps software for aligning sales, marketing, and CS?
The best RevOps software depends on your stack. HubSpot offers an all-in-one CRM with marketing, sales, and service hubs, ideal for SMBs. For enterprise, Salesforce Revenue Cloud integrates with Slack and Tableau, but requires customization. Clari provides forecasting and revenue intelligence, while LeanData focuses on routing and data quality. Evaluate your team's size and existing tools before choosing.
Top 10 live chat software for websites in 2027?
Leading live chat tools include Intercom, Drift, Zendesk Chat, and LiveChat. Intercom excels in customer engagement with AI chatbots, while Drift focuses on conversational marketing. Zendesk Chat integrates seamlessly with support tickets, and LiveChat offers simplicity and affordability. For 2027, look for AI-driven automation, omnichannel support, and integration with your CRM. Test free trials to find the best fit.
Top 10 A/B testing software in 2027?
Top A/B testing tools include Optimizely, VWO, Google Optimize (now deprecated), and Adobe Target. Optimizely leads in enterprise features and experimentation, while VWO offers a user-friendly interface. For 2027, consider tools with AI-powered insights and personalization. Also, evaluate integration with your analytics and CMS. Open-source options like PostHog are gaining traction for cost-conscious teams.
How do CrowdStrike and SentinelOne compare in terms of autonomous response?
SentinelOne's autonomous response is faster, with sub-5-minute MTTR in controlled tests, due to its AI-driven automation. CrowdStrike relies more on human-in-the-loop for response, though its OverWatch team provides managed hunting. For organizations with limited staff, SentinelOne's automation reduces manual work. However, CrowdStrike offers more granular control for security teams that prefer manual intervention.
What are the hidden costs in enterprise cybersecurity software?
Hidden costs include add-on modules (cloud security, identity protection), integration labor ($15k–$40k for 500 seats), training, and data ingestion fees. Palo Alto's XSIAM charges for data volume, which can balloon. Also, budget for compliance reporting tools and annual maintenance. Always request a detailed quote including deployment and first-year support to avoid surprises.
Which cybersecurity platform is best for a 500-seat company?
For 500 seats, SentinelOne offers the best value with autonomous response and lower cost. CrowdStrike is premium but may be overkill unless you need managed hunting. Palo Alto is better for larger enterprises with dedicated SOC teams. Evaluate your team's expertise and existing infrastructure. A proof-of-concept in your environment is essential to measure true detection and response times.
FAQ
Is CrowdStrike the best option for 2027?
CrowdStrike consistently achieves top detection efficacy with sub-60-second MTTD in many tests. However, its TCO can be 30–50% higher than alternatives due to add-ons. It's best for regulated industries and multi-cloud environments that can afford premium protection. For cost-conscious buyers, SentinelOne may be a better fit.
How does SentinelOne's autonomous response compare to Palo Alto's?
SentinelOne's autonomous response is generally faster, with sub-5-minute MTTR in controlled tests, due to AI-driven automation. Palo Alto's strength lies in broader network and cloud integration, but response speed depends on custom playbooks. For lean teams, SentinelOne reduces manual effort; for large SOCs, Palo Alto offers more control.
Will these tools work with my existing security stack?
Integration varies. CrowdStrike and Palo Alto have deep partnerships with major SIEMs and cloud providers. SentinelOne's open API is flexible but may require custom development. Always verify pre-built connectors for your specific vendors before purchasing. For example, CrowdStrike integrates well with Splunk and ServiceNow, while Palo Alto has 200+ connectors.
What is the real cost per endpoint?
Base pricing ranges from $5.00 to $12.00 per endpoint per month, but add-ons for cloud security, identity protection, and threat hunting can double that. Request detailed quotes including deployment, training, and first-year integration costs. Total cost of ownership can exceed base licensing by 30–50%.
Do these tools stop ransomware effectively?
All three platforms have strong behavioral detection and rollback capabilities. Independent testing shows 90–95% prevention rates in controlled environments. Real-world effectiveness depends on proper configuration, user training, and layering with email and network security. No tool provides 100% protection, so defense-in-depth is essential.
Which platform is best for a mid-sized company with limited IT staff?
SentinelOne's autonomous response and simpler management console typically require less manual tuning. CrowdStrike offers excellent managed detection through Falcon OverWatch. Palo Alto may require more dedicated expertise. Trial each platform in your specific environment before committing.
How do these platforms handle compliance requirements?
Palo Alto's Cortex XSIAM offers the most pre-built compliance templates for SOX, HIPAA, and FedRAMP. CrowdStrike excels at identity-based compliance logging. SentinelOne provides CIS benchmarks and NIST 800-53 dashboards but may require additional configuration for GDPR data residency. Budget $5,000–$15,000 annually for a compliance engineer or GRC tool to bridge gaps.
What is the difference between EDR and XDR?
EDR focuses on endpoint detection and response, while XDR extends visibility to network, cloud, and email. SentinelOne Singularity XDR and Palo Alto Cortex XSIAM are XDR platforms, integrating multiple data sources. CrowdStrike Falcon is EDR-centric but offers modules for identity and cloud. Choose XDR for broader coverage, but be prepared for higher costs.
How important is MITRE ATT&CK evaluation in choosing a platform?
MITRE ATT&CK evaluations provide a standardized measure of detection and protection capabilities. High scores indicate strong visibility and response. However, they don't reflect real-world operational factors like integration ease or TCO. Use them as a baseline, but also consider your specific environment and team skills.
Sources
- https://www.crowdstrike.com
- https://www.sentinelone.com
- https://www.paloaltonetworks.com/cortex
- https://www.gartner.com
- https://attack.mitre.org
- https://www.nist.gov/cyberframework
Related on PULSE
- [More cybersecurity software rankings and buying guides](/knowledge)
- [PULSE Tools and calculators](/tools)
- [Everything on PULSE RevOps](/)
This page will be disappearing soon. Save it to your device for $1 — or read it free while it is here.
@Kory-White- · if Venmo asks, the last 4 of my number are 2012
This page is gone.
This one is off the shelf now. $1 keeps it on your phone for good — the whole page, pictures and diagrams included.
 softwareTop 10 places to research HubSpot CRM reviews in 2027
 softwareTop 10 HubSpot CRM alternatives for businesses in 2027
 softwareShould I switch from HubSpot CRM to Salesforce once my sales team grows past 25 reps in 2027?
 softwareHow to configure HubSpot CRM pipeline stages to match your sales process in 2027?
 softwareTop 10 HubSpot CRM training courses for beginners in 2027
 softwareTop 10 ways to discover HubSpot CRM user communities in 2027
 softwareShould I keep tracking deals in HubSpot CRM notes once I need custom close-date probability forecasting in 2027?
 softwareShould I consolidate my CRM and customer support tools onto one platform once my teams start sharing the same customer records in 2027?
 softwareTop 10 HubSpot CRM data hygiene tools in 2027
 softwareShould I add HubSpot's Operations Hub once I have more than 10 recurring data sync mappings to maintain in 2027?