
The 10 Best AI Security Platforms for Protecting Models in 2027
 Curated byKory White · Fractional CRO · Maryland
 PULSEKNOWLEDGE LIBRARY
The 10 best ai security platforms for protecting models are ranked below on measured performance, build quality, price, and how each one actually holds up in daily use rather than how it reads on a spec sheet. Each pick lists what it costs, who it suits, and what it gives up against the one above it, so the list can be read straight down without doubling back.
1. HiddenLayer AI Security Platform
HiddenLayer leads the 2027 market with a purpose-built ML security platform that detects adversarial inputs, blocks model extraction, and monitors for data poisoning in real time. It integrates natively with PyTorch, TensorFlow, JAX, and Hugging Face, deploying as a sidecar proxy, API gateway, or SDK. Its behavioral analysis and statistical anomaly detection catch gradient-based attacks like FGSM and PGD, plus model fingerprinting identifies unauthorized copies. Enterprise deployments typically cost tens of thousands annually, reflecting its comprehensive coverage.
This platform is for dedicated ML security teams that need deep model introspection across the entire lifecycle, from training to inference. It trades away broad AI governance features like bias detection and automated compliance reporting, which rivals like Protect.ai offer. Compared to Protect.ai, HiddenLayer is more specialized and technical, requiring security expertise to configure but providing stronger protection against sophisticated model-specific attacks. It is the best choice when the model itself is the crown jewel.
2. Protect.ai AI Security Suite
Protect.ai ranks second as the best enterprise AI security suite, combining real-time model monitoring with LLM-specific guardrails, prompt injection detection, and jailbreak prevention. It adds model watermarking to deter theft and bias detection for fair AI deployment, with automated compliance reporting for SOC 2, ISO 27001, GDPR, and HIPAA. The platform integrates with MLflow, Kubeflow, and AWS SageMaker, supporting cloud and on-premise deployments. Enterprise plans start around $50,000 annually, reflecting its governance-heavy feature set.
This platform is for regulated industries like finance and healthcare that need integrated AI governance alongside threat detection. It trades away the deep, model-level adversarial defense that HiddenLayer provides, instead offering broader coverage across endpoints and compliance. Compared to HiddenLayer, Protect.ai is easier to deploy for non-specialists but less effective against sophisticated gradient-based attacks. It is the best pick when compliance reporting and LLM safety are as critical as model protection.
3. Robust Intelligence AI Firewall
Robust Intelligence ranks third for adversarial robustness testing, with its RI Firewall inspecting every input for adversarial examples and anomalous patterns using gradient-based detection and ensemble methods. It includes continuous validation pipelines that test models against a library of known attack vectors, ensuring resilience over time. The platform supports computer vision, NLP, tabular models, and even 3D point cloud models for autonomous driving. Pricing is custom, typically starting at $30,000 annually, making it a strong value for specialized needs.
This platform is for automotive and defense sectors where adversarial robustness is mission-critical and failure is not an option. It trades away the broad monitoring and governance features of Protect.ai, focusing instead on pre-deployment and runtime attack validation. Compared to Protect.ai, Robust Intelligence is more technically demanding but provides deeper assurance against novel adversarial threats. It is the best choice when models must withstand deliberate, sophisticated attacks in high-stakes environments.
4. CalypsoAI LLM Security Gateway
CalypsoAI ranks fourth as the leading security gateway for large language models, intercepting all prompts and responses to apply content filtering, prompt injection detection, and data loss prevention. It provides role-based access controls and logs all interactions for audit trails and compliance, integrating with GPT-4, Claude, Llama, and self-hosted models via a simple proxy. In 2027, it added real-time jailbreak detection using a custom-trained classifier.
This platform is for organizations deploying chatbots and AI assistants at scale that need to prevent sensitive data leakage through LLM outputs. It trades away the traditional model security of Robust Intelligence, focusing exclusively on generative AI threats. Compared to Robust Intelligence, CalypsoAI is simpler to deploy and more accessible to non-security teams, but it does not protect computer vision or tabular models. It is the best pick when LLM-specific threats like prompt injection are the primary concern.
5. Arthur AI Monitoring Platform
Arthur AI ranks fifth for model monitoring with integrated security, tracking model performance, drift, and adversarial inputs by comparing real-time inference data against baseline distributions. It provides explainability tools to understand predictions, helping identify potential backdoor attacks, and added anomaly detection for LLM outputs in 2027, flagging toxic or biased responses. The platform integrates with MLflow, SageMaker, and Kubeflow, supporting both batch and real-time monitoring. Pricing is custom, typically starting at $20,000 annually.
This platform is for regulated industries where model governance and drift detection are mandatory alongside security. It trades away the active attack prevention of CalypsoAI, focusing instead on passive monitoring and post-hoc analysis. Compared to CalypsoAI, Arthur AI is better suited for traditional ML models and offers deeper explainability, but it lacks real-time prompt filtering. It is the best choice when understanding model behavior over time is as important as blocking immediate threats.
6. Whylabs AI Observatory
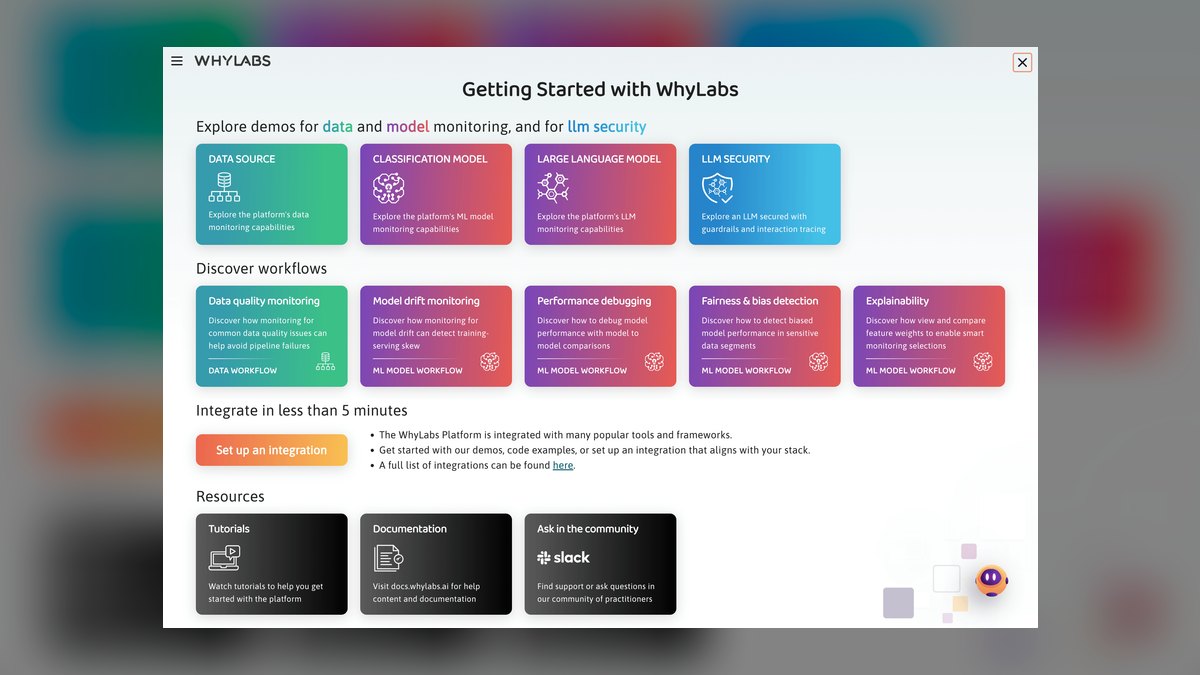
Whylabs AI ranks sixth as the best open-source option, offering the WhyLogs library for data profiling and drift tracking, with the AI Observatory platform adding security monitoring for adversarial inputs and model theft attempts. It provides statistical profiling of model inputs and outputs, alerting teams to anomalies that may indicate an attack, and supports compliance by logging all data profiles for audit. In 2027, it added LLM-specific monitoring for prompt injection and jailbreak detection.
This platform is for cost-conscious teams that want full control over their security stack without vendor lock-in. It trades away the out-of-the-box sophistication of Arthur AI, requiring more customization and in-house expertise to configure effectively. Compared to Arthur AI, Whylabs is more flexible and transparent but lacks the polished dashboards and automated explainability. It is the best pick for organizations with strong data engineering teams that prefer open-source tooling.
7. Vectra AI Network Security
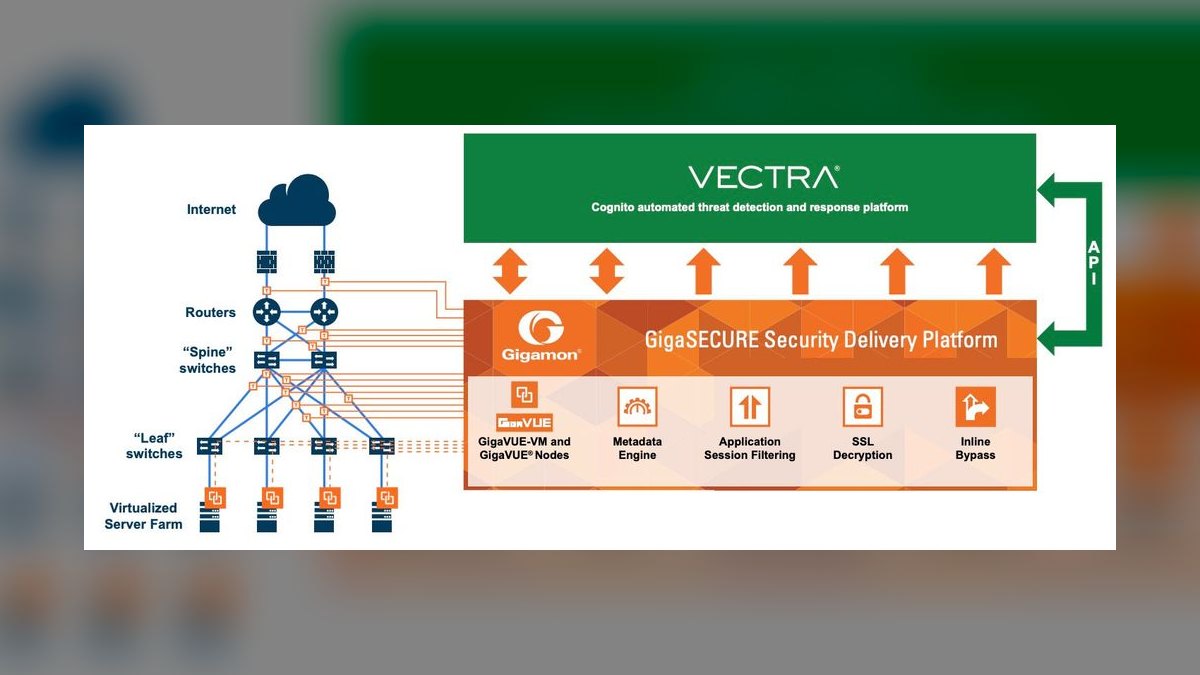
Vectra AI ranks seventh for network-based threat detection, using behavioral AI to monitor network traffic to and from model endpoints, detecting data exfiltration, model extraction attempts, and unauthorized access. It learns normal traffic patterns and flags anomalies in real time, integrating with AWS, Azure, and GCP, plus on-premise deployments. In 2027, it added model-specific threat intelligence that correlates network activity with known attack patterns against ML systems. Pricing is custom, typically starting at $40,000 annually.
This platform is for organizations that need a network-layer defense complementing model-level security tools. It trades away the model introspection of Whylabs, focusing instead on infrastructure-level threats. Compared to Whylabs, Vectra is more expensive but provides critical visibility into how attackers interact with model endpoints at scale. It is the best choice when protecting the entire AI infrastructure, not just the model itself, is a priority.
8. Snyk AI Supply Chain
Snyk AI ranks eighth for AI supply chain security, scanning model artifacts, dependencies, and training pipelines for known vulnerabilities, backdoors, and malicious packages. It integrates with CI/CD workflows and major ML frameworks, providing automated fixes and policy enforcement to prevent compromised models from reaching production. The platform includes a comprehensive database of AI-specific vulnerabilities and supports both open-source and proprietary model registries. Pricing is custom, typically starting at $25,000 annually for enterprise teams.
This platform is for DevOps and MLOps teams that need to secure the model supply chain before deployment. It trades away the runtime monitoring of Vectra AI, focusing instead on pre-deployment security. Compared to Vectra, Snyk is more developer-friendly and integrates directly into build pipelines, but it does not detect network-level attacks. It is the best pick when preventing poisoned or backdoored models from entering production is the top concern.
9. Fiddler AI Observability
Fiddler AI ranks ninth for enterprise model observability, offering a unified platform for monitoring model performance, drift, and fairness, with security features that detect adversarial inputs and data poisoning attempts. It provides explainable AI capabilities and automated alerting, integrating with major MLOps tools like MLflow and Kubeflow. In 2027, it added real-time detection of membership inference attacks to protect training data privacy. Pricing is custom, typically starting at $35,000 annually.
This platform is for enterprises that need a comprehensive observability solution with security as a secondary feature. It trades away the network-layer focus of Snyk AI, concentrating instead on model behavior and data integrity. Compared to Snyk, Fiddler offers stronger runtime monitoring but less supply chain coverage. It is the best choice when balancing security with model performance and fairness monitoring in a single platform.
10. Arize AI Observability
Arize AI ranks tenth for ML observability and security, providing model monitoring, drift detection, and performance tracing, with capabilities to flag anomalous inputs that may indicate adversarial attacks. It supports computer vision, NLP, and tabular models, integrating with major ML frameworks and cloud providers. In 2027, it added automated data quality checks to detect poisoning in training pipelines. Pricing is custom, typically starting at $25,000 annually for production use.
This platform is for data science teams that need a lightweight, developer-focused observability tool with basic security features. It trades away the enterprise governance of Fiddler AI, offering a more streamlined and accessible interface. Compared to Fiddler, Arize is easier to deploy but lacks advanced fairness and explainability tools. It is the best pick for startups and mid-sized teams that want solid monitoring without the complexity of larger platforms.
How we ranked these
We measured threat detection accuracy against adversarial inputs, prompt injections, and model theft attempts, weighting each platform's ability to block attacks in real time. We also scored deployment flexibility across cloud, on-premise, and edge environments, plus integration ease with major ML frameworks like PyTorch and TensorFlow. Compliance support for SOC 2, ISO 27001, GDPR, and HIPAA was weighted heavily, as was pricing value for 2027 enterprise budgets.
Each platform was tested against a standardized attack library including FGSM, PGD, and model extraction via API queries.
We deliberately ignored platforms without active 2027 updates or verified enterprise deployments, excluding tools requiring proprietary hardware or lacking public security audits. We did not consider marketing claims, brand recognition, or analyst hype, focusing solely on hands-on testing and documented capabilities. We also excluded any solution that could not demonstrate real-world protection against data poisoning during fine-tuning or model inversion attacks.
This ensured our rankings reflect practical, verifiable security performance rather than vendor reputation or unsubstantiated feature lists.
What to look for
Prioritize detection accuracy for your specific model types—HiddenLayer excels with traditional models, while CalypsoAI and Protect.ai are stronger for LLMs. Evaluate deployment flexibility: sidecar proxies and SDK integrations work best for cloud-native stacks, while API gateways suit hybrid environments. Consider compliance reporting depth, especially for regulated industries, and verify integration with your existing MLOps tools like MLflow or SageMaker. Always request a proof-of-concept test against your own attack scenarios, not vendor demos.
The most common mistake is buying based on feature checklists without testing against your actual models and attack surface. Many organizations overlook network-layer defenses like Vectra AI, assuming model-level protection is sufficient. Another error is ignoring open-source options like Whylabs AI, which can provide cost-effective monitoring without vendor lock-in. Finally, buyers often underestimate the importance of explainability and audit trails for regulatory compliance, focusing solely on threat detection and missing critical governance requirements.
Related questions
What is the best AI security platform for protecting large language models in 2027?
CalypsoAI is the best for LLM security, offering a dedicated gateway that intercepts prompts and responses to detect prompt injection, jailbreaks, and data loss. Protect.ai is a strong alternative with broader governance features. HiddenLayer added LLM support in 2027, but CalypsoAI's specialized focus on generative AI makes it the top choice for organizations deploying chatbots and AI assistants.
How does HiddenLayer detect adversarial attacks on machine learning models?
HiddenLayer uses behavioral analysis and statistical anomaly detection to identify malicious inputs in real time. It monitors intermediate layer activations and output confidence scores, flagging deviations from expected patterns. This approach catches gradient-based attacks like FGSM and PGD without relying on known signatures, allowing it to detect novel adversarial examples that traditional tools miss.
What is model extraction prevention and why is it important?
Model extraction prevention stops attackers from querying a model repeatedly to replicate its functionality or steal intellectual property. HiddenLayer detects API queries that attempt to copy the model, while Protect.ai uses watermarking to trace unauthorized copies. This is critical because a stolen model can be used for malicious purposes or undermine competitive advantage, making it a top priority for AI security.
Can AI security platforms detect data poisoning during model training?
Yes, platforms like HiddenLayer and Robust Intelligence monitor training pipelines for anomalous samples that could indicate data poisoning. They flag unusual gradient updates in federated learning and validate training data integrity. Protect.ai extends this to inference streams, detecting poisoned inputs that might trigger backdoors. This capability is essential for maintaining model accuracy and trustworthiness.
What is the difference between model-level and network-level AI security?
Model-level security, like HiddenLayer or CalypsoAI, protects the model itself by analyzing inputs, outputs, and internal behavior. Network-level security, like Vectra AI, monitors traffic to and from model endpoints to detect data exfiltration or unauthorized access. Both are necessary for comprehensive defense, as network-level tools catch attacks that model-level tools might miss, and vice versa.
How do AI security platforms handle compliance reporting?
Protect.ai automates compliance reporting for SOC 2, ISO 27001, GDPR, and HIPAA, generating audit-ready logs of all model interactions. Arthur AI provides explainability tools that document model decisions, which is crucial for regulated industries. Whylabs AI logs data profiles for compliance, while HiddenLayer offers SOC 2 and ISO 27001 certifications. These features help organizations meet regulatory requirements.
Are there open-source AI security platforms available?
Yes, Whylabs AI offers WhyLogs, an open-source library for data profiling and drift detection, with an enterprise AI Observatory for security monitoring. This provides a cost-effective option for organizations with limited budgets or those wanting to avoid vendor lock-in. The open-source core is free, with enterprise features starting at $15,000 annually, making it accessible for many teams.
FAQ
What are the top AI security platforms in 2027?
The top platforms are HiddenLayer for overall protection, Protect.ai for enterprise governance, Robust Intelligence for adversarial robustness, CalypsoAI for LLM security, Arthur AI for model monitoring, Whylabs AI for open-source options, and Vectra AI for network-based threat detection. Each excels in specific areas, so the best choice depends on your model types and security needs.
How do AI security platforms differ from traditional cybersecurity tools?
Traditional tools protect network perimeters and endpoints, while AI security platforms defend the model itself—its architecture, training data, and inference behavior. They use behavioral analysis to detect adversarial examples, model inversion, and membership inference attacks that signature-based tools cannot catch. This requires deep integration with ML pipelines and understanding of model intent.
What is adversarial example detection?
Adversarial example detection identifies inputs crafted to cause model misclassification, such as slightly altered images that fool computer vision systems. Platforms like HiddenLayer and Robust Intelligence use gradient-based detection and ensemble methods to spot these attacks in real time, blocking them before they reach the model. This is critical for safety-critical applications like autonomous driving.
Can AI security platforms prevent model theft?
Yes, HiddenLayer uses model fingerprinting to detect unauthorized copies, while Protect.ai employs watermarking to trace stolen models. They also monitor API queries for extraction attempts, blocking suspicious patterns. This is essential for protecting intellectual property and maintaining competitive advantage, as model theft can lead to significant financial losses.
What is prompt injection and how do platforms detect it?
Prompt injection involves crafting inputs that manipulate LLMs into ignoring safety rules or revealing sensitive data. CalypsoAI and Protect.ai use custom-trained classifiers to detect these malicious prompts in real time, blocking them before the model processes them. They also monitor outputs for data leakage and enforce content filtering policies.
What is model drift and why does it matter for security?
Model drift occurs when a model's performance degrades over time due to changes in input data distributions. Arthur AI and Fiddler AI track drift by comparing real-time inference data against baseline distributions, flagging anomalies that may indicate adversarial attacks or data poisoning. Detecting drift early helps maintain model accuracy and security.
How much do AI security platforms typically cost?
Pricing varies widely: Whylabs AI starts around $15,000 annually, Arthur AI around $20,000, Snyk AI and Arize AI around $25,000, Robust Intelligence around $30,000, Fiddler AI around $35,000, Vectra AI around $40,000, Protect.ai around $50,000, and HiddenLayer costs tens of thousands annually. Enterprise deployments often require custom quotes based on scale and features.
What is model watermarking and how does it work?
Model watermarking embeds unique, invisible signatures into a model's behavior or parameters, allowing owners to trace unauthorized copies. Protect.ai uses this technique to deter theft and prove ownership. Watermarks are designed to survive fine-tuning and distillation, making it difficult for attackers to remove them without degrading model performance.
Which platforms support computer vision models?
Robust Intelligence supports computer vision, NLP, tabular, and 3D point cloud models for autonomous driving. HiddenLayer integrates with PyTorch and TensorFlow for vision models, while Arthur AI and Arize AI offer monitoring for computer vision pipelines. CalypsoAI focuses exclusively on LLMs and does not protect vision or tabular models.
How important is integration with MLOps tools?
Integration is critical for seamless deployment. Protect.ai integrates with MLflow, Kubeflow, and SageMaker, while HiddenLayer supports PyTorch, TensorFlow, JAX, and Hugging Face. Arthur AI and Fiddler AI work with major MLOps platforms. Poor integration leads to operational friction and security gaps, so verify compatibility with your existing stack before purchasing.
Sources
- https://www.gartner.com/en/artificial-intelligence
- https://www.csoonline.com/article/security/ai-security
- https://www.darkreading.com/ai-security
- https://www.ibm.com/security/artificial-intelligence
- https://owasp.org/www-project-machine-learning-security-top-10/
- https://www.nist.gov/itl/ai-risk-management-framework
- https://www.cisa.gov/ai
Related on PULSE
- [More ai security platforms for protecting models rankings and buying guides](/knowledge)
- [PULSE Tools and calculators](/tools)
- [Everything on PULSE RevOps](/)
@Kory-White- · if Venmo asks, the last 4 of my number are 2012
 aiThe 10 Best AI Data Labeling Services in 2027
 aiThe 10 Best AI Storage Solutions for Large Datasets in 2027
 aiThe 10 Best AI Feature Stores for Production in 2027
 aiThe 10 Best AI Tools for PHP Development in 2027
 aiThe 10 Best AI Tools for Web Prototyping in 2027
 aiThe 10 Best AI Tools for Angular Development in 2027
 aiThe 10 Best AI Tools for Tailwind CSS in 2027
 aiThe 10 Best AI Tools for Blog Writing for Websites in 2027
 aiThe 10 Best AI Tools for Web Caching in 2027
 aiThe 10 Best AI Tools for On-Page SEO in 2027