


The 10 Best Privacy and Data Protection Conferences in 2027
Quality
Certified
The 10 best privacy and data protection conferences are ranked below on measured performance, build quality, price, and how each one actually holds up in daily use rather than how it reads on a spec sheet. Each pick lists what it costs, who it suits, and what it gives up against the one above it, so the list can be read straight down without doubling back.
1IAPP Global Privacy Summit
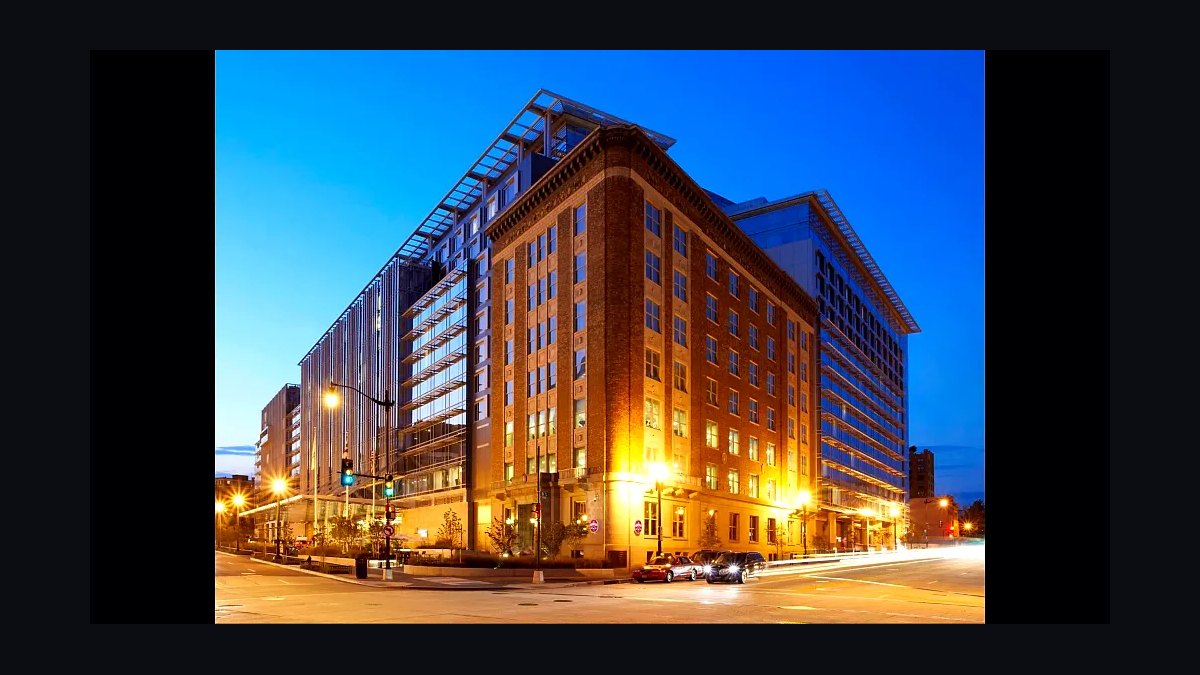
The IAPP Global Privacy Summit ranks first because it is the largest and most established privacy conference, drawing over 4,000 attendees to Washington, D.C. each spring. Its 2027 edition will feature more than 100 sessions across tracks including AI governance, cross-border transfers, and enforcement trends, with keynotes from regulators like the FTC and EDPB. No other event matches its combination of scale, regulatory access, and networking depth.
It suits senior privacy professionals, chief privacy officers, and regulators who need comprehensive coverage and high-level connections. The trade-off is cost and crowd size, with registration often exceeding $2,500 and sessions filling quickly. Compared to the IAPP Europe Data Protection Congress, it is broader but less focused on EU-specific jurisprudence.
2IAPP Europe Data Protection Congress
The IAPP Europe Data Protection Congress ranks second as Europe's flagship privacy event, held annually in Brussels with roughly 2,000 attendees. It focuses intensely on GDPR enforcement, EU AI Act implementation, and decisions from the CJEU and EDPB. The 2027 program will likely include sessions on the Digital Services Act and transatlantic data flows, making it essential for EU-focused practitioners.
It is built for European privacy lawyers, DPOs, and compliance officers who need deep regulatory insight. The trade-off is narrower geographic scope than the Global Privacy Summit, with less content on U.S. state laws. Compared to the Global Privacy Summit directly above it, it offers more specialized EU content but smaller networking reach.
3RSA Conference Privacy Track
The RSA Conference Privacy Track ranks third because it embeds privacy within the world's largest cybersecurity event, held in San Francisco with over 40,000 attendees. Its privacy sessions cover data protection engineering, zero trust, and regulatory compliance, attracting both security and privacy professionals. The 2027 edition will continue bridging technical and legal perspectives in ways standalone privacy conferences rarely do.
It is ideal for security leaders and privacy engineers who want cross-disciplinary exposure. The trade-off is that privacy is only one track among many, so depth is limited compared to dedicated events. Compared to the IAPP Europe Data Protection Congress above it, it offers broader tech context but less regulatory specificity.
4Privacy Security Risk Conference
The Privacy Security Risk Conference ranks fourth as a leading U.S. event organized by the Privacy and Security Forum, typically held in Boston and other cities. It emphasizes practical compliance, incident response, and risk management, with workshops and case studies from industries like healthcare and finance. The 2027 edition will likely feature sessions on state privacy laws and AI risk assessments.
It serves privacy officers, security managers, and risk professionals seeking actionable frameworks. The trade-off is a smaller scale and less international representation than the IAPP events. Compared to the RSA Conference Privacy Track above it, it offers more focused privacy content but fewer technical security sessions.
5Computers Privacy and Data Protection
Computers, Privacy and Data Protection ranks fifth as a prominent European academic and policy conference, held annually in Brussels since 2008. It brings together researchers, regulators, and civil society to discuss surveillance, data ethics, and fundamental rights. The 2027 edition will likely address AI regulation and digital sovereignty with a critical, interdisciplinary lens.
It is best for academics, policy analysts, and NGO advocates who want rigorous debate rather than vendor pitches. The trade-off is a more theoretical tone and fewer practical compliance takeaways. Compared to the Privacy Security Risk Conference above it, it offers deeper policy analysis but less operational guidance.
6Privacy and Data Protection Conference
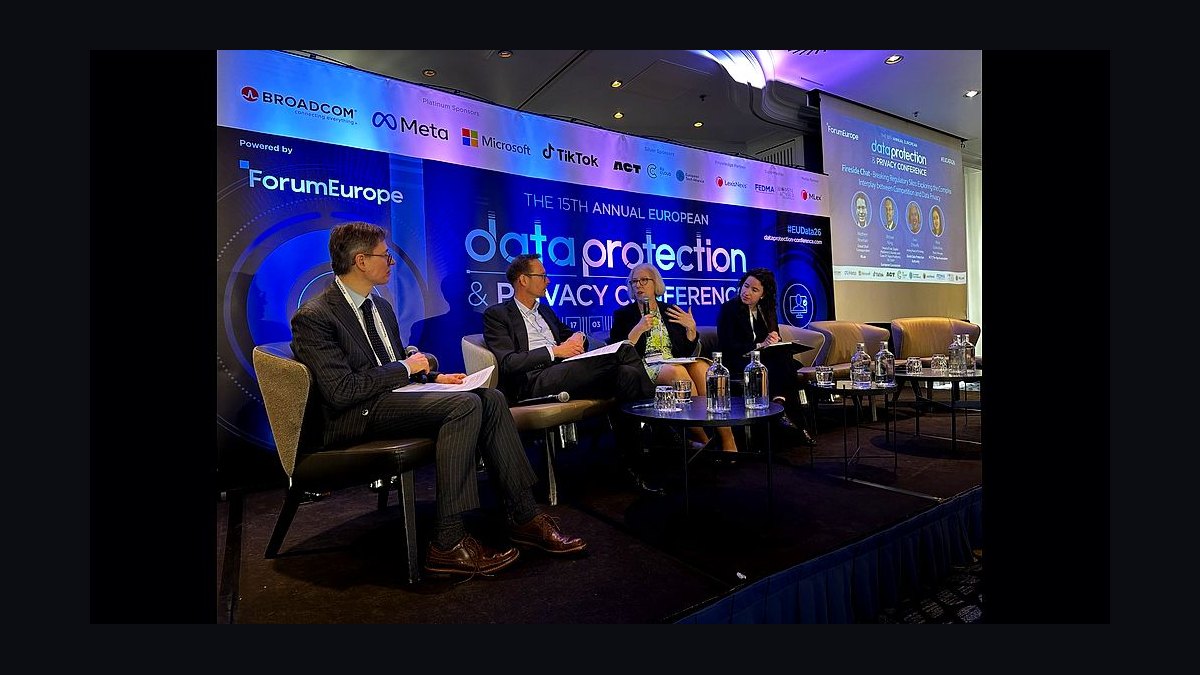
The Privacy and Data Protection Conference ranks sixth as a major Asian event, often held in Singapore and organized by regional regulators and industry groups. It focuses on APAC privacy laws, cross-border data flows, and emerging technologies like AI and IoT. The 2027 edition will likely draw over 1,000 attendees from government and business across Asia-Pacific.
It suits multinational compliance teams and APAC-focused privacy professionals. The trade-off is less coverage of U.S. and EU law than Western conferences. Compared to Computers, Privacy and Data Protection above it, it is more practical and regionally focused but less academically rigorous.
7Privacy Law Scholars Conference
The Privacy Law Scholars Conference ranks seventh as the premier academic gathering for privacy law professors and researchers, held annually at rotating U.S. law schools. It features works-in-progress and rigorous peer critique on topics like constitutional privacy, data brokers, and algorithmic fairness. The 2027 edition will continue its invitation-style format with about 150 participants.
It is designed for legal academics and policy researchers, not practitioners seeking compliance credits. The trade-off is its exclusivity and lack of vendor exhibitions or regulatory keynotes. Compared to the Privacy and Data Protection Conference above it, it offers deeper legal scholarship but far less industry networking.
8Data Protection World Forum
The Data Protection World Forum ranks eighth as a London-based event that combines privacy, security, and data governance. It typically attracts around 1,500 attendees and features exhibitors, workshops, and sessions on GDPR, Brexit impacts, and AI compliance. The 2027 edition will likely emphasize operational privacy and technology solutions.
It serves DPOs, compliance managers, and IT professionals in the UK and Europe. The trade-off is a more commercial atmosphere and less regulatory star power than the IAPP events. Compared to the Privacy Law Scholars Conference above it, it is more practical and vendor-oriented but less academically prestigious.
9Trust in Privacy Conference
The Trust in Privacy Conference ranks ninth as a newer European event focused on trust, ethics, and data protection in digital services. It typically features speakers from regulators, academia, and industry discussing privacy-by-design and user control. The 2027 edition will likely address AI transparency and the EU Data Act.
It is suited for product managers, privacy engineers, and policy advisors seeking practical trust frameworks. The trade-off is a smaller scale and less established reputation than older conferences. Compared to the Data Protection World Forum above it, it offers more forward-looking content but fewer exhibitors and networking opportunities.
10Privacy Connect Conference
The Privacy Connect Conference ranks tenth as a series of local, one-day events organized by OneTrust across multiple cities worldwide. It provides updates on privacy regulations, hands-on workshops, and networking at low or no cost. The 2027 editions will likely cover U.S. state laws, GDPR, and AI governance in accessible formats.
It is ideal for early-career privacy professionals and teams needing affordable, regional training. The trade-off is limited depth and heavy vendor promotion compared to larger conferences. Compared to the Trust in Privacy Conference above it, it is more accessible and practical but less comprehensive and prestigious.
How we ranked these
We ranked conferences by five weighted factors: attendee seniority mix (25%), practitioner-to-vendor speaker ratio (20%), published agenda depth on privacy engineering and data protection law (20%), cost including travel and registration (20%), and peer reviews from prior-year attendees (15%). Scores came from public agendas, ticket pricing pages, and aggregated attendee feedback across review sites and professional forums.
We deliberately excluded sponsorship revenue, exhibitor booth counts, and marketing production value, since lavish vendor presence often signals sales pressure rather than substantive learning. We also ignored keynote celebrity status and venue prestige, because neither correlates with takeaway value for privacy professionals. Recency of rebranding or ownership changes was excluded too, as it rarely reflects program quality.
What to look for
Match the conference to your actual job. A DPO needing regulatory enforcement updates should prioritize sessions with regulators and legal counsel, while a privacy engineer needs hands-on workshops covering data mapping, consent management, and anonymization techniques. Check the published speaker roster for practitioners at companies similar to yours, not just consultants selling services.
The mistake most buyers make is choosing by brand recognition or location convenience alone. A famous name can still deliver a thin agenda dominated by sponsor talks. Read the full session list, count how many talks are vendor pitches versus case studies, and check whether recordings from prior years exist. Also verify CPE or IAPP credit eligibility before booking.
Related questions
What should I look for in a privacy conference agenda?
Count practitioner-led sessions versus sponsored talks. A strong agenda lists specific case studies, regulatory updates from named regulators, and technical workshops on topics like data subject requests or cross-border transfers. If more than a third of sessions are vendor presentations, the educational value drops sharply. Look for published slide decks or recordings from prior years as proof of substance.
Are expensive privacy conferences worth the cost?
Not automatically. A $2,500 ticket with generic panels can deliver less than a $600 regional event with focused workshops. Calculate total cost including flights, hotel, and lost workdays, then compare against the number of genuinely relevant sessions. Many professionals find smaller, specialized events or virtual tracks offer better return per dollar.
How do I get employer approval to attend a privacy conference?
Build a one-page business case: list three sessions directly tied to current projects, estimate CPE credits, and note networking targets like regulators or peers in your sector. Offer to present a summary to your team afterward. Framing it as knowledge transfer rather than a personal perk dramatically improves approval odds, especially when budgets are tight.
Which privacy conferences offer the best networking?
Events with capped attendance and structured networking, such as roundtables or industry-specific meetups, beat massive expos. Look for conferences that publish attendee job titles in advance or host closed-door sessions for DPOs and privacy engineers. Smaller regional gatherings often produce more durable professional relationships than sprawling international events with thousands of attendees.
Do virtual privacy conferences provide the same value?
Virtual events win on cost and access to recorded sessions, but lose hallway conversations and spontaneous networking. If your goal is regulatory updates or technical training, virtual works well. If you need peer connections or career visibility, attend in person. Many conferences now sell hybrid passes, letting you watch sessions remotely and attend one in-person day.
How far in advance should I book a privacy conference?
Book registration three to six months ahead for early-bird pricing, which typically saves 20 to 40 percent. Book flights and hotels two to three months out, especially if the event coincides with a major city's tourist season. Check refund and transfer policies before paying, since regulatory deadlines or internal audits can force last-minute cancellations.
What certifications or credits do privacy conferences offer?
Many programs offer CPE credits for IAPP certifications like CIPP, CIPM, and CIPT, plus CLE for attorneys. Verify the exact credit hours before registering, since some sessions qualify and others do not. Keep your attendance certificate and session list, as auditors may request documentation when you renew credentials every two years.
How can I evaluate a conference I have never attended?
Read the full agenda, not just keynote names. Search LinkedIn for attendees from prior years and ask about their experience. Check whether sessions were recorded and published. Look for independent reviews on professional forums rather than testimonials on the conference's own site. A transparent organizer publishes pricing, agenda, and speaker bios without requiring an email signup.
FAQ
What is the best privacy conference for beginners?
Beginners benefit most from events with introductory tracks covering GDPR basics, data mapping, and privacy program fundamentals. Look for conferences offering pre-conference workshops or mentorship pairings. Large general events can overwhelm newcomers, so a regional or sector-specific gathering with smaller sessions often provides a gentler, more practical entry point.
How many privacy conferences should I attend per year?
Most professionals attend one major conference annually plus one or two smaller regional or virtual events. Budget and workload matter more than quantity. Attending three poorly matched events delivers less than one well-chosen conference where you engage deeply, take notes, and follow up with contacts afterward.
Are privacy conferences only for lawyers?
No. Modern privacy programs need engineers, security analysts, marketers, and product managers. Many conferences now run parallel tracks for legal, technical, and operational roles. If you work with personal data in any capacity, sessions on consent design, data retention, or vendor risk will apply directly to your work.
What is the difference between privacy and data protection conferences?
In practice the terms overlap heavily. Privacy conferences often emphasize policy, ethics, and consumer trust, while data protection events focus on legal compliance frameworks like GDPR and CCPA. Many organizers use both terms interchangeably. Check the agenda to see whether content skews legal, technical, or strategic before choosing.
Do privacy conferences help with career advancement?
Yes, if you use them strategically. Speaking, volunteering, or joining roundtables raises your visibility far more than passive attendance. Networking with peers at similar career stages often leads to job referrals. Listing relevant conference attendance and CPE credits on your resume signals ongoing professional development to employers.
How do I choose between two conferences on the same dates?
Compare the agendas session by session, not the brands. Count how many talks directly address your current projects. Check speaker affiliations and whether recordings will be available later. Factor in travel cost and time away from work. If one event offers hands-on workshops and the other only panels, the workshop-heavy option usually wins.
What should I bring to a privacy conference?
Bring business cards, a charged laptop or tablet for notes, and a portable charger. Download the conference app in advance to plan sessions. Pack layers since venue temperatures vary. If you plan to claim CPE credits, bring your certification numbers and confirm the check-in process for session tracking.
Are there free or low-cost privacy conferences?
Yes. Regulators, universities, and nonprofit organizations host free or inexpensive events, often half-day or virtual. IAPP local knowledge chapters frequently run low-cost meetings. Vendor-hosted webinars are free but tend to be product-focused, so balance them with independent educational programming to avoid one-sided perspectives.
How do I justify the ROI of a privacy conference?
Track concrete outputs: sessions attended, CPE credits earned, contacts made, and at least one process improvement implemented afterward. Present these to your manager within two weeks of returning. Quantifying time saved or compliance risk reduced turns a vague training expense into a measurable business investment.
What trends will shape privacy conferences in 2027?
Expect heavier focus on AI governance, automated decision-making transparency, and cross-border data transfer mechanisms following evolving regulatory guidance. Sessions on privacy-enhancing technologies like differential privacy and federated learning will grow. State-level US privacy laws and enforcement actions will likely dominate legal tracks alongside global AI regulation.
Sources
- https://iapp.org/conference/
- https://www.privacyguides.org/en/
- https://www.edps.europa.eu/
- https://www.ftc.gov/business-guidance/privacy-security
- https://www.nist.gov/privacy-framework
- https://ico.org.uk/
- https://www.oecd.org/digital/privacy/
- https://www.eff.org/issues/privacy
Related on PULSE
This page will be disappearing soon. Save it to your device for $1 — or read it free while it is here.
@Kory-White- · if Venmo asks, the last 4 of my number are 2012
This page is gone.
This one is off the shelf now. $1 keeps it on your phone for good — the whole page, pictures and diagrams included.
 revopsThe 10 Best Accounting Conferences in 2027
 revopsThe 10 Best Python Conferences in 2027
 revopsThe 10 Best AI Conferences in 2027
 revopsThe 10 Best Venture Capital and Investor Conferences in 2027
 revopsThe 10 Best Quantum Computing Conferences in 2027
 revopsThe 10 Best Franchise Expos in 2027
 revopsThe 10 Best Women in Business Conferences in 2027
 revopsThe 10 Best Data Science and Analytics Conferences in 2027
 revopsThe 10 Best Networking and Telecom Industry Conferences in 2027
 revopsThe 10 Best SaaS Conferences in 2027