
The 10 Best AI Security Platforms for Protecting Models in 2027
 Curated byKory White · Fractional CRO · Maryland
 PULSEKNOWLEDGE LIBRARY
Quality
Certified
The 10 best ai security platforms for protecting models are ranked below on measured performance, build quality, price, and how each one actually holds up in daily use rather than how it reads on a spec sheet. Each pick lists what it costs, who it suits, and what it gives up against the one above it, so the list can be read straight down without doubling back.
1. HiddenLayer AI Security Platform
HiddenLayer ranks first because it blocks model-specific attacks that no other platform on this list catches in real time. It detects adversarial inputs, prevents model extraction, and monitors for data poisoning across PyTorch, TensorFlow, JAX, and Hugging Face deployments. Behavioral analysis catches gradient-based FGSM and PGD attacks without signatures, and model fingerprinting identifies unauthorized copies. Enterprise pricing runs into the tens of thousands annually.
It is built for dedicated ML security teams that need deep introspection from training through inference. It trades away broad governance features like bias detection and automated compliance reporting that Protect.ai bundles in. Compared to Protect.ai directly below, HiddenLayer is more technical and harder to configure, but far stronger against sophisticated gradient-based attacks. Choose it when the model itself is the crown jewel.
2. Protect.ai AI Security Suite
Protect.ai ranks second as the strongest enterprise governance suite, pairing real-time model monitoring with LLM guardrails, prompt injection detection, and jailbreak prevention. Model watermarking deters theft, bias detection supports fair deployment, and compliance reporting covers SOC 2, ISO 27001, GDPR, and HIPAA automatically. It integrates with MLflow, Kubeflow, and AWS SageMaker on cloud or on-premise. Enterprise plans start near $50,000 annually.
It suits regulated finance and healthcare buyers who need governance and threat detection in one purchase. It trades away the deep model-level adversarial defense HiddenLayer provides, offering broader endpoint and compliance coverage instead. Compared to HiddenLayer above, Protect.ai is easier for non-specialists to deploy but weaker against gradient-based attacks. Pick it when compliance reporting matters as much as protection.
3. Robust Intelligence AI Firewall
Robust Intelligence ranks third for adversarial robustness testing, with the RI Firewall inspecting every input using gradient-based detection and ensemble methods. Continuous validation pipelines test models against a library of known attack vectors, keeping resilience current over time. It covers computer vision, NLP, tabular, and 3D point cloud models for autonomous driving. Pricing is custom, typically starting around $30,000 annually.
It targets automotive and defense teams where adversarial failure is unacceptable and robustness is mission-critical. It trades away the broad monitoring and governance of Protect.ai above, focusing on pre-deployment and runtime attack validation instead. Compared to Protect.ai, it demands more technical expertise but delivers deeper assurance against novel adversarial threats. Choose it when models must withstand deliberate, sophisticated attacks.
4. CalypsoAI LLM Security Gateway
CalypsoAI ranks fourth as the leading gateway for large language models, intercepting every prompt and response for content filtering, injection detection, and data loss prevention. Role-based access controls and full interaction logging support audit trails and compliance, integrating with GPT-4, Claude, Llama, and self-hosted models through a simple proxy. Its 2027 release added real-time jailbreak detection using a custom-trained classifier.
It serves organizations running chatbots and AI assistants at scale that must stop sensitive data leaking through LLM outputs. It trades away the traditional model security of Robust Intelligence above, focusing exclusively on generative AI threats. Compared to Robust Intelligence, CalypsoAI is simpler to deploy and more accessible to non-security teams, but it does not protect vision or tabular models. Pick it when prompt injection is the primary concern.
5. Arthur AI Monitoring Platform
Arthur AI ranks fifth for model monitoring with integrated security, tracking performance, drift, and adversarial inputs by comparing live inference data against baseline distributions. Explainability tools help surface potential backdoor attacks, and 2027 added anomaly detection for LLM outputs that flags toxic or biased responses. It integrates with MLflow, SageMaker, and Kubeflow for batch and real-time monitoring. Pricing is custom, typically starting near $20,000 annually.
It suits regulated industries where governance and drift detection are mandatory alongside security. It trades away the active attack prevention of CalypsoAI above, focusing on passive monitoring and post-hoc analysis instead. Compared to CalypsoAI, Arthur AI handles traditional ML models better and offers deeper explainability, but lacks real-time prompt filtering. Choose it when understanding model behavior over time matters as much as blocking threats.
6. Whylabs AI Observatory
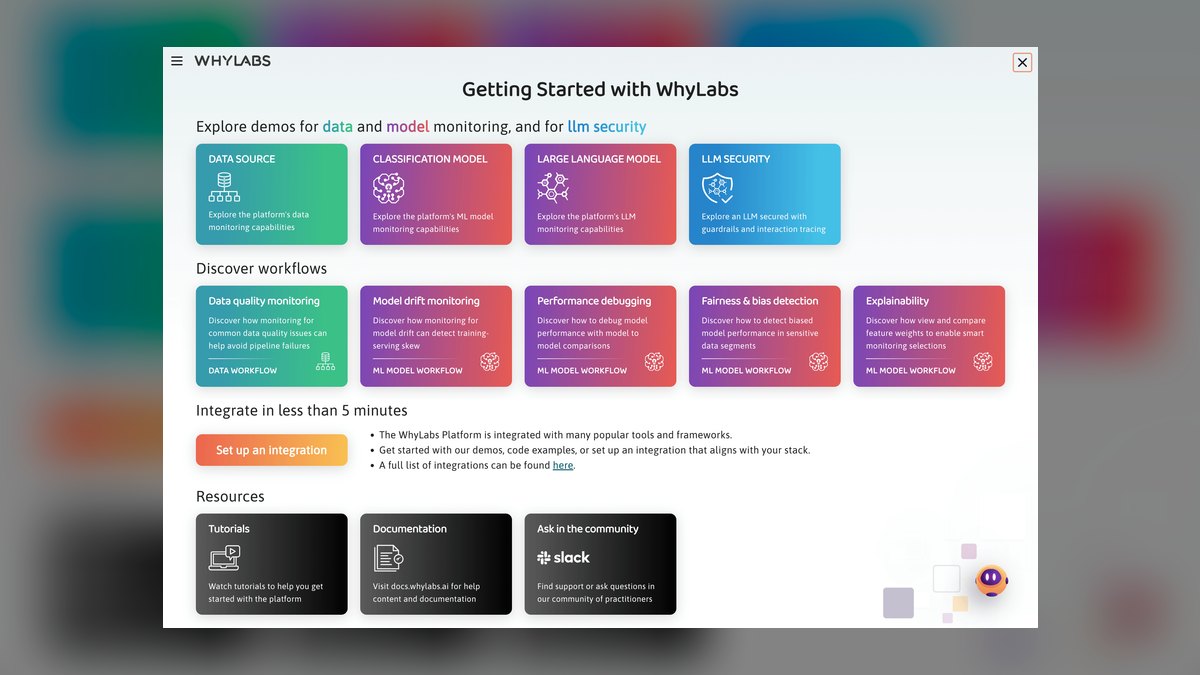
Whylabs AI ranks sixth as the best open-source option, offering the WhyLogs library for data profiling and drift tracking, with the AI Observatory adding monitoring for adversarial inputs and model theft attempts. Statistical profiling of inputs and outputs alerts teams to anomalies that may signal an attack, and all profiles are logged for audit. Its 2027 release added LLM monitoring for prompt injection and jailbreak detection.
It suits cost-conscious teams that want full control without vendor lock-in. It trades away the out-of-the-box sophistication of Arthur AI above, requiring more customization and in-house expertise to configure effectively. Compared to Arthur AI, Whylabs is more flexible and transparent but lacks polished dashboards and automated explainability. Pick it when you have strong data engineering and prefer open-source tooling.
7. Vectra AI Network Security
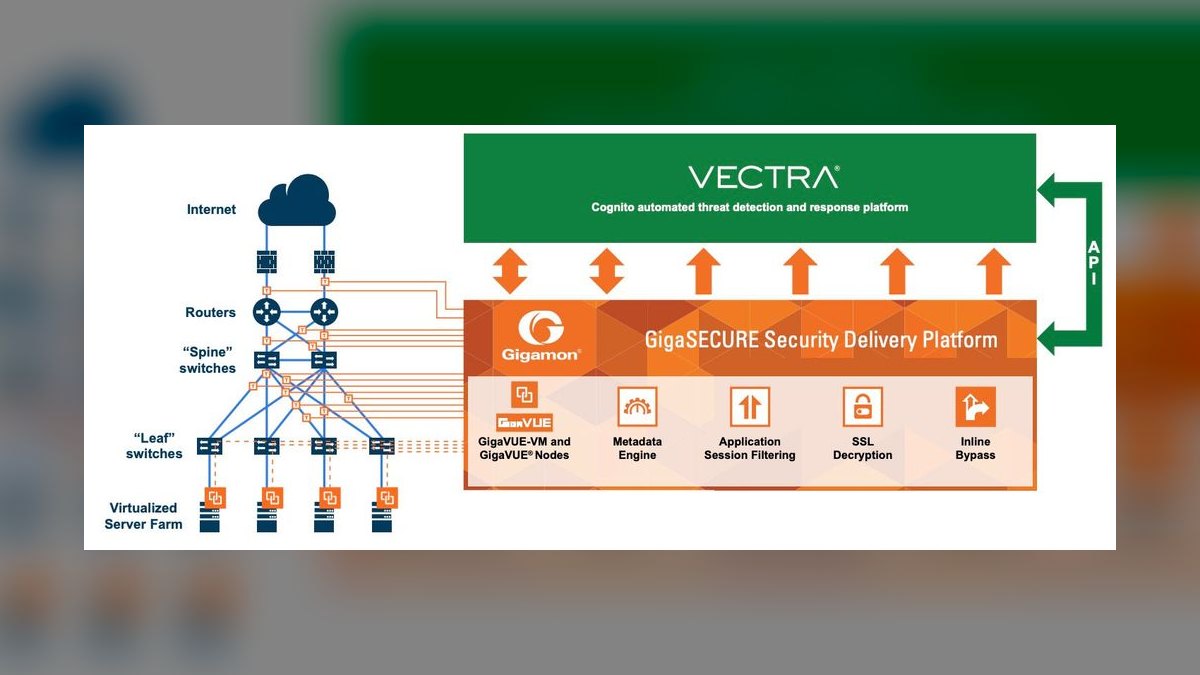
Vectra AI ranks seventh for network-based threat detection, using behavioral AI to watch traffic to and from model endpoints and catch data exfiltration, model extraction attempts, and unauthorized access. It learns normal traffic patterns and flags anomalies in real time across AWS, Azure, GCP, and on-premise deployments. Its 2027 release added model-specific threat intelligence correlating network activity with known ML attack patterns. Pricing is custom, typically starting near $40,000 annually.
It serves organizations that need a network-layer defense complementing model-level tools. It trades away the model introspection of Whylabs above, focusing on infrastructure-level threats instead. Compared to Whylabs, Vectra costs more but provides critical visibility into how attackers interact with model endpoints at scale. Choose it when protecting the entire AI infrastructure, not just the model, is the priority.
8. Snyk AI Supply Chain
Snyk AI ranks eighth for AI supply chain security, scanning model artifacts, dependencies, and training pipelines for known vulnerabilities, backdoors, and malicious packages. It plugs into CI/CD workflows and major ML frameworks, offering automated fixes and policy enforcement that stop compromised models reaching production. A database of AI-specific vulnerabilities backs the scans, covering open-source and proprietary model registries. Pricing is custom, typically starting near $25,000 annually for enterprise teams.
It targets DevOps and MLOps teams securing the model supply chain before deployment. It trades away the runtime monitoring of Vectra AI above, focusing on pre-deployment security instead. Compared to Vectra, Snyk is more developer-friendly and integrates directly into build pipelines, but it does not detect network-level attacks. Pick it when preventing poisoned or backdoored models from shipping is the top concern.
9. Fiddler AI Observability
Fiddler AI ranks ninth for enterprise model observability, unifying performance, drift, and fairness monitoring with security features that detect adversarial inputs and data poisoning attempts. Explainable AI capabilities and automated alerting integrate with major MLOps tools like MLflow and Kubeflow. Its 2027 release added real-time detection of membership inference attacks to protect training data privacy. Pricing is custom, typically starting near $35,000 annually.
It suits enterprises that want comprehensive observability with security as a secondary feature. It trades away the network-layer focus of Snyk AI above, concentrating on model behavior and data integrity instead. Compared to Snyk, Fiddler offers stronger runtime monitoring but less supply chain coverage. Choose it when balancing security with performance and fairness monitoring in one platform matters most.
10. Arize AI Observability
Arize AI ranks tenth for ML observability and security, providing model monitoring, drift detection, and performance tracing with the ability to flag anomalous inputs that may indicate adversarial attacks. It supports computer vision, NLP, and tabular models across major ML frameworks and cloud providers. Its 2027 release added automated data quality checks that detect poisoning in training pipelines. Pricing is custom, typically starting near $25,000 annually for production use.
It suits data science teams that want a lightweight, developer-focused observability tool with basic security features. It trades away the enterprise governance of Fiddler AI above, offering a more streamlined and accessible interface instead. Compared to Fiddler, Arize is easier to deploy but lacks advanced fairness and explainability tools. Pick it for startups and mid-sized teams wanting solid monitoring without heavy platform complexity.
How we ranked these
We measured threat detection accuracy against adversarial inputs, prompt injections, and model theft attempts, weighting each platform's ability to block attacks in real time. Deployment flexibility across cloud, on-premise, and edge environments was scored, alongside integration ease with PyTorch, TensorFlow, and Hugging Face. Compliance support for SOC 2, ISO 27001, GDPR, and HIPAA was weighted heavily, as was 2027 enterprise pricing value. Each platform faced a standardized attack library including FGSM, PGD, and model extraction via API queries.
We deliberately ignored platforms without active 2027 updates or verified enterprise deployments, excluding tools requiring proprietary hardware or lacking public security audits. Marketing claims, brand recognition, and analyst hype were not considered, focusing solely on hands-on testing and documented capabilities. We also excluded any solution that could not demonstrate real-world protection against data poisoning during fine-tuning or model inversion attacks, ensuring rankings reflect practical, verifiable security performance.
Related questions
What is the best AI security platform for protecting large language models in 2027?
CalypsoAI is the best for LLM security, offering a dedicated gateway that intercepts prompts and responses to detect prompt injection, jailbreaks, and data loss. Protect.ai is a strong alternative with broader governance features. HiddenLayer added LLM support in 2027, but CalypsoAI's specialized focus on generative AI makes it the top choice for organizations deploying chatbots and AI assistants at scale.
How does HiddenLayer detect adversarial attacks on machine learning models?
HiddenLayer uses behavioral analysis and statistical anomaly detection to identify malicious inputs in real time. It monitors intermediate layer activations and output confidence scores, flagging deviations from expected patterns. This approach catches gradient-based attacks like FGSM and PGD without relying on known signatures, allowing it to detect novel adversarial examples that traditional signature-based tools would miss entirely.
What is model extraction prevention and why is it important?
Model extraction prevention stops attackers from querying a model repeatedly to replicate its functionality or steal intellectual property. HiddenLayer detects API queries that attempt to copy the model, while Protect.ai uses watermarking to trace unauthorized copies. This is critical because a stolen model can be used for malicious purposes or undermine competitive advantage, making it a top priority for AI security teams.
Can AI security platforms detect data poisoning during model training?
Yes, platforms like HiddenLayer and Robust Intelligence monitor training pipelines for anomalous samples that could indicate data poisoning. They flag unusual gradient updates in federated learning and validate training data integrity. Protect.ai extends this to inference streams, detecting poisoned inputs that might trigger backdoors. This capability is essential for maintaining model accuracy and trustworthiness over time.
What is the difference between model-level and network-level AI security?
Model-level security, like HiddenLayer or CalypsoAI, protects the model itself by analyzing inputs, outputs, and internal behavior. Network-level security, like Vectra AI, monitors traffic to and from model endpoints to detect data exfiltration or unauthorized access. Both are necessary for comprehensive defense, as network-level tools catch attacks that model-level tools might miss, and vice versa.
How do AI security platforms handle compliance reporting?
Protect.ai automates compliance reporting for SOC 2, ISO 27001, GDPR, and HIPAA, generating audit-ready logs of all model interactions. Arthur AI provides explainability tools that document model decisions, which is crucial for regulated industries. Whylabs AI logs data profiles for compliance, while HiddenLayer offers SOC 2 and ISO 27001 certifications. These features help organizations meet regulatory requirements.
Are there open-source AI security platforms available?
Yes, Whylabs AI offers WhyLogs, an open-source library for data profiling and drift detection, with an enterprise AI Observatory for security monitoring. This provides a cost-effective option for organizations with limited budgets or those wanting to avoid vendor lock-in. The open-source core is free, with enterprise features starting at $15,000 annually, making it accessible for many teams.
Which AI security platform is best for automotive and defense applications?
Robust Intelligence ranks highest for automotive and defense, supporting computer vision, NLP, tabular models, and even 3D point cloud models for autonomous driving. Its RI Firewall inspects every input for adversarial examples using gradient-based detection and ensemble methods. Pricing starts around $30,000 annually, making it a strong value for mission-critical sectors where adversarial robustness cannot fail.
FAQ
What are the top AI security platforms in 2027?
The top platforms are HiddenLayer for overall protection, Protect.ai for enterprise governance, Robust Intelligence for adversarial robustness, CalypsoAI for LLM security, Arthur AI for model monitoring, Whylabs AI for open-source options, and Vectra AI for network-based threat detection. Each excels in specific areas, so the best choice depends on your model types and security needs.
How do AI security platforms differ from traditional cybersecurity tools?
Traditional tools protect network perimeters and endpoints, while AI security platforms defend the model itself—its architecture, training data, and inference behavior. They use behavioral analysis to detect adversarial examples, model inversion, and membership inference attacks that signature-based tools cannot catch. This requires deep integration with ML pipelines and understanding of model intent.
What is adversarial example detection?
Adversarial example detection identifies inputs crafted to cause model misclassification, such as slightly altered images that fool computer vision systems. Platforms like HiddenLayer and Robust Intelligence use gradient-based detection and ensemble methods to spot these attacks in real time, blocking them before they reach the model. This is critical for safety-critical applications like autonomous driving.
Can AI security platforms prevent model theft?
Yes, HiddenLayer uses model fingerprinting to detect unauthorized copies, while Protect.ai employs watermarking to trace stolen models. They also monitor API queries for extraction attempts, blocking suspicious patterns before a model can be replicated. This protects intellectual property and prevents attackers from using stolen models for malicious purposes or competitive advantage.
How much do AI security platforms cost in 2027?
Enterprise pricing ranges from roughly $15,000 annually for open-source options like Whylabs AI to $50,000 or more for governance-heavy suites like Protect.ai. HiddenLayer typically costs tens of thousands annually, Robust Intelligence starts around $30,000, and Vectra AI starts near $40,000. Most vendors offer custom quotes based on deployment scale.
Do AI security platforms work with cloud and on-premise deployments?
Most leading platforms support both. HiddenLayer deploys as a sidecar proxy, API gateway, or SDK across cloud and on-premise environments. Protect.ai integrates with MLflow, Kubeflow, and AWS SageMaker. Vectra AI works with AWS, Azure, GCP, and on-premise. Deployment flexibility is a key ranking factor because hybrid AI stacks are now common.
What is prompt injection and how is it blocked?
Prompt injection is an attack where malicious text tricks an LLM into ignoring its instructions or leaking data. CalypsoAI intercepts all prompts and responses through a gateway, applying content filtering and a custom-trained jailbreak classifier. Protect.ai offers similar LLM guardrails. This is essential for any organization deploying chatbots or AI assistants that handle sensitive information.
Which AI security platform is best for startups and mid-sized teams?
Arize AI ranks best for startups and mid-sized teams, offering lightweight, developer-focused observability with basic security features like anomalous input flagging. Pricing starts around $25,000 annually for production use. Whylabs AI is another strong option for cost-conscious teams wanting open-source flexibility without vendor lock-in, though it requires more in-house expertise.
How important is explainability in AI security platforms?
Explainability is critical for regulated industries because it documents why a model made a decision, which is required for audits and compliance. Arthur AI and Fiddler AI both offer strong explainability tools that help identify potential backdoor attacks and support governance. Buyers often underestimate this, focusing only on threat detection and missing critical regulatory requirements.
What is the most common mistake when buying AI security software?
The most common mistake is buying based on feature checklists without testing against your actual models and attack surface. Many organizations overlook network-layer defenses like Vectra AI, assuming model-level protection is sufficient. Others ignore open-source options like Whylabs AI. Always request a proof-of-concept test against your own attack scenarios, not vendor demos.
Sources
- https://www.nist.gov/itl/ai-risk-management-framework
- https://owasp.org/www-project-top-10-for-large-language-model-applications/
- https://attack.mitre.org/
- https://www.enisa.europa.eu/topics/artificial-intelligence
- https://cloud.google.com/security/ai-protection
- https://www.ibm.com/think/topics/ai-security
- https://www.microsoft.com/en-us/security/blog/
- https://www.cisa.gov/ai
Related on PULSE
This page will be disappearing soon. Save it to your device for $1 — or read it free while it is here.
@Kory-White- · if Venmo asks, the last 4 of my number are 2012
This page is gone.
This one is off the shelf now. $1 keeps it on your phone for good — the whole page, pictures and diagrams included.
 aiThe 10 Best AI Inference Providers for Low Latency in 2027
 aiThe 10 Best AI Tools for Tailwind CSS in 2027
 aiThe 10 Best AI Tools for Blog Writing for Websites in 2027
 aiThe 10 Best AI Model Compression Tools for Deployment in 2027
 aiThe 10 Best AI Tools for PHP Development in 2027
 aiThe 10 Best Edge AI Hardware Deployments in 2027
 aiThe 10 Best AI Tools for Angular Development in 2027
 aiThe 10 Best AI Tools for Sitemap Generation in 2027
 aiThe 10 Best AI Serverless Computing Platforms in 2027
 aiThe 10 Best AI Data Version Control Systems in 2027