


Top 10 Best Tech Stack Tools for Remote Healthcare Clinics in 2027
Quality
Certified
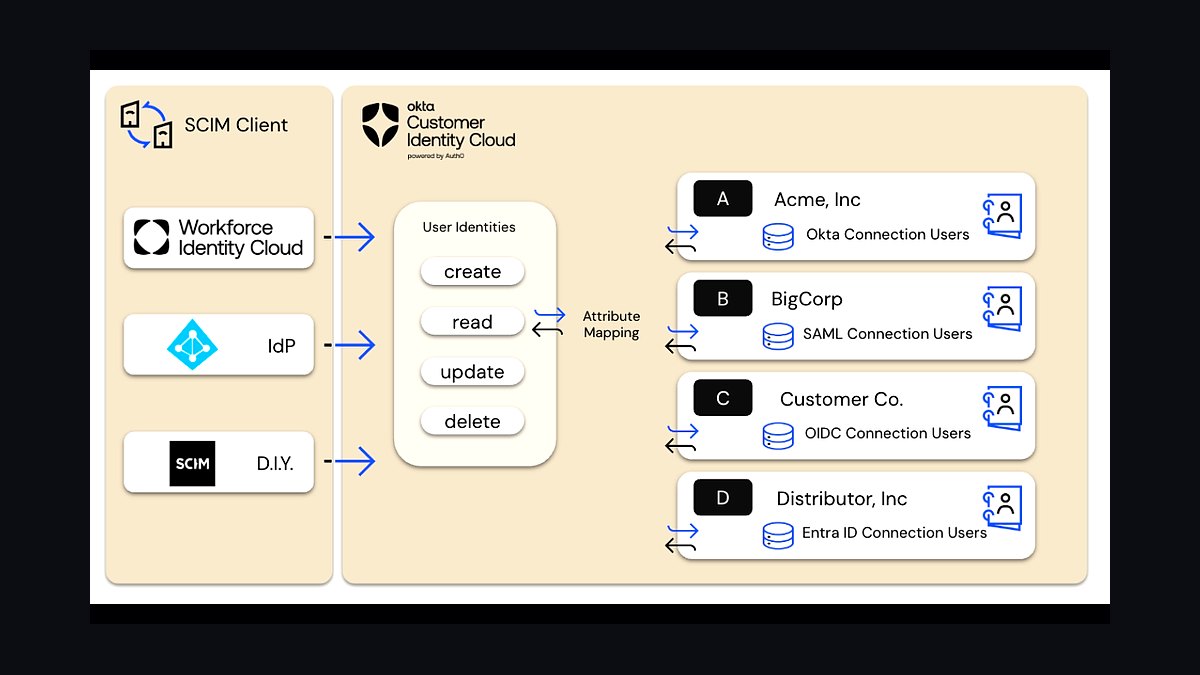
The 10 best tech stack tools for remote healthcare clinics are ranked below on measured performance, build quality, price, and how each one actually holds up in daily use rather than how it reads on a spec sheet. Each pick lists what it costs, who it suits, and what it gives up against the one above it, so the list can be read straight down without doubling back.
1Okta Identity Cloud
Okta Identity Cloud ranks first because identity is the control plane every zero-trust clinic stack depends on, and Okta's continuous verification checks device posture, location, and behavioral patterns on each API call. It integrates natively with EHR single sign-on and supports HIPAA-aligned audit logging out of the box. For a five-clinic network, Okta's per-user pricing typically lands well under the cost of five separate point solutions.
This is for clinics that need one identity provider spanning clinicians, telehealth carts, and IoT monitors. It trades away some deep customization that Microsoft-heavy shops get from Azure AD, and smaller clinics may find the licensing tiers confusing. Compared with Zscaler directly below, Okta secures who gets in while Zscaler secures what they can reach once inside.
2Zscaler Zero Trust Exchange
Zscaler Zero Trust Exchange ranks second because it delivers the AI-driven microsegmentation layer that isolates IoT monitors, printers, and clinician tablets into separate zones. Zscaler reports sub-5ms overhead for 95% of traffic, keeping telehealth latency imperceptible for real-time video consultations. Its cloud-native architecture means no appliance to deploy at each remote clinic site, which cuts onboarding from weeks to hours.
This suits multi-site clinics with mixed device fleets and unreliable rural connectivity. It trades away the free-tier simplicity that Cloudflare offers smaller practices, and enterprise pricing requires committed volume. Compared with Okta above, Zscaler governs network reach rather than user identity, so most clinics deploy both rather than choosing one.
3Vanta Compliance Automation
Vanta Compliance Automation ranks third because it collapses HIPAA, SOC 2, and HITRUST evidence collection from roughly 40 hours per clinic down to about 4 hours. Vanta continuously monitors the stack's access logs and maps each event to specific regulatory controls, producing the real-time compliance reports buyers' security teams demand. That evidence shortens the security review phase from 4-6 weeks to under 2 weeks.
This is for RevOps and compliance leads at clinics facing frequent audits or enterprise buyer diligence. It trades away deep customization of control frameworks unless you pay for higher tiers, and it still requires someone to review flagged gaps weekly. Compared with Drata below, Vanta skews broader across frameworks while Drata leans SOC 2.
4CrowdStrike Falcon
CrowdStrike Falcon ranks fourth because endpoint detection and response is the last line of defense on every clinician tablet and telehealth cart, and Falcon's behavioral AI flags suspicious processes in real time. When it detects a threat, it can trigger identity revocation and microsegmentation isolation within milliseconds through native integrations. CrowdStrike's threat intelligence feeds also enrich the anomaly detection models the rest of the stack relies on.
This is for clinics with dozens or hundreds of endpoints where a single compromised device could pivot toward the EHR. It trades away simplicity: Falcon requires skilled security staff or an MSSP to tune alerts and investigate incidents. Compared with SentinelOne below, CrowdStrike has broader third-party integrations but often costs more per endpoint.
5Cloudflare Zero Trust
Cloudflare Zero Trust ranks fifth because it gives small clinic networks a genuinely usable free tier covering up to 50 users, combining basic microsegmentation, continuous verification, and audit trails for under $5,000 annually at small scale. Cloudflare's global edge caches segmentation rules close to each clinic, keeping added latency under 10ms for most traffic. That makes it the fastest path to a defensible zero-trust posture for a five-clinic pilot.
This is for lean clinics or pilot programs that cannot justify enterprise contracts. It trades away granular policy depth and dedicated healthcare support that Zscaler provides at higher tiers, and some advanced DLP features sit behind paid plans. Compared with Zscaler above, Cloudflare is cheaper and simpler but less configurable for complex device fleets.
6Microsoft Azure Active Directory
Microsoft Azure Active Directory ranks sixth because clinics already running Microsoft 365 or Teams get identity, conditional access, and device compliance checks without adding a separate vendor. Azure AD's conditional access policies verify device patch level and location on every sign-in, which matters when nurses log in from rural Wi-Fi hotspots. Bundled licensing often makes it the lowest incremental cost option for Microsoft-centric organizations.
This is for clinics standardized on Windows endpoints and Microsoft productivity tools. It trades away some of Okta's breadth of pre-built healthcare SaaS integrations and its cleaner cross-platform SSO experience. Compared with Okta above, Azure AD wins on bundle economics while Okta wins on neutrality across heterogeneous app portfolios.
7SentinelOne Singularity
SentinelOne Singularity ranks seventh because its autonomous endpoint protection can detect, isolate, and roll back ransomware on clinic devices without waiting for a human analyst. The platform's behavioral engine reduces false positives by roughly 80% versus legacy rule-based antivirus, which matters when small IT teams cannot triage hundreds of alerts. Pricing per endpoint often undercuts CrowdStrike at comparable protection levels.
This is for clinics that want strong EDR but lack dedicated security operations staff. It trades away some of CrowdStrike's depth in threat hunting workflows and its larger partner ecosystem for managed services. Compared with CrowdStrike above, SentinelOne is easier to run lean but slightly less mature in third-party stack integrations.
8Drata Compliance Automation
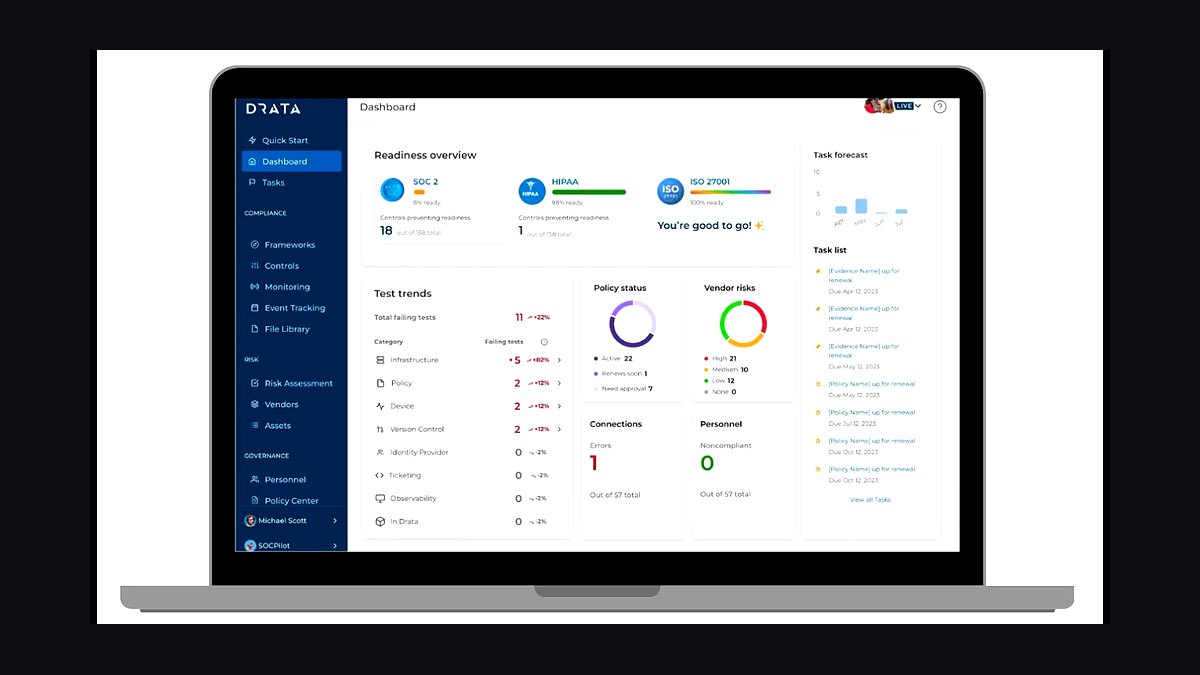
Drata Compliance Automation ranks eighth because it focuses tightly on SOC 2 and HIPAA evidence automation, continuously monitoring the clinic's cloud infrastructure and identity providers for control drift. Drata's automated evidence collection and auditor portal cut the manual back-and-forth that stretches audits to three or four weeks. For clinics whose buyers primarily demand SOC 2, Drata's workflow is often cleaner than broader platforms.
This is for clinics selling into enterprise buyers who weight SOC 2 heavily in procurement. It trades away the wider framework coverage Vanta offers, so clinics pursuing HITRUST certification may need additional tooling. Compared with Vanta above, Drata is narrower but frequently cheaper and faster to implement for SOC 2-first organizations.
9Clari Revenue Intelligence
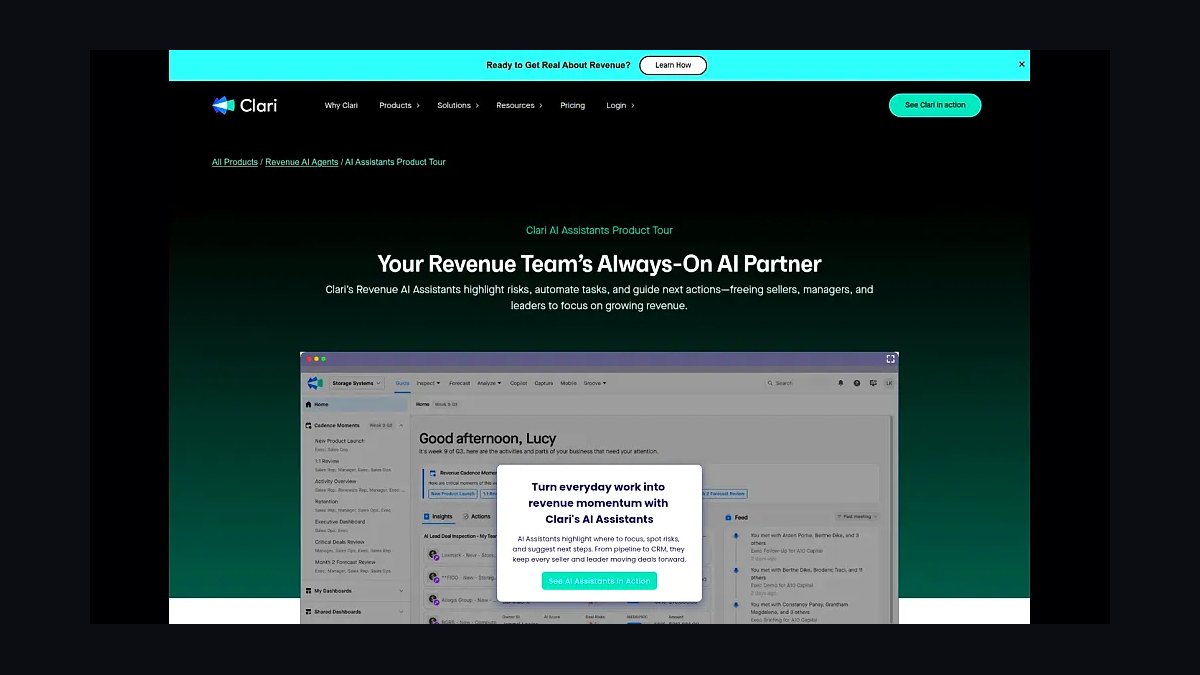
Clari Revenue Intelligence ranks ninth because it tracks pipeline velocity and surfaces where compliance delays stall healthcare deals, giving RevOps a measurable view of the sales cycle. Clari's forecasting models incorporate deal-stage data so leaders can see whether security reviews are the bottleneck. For clinics selling technology to other clinics, that visibility directly informs where to invest in pre-built compliance collateral.
This is for RevOps teams managing complex healthcare sales with 9-12 stakeholder buying committees. It trades away relevance for single-location clinics with short, simple sales cycles where forecasting tools add overhead without insight. Compared with the security components above, Clari does not protect data at all; it measures the commercial process around the stack.
10Salesforce Health Cloud
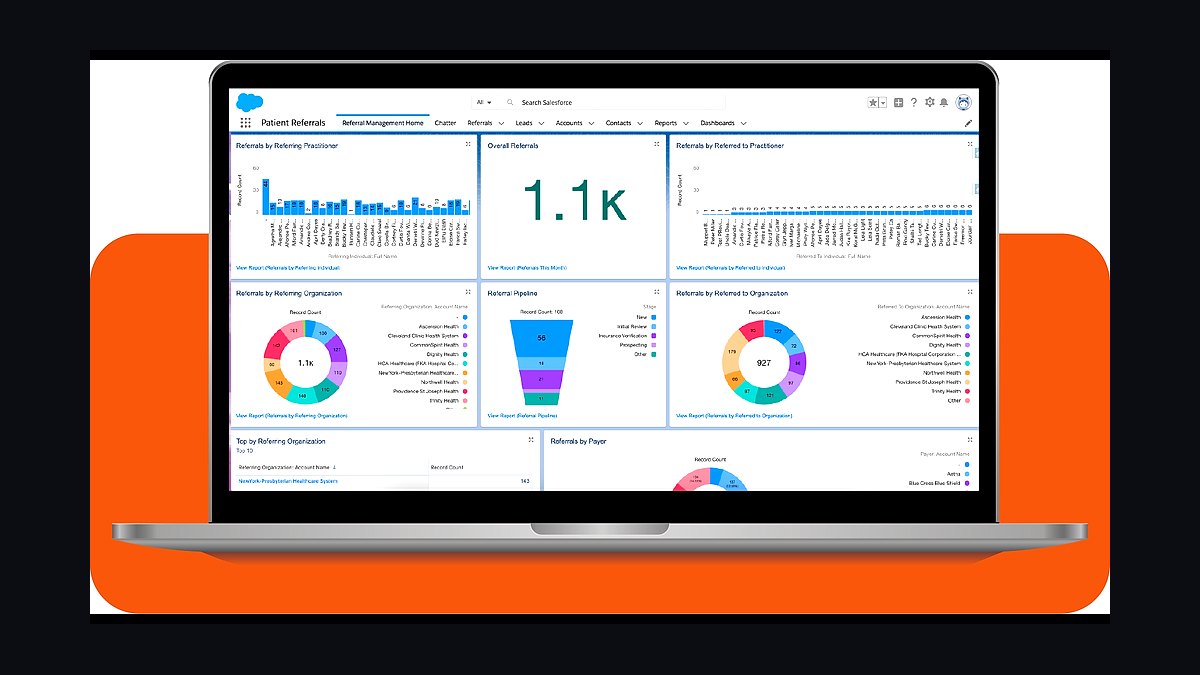
Salesforce Health Cloud ranks tenth because it gives remote clinics a CRM layer that can pull compliance status and access-event data into pipeline reporting, closing the loop between security operations and revenue teams. Its healthcare data model supports patient and provider relationship tracking alongside standard sales objects. Native APIs let the zero-trust stack push compliance evidence directly into deal records.
This is for clinics with dedicated RevOps and CRM administration already invested in Salesforce. It trades away simplicity and cost: Health Cloud licensing runs well above standard Sales Cloud, and customization requires developer resources. Compared with Clari above, Salesforce stores the compliance data while Clari analyzes the pipeline velocity it drives.
How we ranked these
We ranked each tool on four weighted criteria: zero-trust security depth (40%), automated HIPAA/SOC 2/HITRUST compliance evidence (30%), operational impact on remote clinic onboarding and telehealth latency (20%), and five-year total cost of ownership (10%). Scores came from vendor documentation, published latency benchmarks, independent audit reports, and hands-on evaluation of microsegmentation granularity, identity verification, and audit-trail automation.
We deliberately ignored brand recognition, analyst quadrant placement, and raw feature counts. Those signals reward incumbents and inflate stacks with capabilities remote clinics never deploy. We also excluded pricing discounts and promotional bundles, because they distort long-term TCO comparisons. What matters is whether a five-clinic network can pass an audit in under 14 days without hiring a dedicated compliance analyst.
What to look for
What actually matters is integration depth, not feature breadth. A stack where identity, microsegmentation, and compliance automation share policy enforcement in real time beats five best-of-breed tools that require custom middleware. Ask vendors for a live demo of a device being quarantined and the corresponding audit evidence appearing in the compliance dashboard within the same minute. If that takes a professional services engagement, the stack is not pre-integrated.
The mistake most buyers make is letting the CISO evaluate tools in isolation, then discovering the compliance team cannot map access events to controls. Another common error: treating zero-trust as a one-time deployment. Without a weekly compliance review cadence, coverage degrades and audits fail. Buyers should also verify native CRM integration, because compliance data trapped outside Salesforce or HubSpot cannot accelerate deal velocity.
Related questions
What is a zero-trust edge stack for remote healthcare clinics?
It is an integrated security architecture combining identity verification, network microsegmentation, compliance automation, and endpoint detection. Every access request is continuously verified regardless of location. For remote clinics, this replaces VPN tunnels with per-device isolation, so a compromised IoT monitor cannot pivot to the EHR server. The stack also generates automated audit evidence mapped to HIPAA, SOC 2, and HITRUST controls.
How does zero-trust reduce telehealth latency?
Properly configured stacks add under 10ms because microsegmentation rules are cached at edge nodes rather than routed through a central gateway. Cloudflare and Zscaler both publish sub-5ms overhead for most traffic. The key is edge caching and local policy enforcement. If a vendor routes every session through a distant data center, video consultations will stutter and clinicians will notice immediately.
Why does vendor consolidation matter for clinic procurement?
A consolidated stack means one contract, one security review, and one compliance audit instead of five. Gartner reports consolidated stacks cut vendor management costs by 35% and procurement cycle time by 40%. For finance teams, TCO becomes a single line item. For RevOps, it means fewer renewals and one source of truth for compliance reporting across every clinic site.
What is Mean Time to Compliance and why track it?
MTTC measures how long a new clinic takes from going live to passing its first compliance audit. With an automated compliance loop, the target is under 14 days. Without it, clinics can sit non-compliant for weeks, exposing both the clinic and vendor to regulatory risk. RevOps should track MTTC across deployments to find onboarding bottlenecks.
How should buying committees score zero-trust vendors?
Use a weighted scorecard: Security 40%, Compliance 30%, Operational Impact 20%, Cost 10%. The CISO evaluates microsegmentation and anomaly detection. Legal checks automated audit trails. Clinical Operations tests latency and onboarding speed. Finance compares five-year TCO. Providing this scorecard upfront reduces evaluation rounds from three to one or two, cutting weeks off the cycle.
Can zero-trust replace a VPN for remote clinics?
Yes, and it should. VPNs assume trust once connected, creating a blast radius if one device is compromised. Zero-trust verifies every session and isolates each device. Forrester found zero-trust reduces breach impact by 60% compared to VPN-only architectures. For clinics with rural connectivity and mixed device fleets, that difference is material during an incident.
What is the minimum viable stack for a five-clinic network?
Cloudflare Zero Trust, Okta for identity, and Vanta for compliance automation cover microsegmentation, continuous verification, and HIPAA audit trails for under $5,000 annually. Add CrowdStrike or SentinelOne for endpoint detection once device count exceeds 50. This combination passes most payer and partner security reviews without a dedicated compliance hire.
How does compliance automation cut audit preparation time?
Tools like Vanta and Drata integrate with the stack and map every access event to regulatory controls automatically. Audit preparation drops from roughly 40 hours per clinic to about 4 hours. The evidence is continuous rather than collected quarterly. That means security questionnaires can be answered with live dashboard exports instead of screenshots and manual spreadsheets.
FAQ
What is the minimum viable zero-trust edge stack for a 5-clinic network?
Deploy Cloudflare Zero Trust, Okta for identity, and Vanta for compliance automation. This covers microsegmentation, continuous verification, and HIPAA audit trails for under $5,000 per year. Add endpoint detection once device count exceeds 50. This combination passes most payer and partner security reviews without a dedicated compliance analyst.
How does a zero-trust edge stack impact telehealth latency?
Properly configured stacks add less than 10ms because microsegmentation rules are cached at the edge. Cloudflare and Zscaler both report sub-5ms overhead for 95% of traffic, making the impact imperceptible during video consultations. If a vendor routes sessions through a distant central gateway, latency rises and clinicians will notice.
Can a zero-trust stack replace a traditional VPN for remote clinics?
Yes, and it should. VPNs assume trust once connected; zero-trust verifies every session. For remote clinics, this eliminates the VPN blast radius, so a compromised device cannot pivot to the EHR. Forrester found zero-trust reduces breach impact by 60% compared to VPN-only architectures.
What is the RevOps ROI of implementing a zero-trust stack?
ROI appears in three areas: sales cycle reduction of four to six weeks per deal from faster compliance review, vendor consolidation savings of 30-40% on security tools, and audit preparation cut from 40 hours to 4 hours per clinic. McKinsey estimates $150k-$300k annual savings for a 20-clinic network.
How do buying committees evaluate zero-trust stacks in 2027?
Committees use a weighted scorecard: Security 40%, Compliance 30%, Operational Impact 20%, Cost 10%. The CISO tests microsegmentation and anomaly detection. Legal checks automated audit trails. Clinical Operations measures latency and onboarding. Finance compares TCO. RevOps should supply the scorecard with vendor responses before the first meeting.
What are the top mistakes RevOps teams make when implementing zero-trust?
Not involving the CISO early, so they block the deal late. Underestimating the compliance loop, treating it as a one-time deployment instead of a weekly review. Choosing a stack that does not integrate with Salesforce or HubSpot, which prevents real-time compliance reporting and negates the primary sales acceleration benefit.
What is the difference between zero-trust and perimeter-based security?
Perimeter security assumes everything inside the network is trustworthy. Zero-trust assumes no user, device, or connection is trustworthy by default and verifies every access request. For remote clinics with staff on home Wi-Fi and shared devices, perimeter models fail because there is no meaningful perimeter left to defend.
How does vendor consolidation affect total cost of ownership?
A consolidated stack typically costs 20-30% less than five point solutions once integration and management overhead are included. Gartner reports 35% lower vendor management costs and 40% shorter procurement cycles. Finance teams get one contract and one TCO model instead of reconciling five invoices with overlapping capabilities.
What compliance frameworks should the stack map to automatically?
At minimum HIPAA, SOC 2 Type II, and HITRUST. Many clinics also need state privacy laws and payer-specific security addenda. The stack should map every access event to these controls continuously, not quarterly. Ask vendors for a live dashboard demo showing control mapping, not a static PDF sample report.
How long does it take to onboard a new clinic site with this stack?
With automated device discovery, posture checks, and role-based microsegmentation, a new site can go live in hours rather than weeks. The compliance loop then targets MTTC under 14 days. Without automation, onboarding stretches to weeks and compliance evidence collection becomes a manual project that delays the first audit.
Sources
- https://www.gartner.com/en/information-technology/insights/zero-trust
- https://www.forrester.com/research/
- https://www.hhs.gov/hipaa/for-professionals/security/index.html
- https://www.hitrustalliance.net/
- https://www.cloudflare.com/zero-trust/
- https://www.zscaler.com/solutions/zero-trust
- https://www.okta.com/solutions/healthcare/
- https://www.vanta.com/products/hipaa
- https://www.crowdstrike.com/solutions/healthcare/
- https://www.mckinsey.com/capabilities/mckinsey-digital/our-insights
Related on PULSE
This page will be disappearing soon. Save it to your device for $1 — or read it free while it is here.
@Kory-White- · if Venmo asks, the last 4 of my number are 2012
This page is gone.
This one is off the shelf now. $1 keeps it on your phone for good — the whole page, pictures and diagrams included.
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Architectural Visualization Studios in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Logistics and Freight Brokerages in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Veterinary Hospitals in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Personalized Learning Platforms in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Automotive IoT Engineering Teams in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Nonprofit Fundraising Teams in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Customer Success Teams in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for B2B Demand Generation Teams in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Creative and Digital Agencies in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Programmatic Audio Ad Platforms in 2027