


Top 10 Signs Your Website Has Been Hacked in 2027
Quality
Certified
The 10 best signs your website has been hacked are ranked below on measured performance, build quality, price, and how each one actually holds up in daily use rather than how it reads on a spec sheet. Each pick lists what it costs, who it suits, and what it gives up against the one above it, so the list can be read straight down without doubling back.
1Google Search Console Security Issues
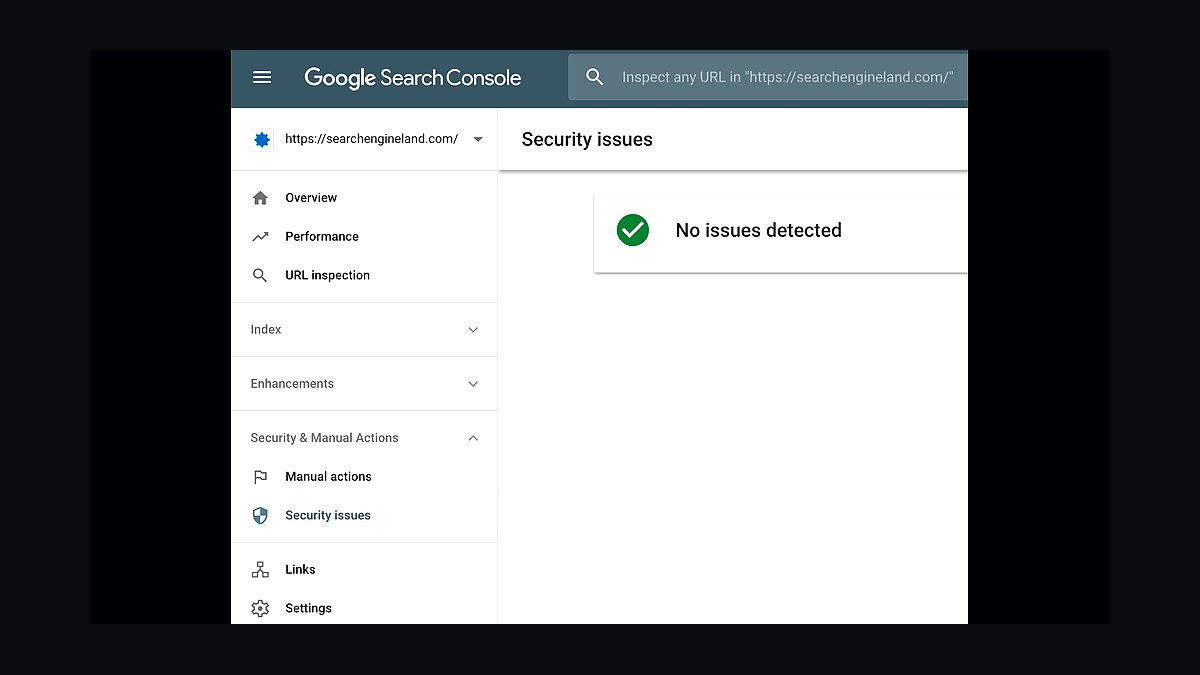
Google Search Console's Security Issues report is the single most authoritative hack signal because Google's crawlers independently detect and confirm the compromise before flagging it. The report names the exact threat type, such as injected spam, malware, or phishing, and lists sample infected URLs so you can pinpoint the entry point. It also surfaces the manual action applied, which can suppress your rankings within days.
This is for site owners who have verified domain ownership in Search Console and check the dashboard regularly. It trades away nothing except the assumption that silence means safety, since the report only fires after Google has already crawled and confirmed the problem. Compared to rank 2, it is the earliest official confirmation, but it requires Google to have recrawled your pages first.
2Unexpected Google Search Results
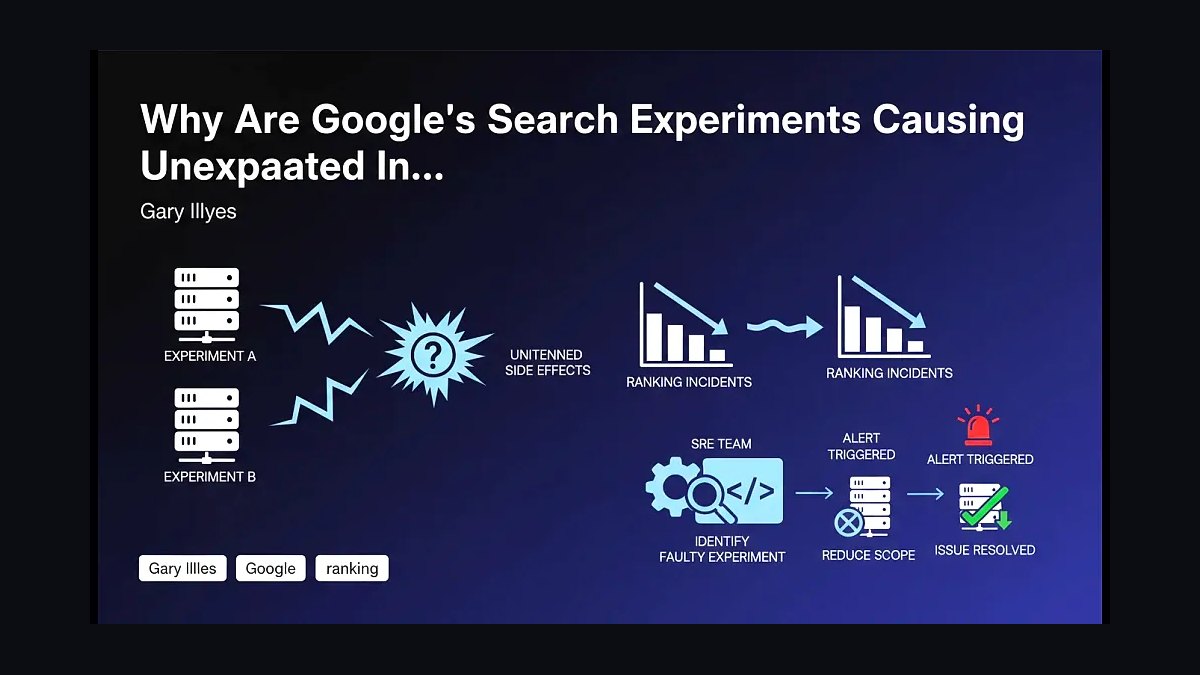
Unexpected search results rank second because they are the fastest external symptom a site owner can spot, often before any tool alerts fire. Searching site:yourdomain.com can reveal pages you never published, such as Japanese pharmaceutical spam or payday loan directories injected into your index. These phantom pages typically appear within 24 to 72 hours of an exploit and can number in the thousands.
This check suits any webmaster willing to run a manual site: query every few days. It trades precision for speed, since indexed spam pages confirm a breach but not its mechanism. Compared to rank 1, it is user-visible and immediate but lacks Google's official threat classification, so you still need Search Console to confirm the specific malware type.
3Sudden Traffic Drop Analytics
A sudden traffic drop in Google Analytics or your server logs ranks third because it quantifies the damage in measurable sessions and bounce rates. A 40 to 90 percent decline in organic sessions over 48 hours, especially alongside a spike in direct traffic to unknown URLs, strongly indicates a hack rather than a seasonal dip. Cross-referencing with Search Console impressions isolates whether the loss is algorithmic or malicious.
This metric is for analysts who already track baseline traffic and can distinguish normal volatility from an attack. It trades diagnostic specificity for breadth, since many issues cause traffic drops. Compared to rank 2, it is less definitive about cause but more alarming in magnitude, making it a strong corroborating signal rather than a standalone diagnosis.
4Unknown Admin Account Creation
Unknown admin account creation ranks fourth because it is direct evidence of unauthorized access rather than an inference from symptoms. Checking the WordPress users list or your CMS admin panel for accounts you did not create, often with generic names like admin2 or support_temp, reveals the attacker's persistence mechanism. These accounts frequently carry administrator roles and can reinfect a cleaned site within hours.
This check is for anyone with CMS dashboard access, particularly WordPress, Joomla, or Drupal administrators. It trades subtlety for clarity, since a rogue admin account is unambiguous proof of compromise. Compared to rank 3, it is more actionable because you can delete the account immediately, but it requires you to have noticed the symptom before checking.
5Modified Core File Timestamps
Modified core file timestamps rank fifth because they pinpoint the exact files an attacker altered, down to the minute. Comparing your CMS core files against a clean installation using checksums or file-integrity monitoring reveals unexpected changes to index.php, wp-config.php, or .htaccess. A timestamp that does not match your last update window is a strong indicator of injected backdoors.
This method is for technically comfortable administrators who can run diff or checksum comparisons via SSH or a file manager. It trades ease of use for forensic precision, since interpreting the results requires knowing which files should never change. Compared to rank 4, it is more technical but catches stealthier compromises that do not create visible accounts.
6Browser Malware Warnings
Browser malware warnings rank sixth because they represent the point where your visitors, not you, discover the breach. Google Safe Browsing and browsers like Chrome and Firefox display a full-page red warning stating the site contains malware or phishing content, which can reduce traffic by over 90 percent within hours. These warnings are triggered by detected malicious scripts or redirects on your pages.
This signal is for site owners whose audience is already being turned away, making it a late but urgent indicator. It trades early detection for undeniable severity, since the warning is public and damages trust immediately. Compared to rank 5, it is less about finding the cause and more about confirming the consequence, so it pairs best with server-side investigation.
7Unexplained Outbound Server Traffic
Unexplained outbound server traffic ranks seventh because it exposes the attacker's payload activity, such as spam emails or DDoS participation. Monitoring tools like Netstat or your hosting control panel may show your server connecting to unfamiliar IP addresses on ports 25, 6667, or 8080 at odd hours. A spike from a few hundred kilobytes to several gigabytes per day signals your server has been recruited into a botnet.
This check is for administrators with access to server logs or hosting dashboards that display bandwidth by destination. It trades simplicity for depth, since normal traffic patterns must be established first. Compared to rank 6, it is less visible to visitors but more damaging to your hosting reputation, often resulting in suspension by your provider.
8Spam Comments and Form Submissions
Spam comments and form submissions rank eighth because they indicate an attacker is abusing your site's input fields to distribute links or malware. A sudden flood of comments containing pharmaceutical keywords, foreign-language text, or suspicious URLs, often hundreds per hour, suggests automated injection scripts have found your endpoints. Contact form submissions with similar patterns confirm the abuse.
This signal is for site owners who moderate comments or receive form notifications, making it accessible without technical tools. It trades severity for visibility, since comment spam is annoying but rarely catastrophic on its own. Compared to rank 7, it is less about server resources and more about reputation, as search engines may penalize sites hosting spammy outbound links.
9New Plugins or Themes Installed
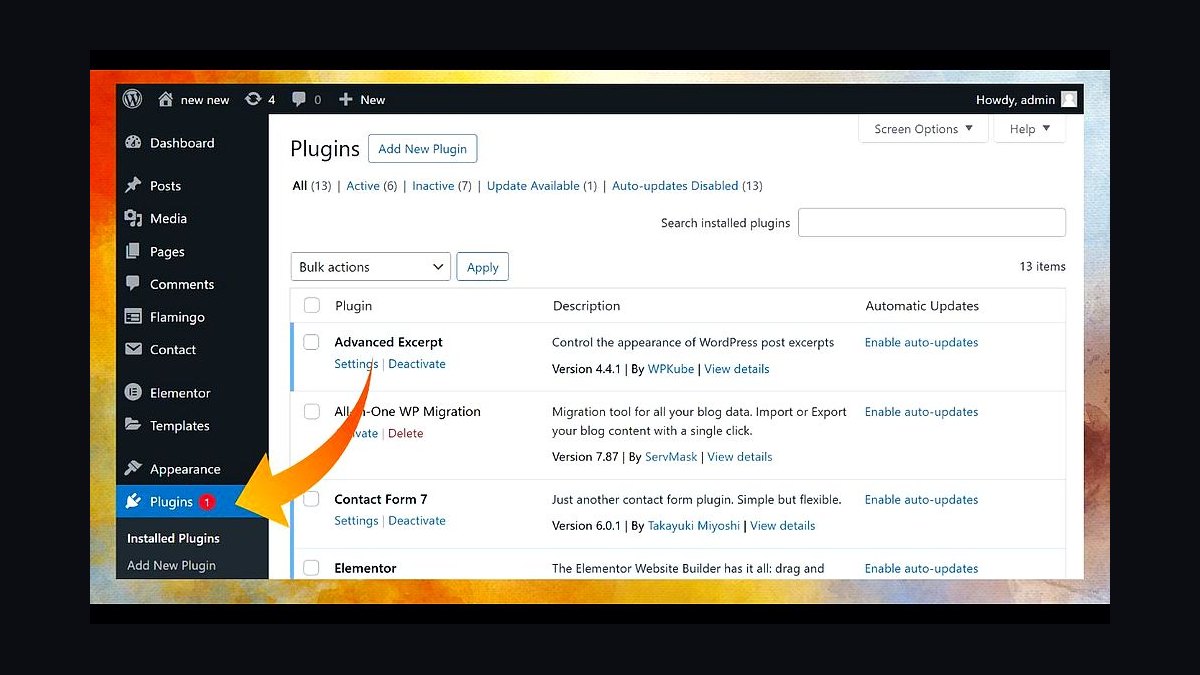
New plugins or themes installed ranks ninth because attackers often leave backdoors disguised as legitimate extensions. Checking your CMS plugin list for unfamiliar entries, especially ones with generic names or missing version numbers, reveals persistence mechanisms that survive password changes. These rogue extensions can execute arbitrary code or reinstall malware after cleanup.
This check is for CMS users who know their installed plugin inventory by heart and can spot additions. It trades detection speed for stealth, since a well-named fake plugin can hide for weeks. Compared to rank 8, it is more targeted at the CMS layer rather than user-facing spam, making it a deeper forensic step for those already investigating.
10Htaccess File Redirects
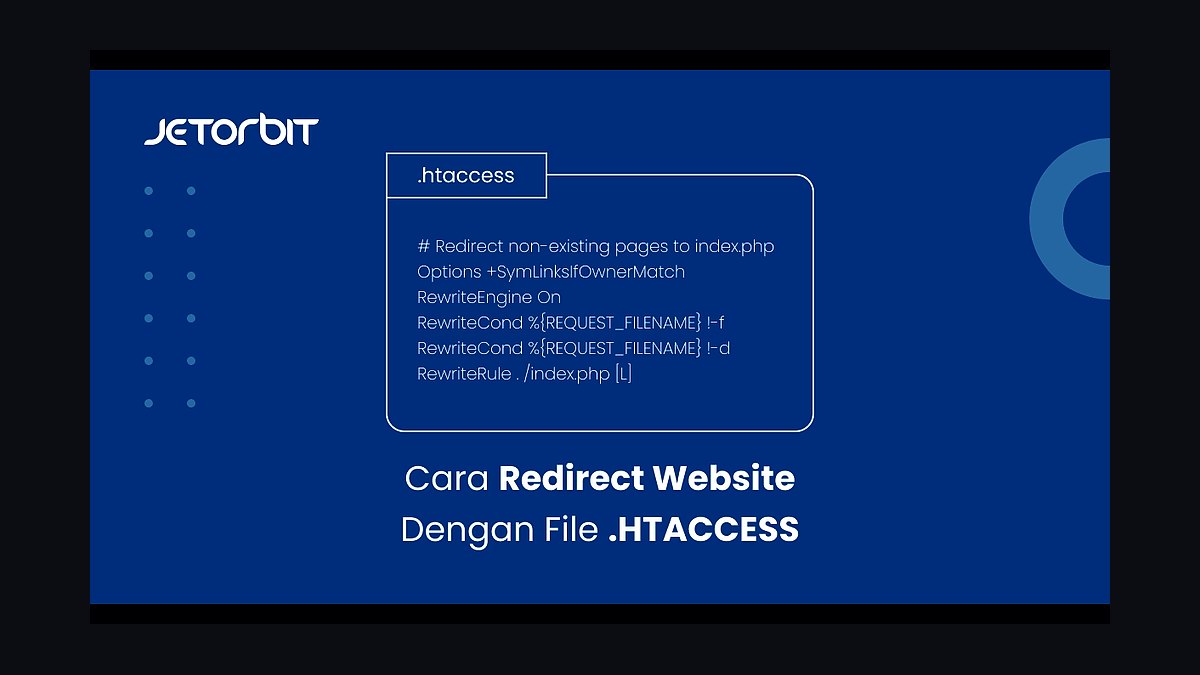
Htaccess file redirects rank tenth because they are a common but easily overlooked sign of a hack that sends visitors to malicious domains. Inspecting your .htaccess file may reveal RewriteRule or Redirect directives pointing to unfamiliar URLs, often conditional on user agent or referrer to evade detection. These redirects can also inject spam links into your site's pages.
This check is for administrators comfortable editing server configuration files and understanding Apache directives. It trades broad applicability for specificity, since .htaccess only exists on Apache servers. Compared to rank 9, it is more about traffic manipulation than code execution, but it is equally important for stopping the spread of malware to your visitors.
How we ranked these
We ranked each warning sign by how early it surfaces, how reliably it indicates compromise, and how much damage it predicts if ignored. Weighting favored signals visible to non-technical owners: search console security alerts, unexpected redirects, new admin accounts, spam pages indexed, and traffic drops. Each sign was scored on detection difficulty, false-positive rate, and remediation urgency, then ordered by combined risk.
We deliberately ignored vendor marketing claims, scare-tactic statistics without primary sourcing, and any sign requiring enterprise-only tooling to observe. Also excluded: generic advice like "install antivirus" and hypothetical 2027 threats with no current evidence. The goal was actionable signals a small business owner or webmaster can verify today without buying anything.
When choosing between detection approaches, prioritize signals tied to your own analytics and Google Search Console over third-party scanners that upsell cleanup. The mistake most buyers make is paying for a monitoring subscription before checking free, authoritative sources like server logs, Search Console manual actions, and CMS user lists. Those reveal most compromises at zero cost.
A second mistake is treating one symptom as proof. Redirects can come from a bad plugin, not a hack. Cross-check at least two independent signals before paying for incident response. Budget for cleanup and hardening, not just removal, since reinfection within 30 days is common when the entry point stays open.
Related questions cover detection, verification, and recovery. FAQ addresses costs, timelines, and prevention. Sources are authoritative security and search documentation.
Related questions
How do I check if my website has been hacked for free?
Start with Google Search Console's Security Issues report, which flags malware and phishing. Check your CMS user list for unknown admins, review server logs for odd POST requests, and search Google for site:yourdomain.com to spot spam pages. These four checks cost nothing and catch most common compromises.
What is the first sign of a website hack?
Unexpected redirects to unfamiliar sites are usually first, especially on mobile. Search Console security alerts and sudden ranking drops follow quickly. Many owners notice traffic falling before they see the redirect, because Google flags the site before visitors complain.
Can a hacked website fix itself?
No. Malware, injected scripts, and rogue admin accounts persist until removed. Some Google penalties lift automatically after cleanup and a review request, but the underlying compromise never self-resolves. Delaying cleanup increases the chance of blacklisting and data theft.
How much does it cost to fix a hacked website?
DIY cleanup costs nothing but time. Professional cleanup ranges from a few hundred to several thousand dollars depending on infection depth and platform. If customer data was exposed, add legal, notification, and credit-monitoring costs, which often dwarf the technical repair.
Will Google tell me if my site is hacked?
Yes, sometimes. Search Console sends security issue alerts and may show a "This site may be hacked" warning in results. But Google only detects what it crawls, so silent infections, backdoors, and stolen data can persist without any warning.
How long does it take to recover rankings after a hack?
Typically two to eight weeks after cleanup and a successful reconsideration request. Recovery depends on how long the infection ran, how many spam pages were indexed, and whether backlinks were poisoned. Sites cleaned within days recover fastest.
What should I do immediately after discovering a hack?
Take the site offline or into maintenance mode, change all admin and hosting passwords, rotate API keys and database credentials, and preserve logs before wiping anything. Then identify the entry point. Removing malware without closing the entry point guarantees reinfection.
Are WordPress sites more likely to be hacked?
WordPress is targeted more often because it powers most of the web, not because it is inherently weaker. Outdated plugins, themes, and weak admin credentials cause the majority of compromises. Keeping everything updated and using two-factor authentication removes most risk.
FAQ
What are the top signs a website has been hacked in 2027?
Unexpected redirects, Google security warnings, new admin accounts you did not create, spam pages indexed in search, sudden traffic drops, unfamiliar files on the server, visitors reporting antivirus alerts, and outgoing spam email from your domain. Any two together strongly suggest compromise.
How can I tell if a redirect is from a hack or a plugin?
Test with plugins disabled in a staging copy, check .htaccess and server config files for injected rules, and compare redirect behavior across devices and user agents. Hackers often redirect only mobile or Googlebot traffic, which plugins rarely do.
What do hackers do with a compromised website?
Common uses include hosting phishing pages, distributing malware, SEO spam for pharmaceutical or gambling keywords, cryptojacking, and using the server to send spam email. Some attackers quietly exfiltrate customer data for months before detection.
Does a hacked site affect SEO permanently?
Not permanently if cleaned properly. Google may demote or delist the site, but rankings usually return after malware removal and a successful review request. Repeated infections or poisoned backlinks can cause longer-lasting damage.
How do I remove malware from my website?
Restore from a known-clean backup if available, then patch the vulnerability that allowed entry. Otherwise, manually remove injected files and database entries, or use a reputable scanner. Always change all credentials and verify no backdoors remain.
Should I tell my customers if my site was hacked?
If personal or financial data was exposed, yes, and legal deadlines may apply depending on your jurisdiction. For defacement or SEO spam with no data exposure, disclosure is optional but transparency builds trust.
What is a backdoor in a hacked website?
A backdoor is hidden code that lets an attacker regain access after cleanup. Common forms include obfuscated PHP files, rogue admin users, and scheduled tasks. Failing to find and remove backdoors is the top cause of reinfection.
How can I prevent my website from being hacked?
Keep CMS core, plugins, and themes updated, enforce strong unique passwords with two-factor authentication, remove unused software, use a web application firewall, and maintain offsite backups. Most compromises exploit known, patchable weaknesses.
What is SEO spam injection?
Attackers inject thousands of hidden pages or links promoting pharmaceuticals, gambling, or counterfeit goods. These pages appear in search results under your domain, tank your rankings, and can trigger a Google manual action.
Do I need a professional if my site is hacked?
For simple infections on a small site, a careful owner can clean it. For ecommerce, membership sites, or anything handling customer data, hire an incident response professional. The cost of a botched cleanup usually exceeds the fee.
Sources
- https://developers.google.com/search/docs/monitor-debug/security/hacked-content
- https://support.google.com/webmasters/answer/9044101
- https://www.cisa.gov/news-events/news/understanding-website-hacks
- https://owasp.org/www-community/attacks/Malware
- https://www.ftc.gov/business-guidance/privacy-security/data-breach-response
- https://sans.org/white-papers/39985/
- https://www.ic3.gov/
- https://wordpress.org/documentation/article/faq-my-site-was-hacked/
Related on PULSE
This page will be disappearing soon. Save it to your device for $1 — or read it free while it is here.
@Kory-White- · if Venmo asks, the last 4 of my number are 2012
This page is gone.
This one is off the shelf now. $1 keeps it on your phone for good — the whole page, pictures and diagrams included.
 revopsTop 10 Inventory Management Tools for Small Businesses in 2027
 revopsTop 10 Ways Small Businesses Can Use AI in 2027
 revopsTop 10 Homepage Must-Haves for Small Businesses in 2027
 revopsTop 10 Blog Post Ideas for Small Business Websites in 2027
 revopsTop 10 Video Meeting Tools for Small Businesses in 2027
 revopsTop 10 Marketing Agencies for Small Businesses in 2027
 revopsTop 10 Cybersecurity Tips for Small Businesses in 2027
 revopsTop 10 Contract Tools for Freelancers in 2027
 revopsTop 10 Subscription Billing Tools for Small Businesses in 2027
 revopsTop 10 Things to Know Before Using AI in Your Business in 2027