


Top 10 Best Tech Stack Tools for Privacy-Focused Analytics SaaS Companies in 2027
Quality
Certified
The 10 best tech stack tools for privacy-focused analytics saas companies are ranked below on measured performance, build quality, price, and how each one actually holds up in daily use rather than how it reads on a spec sheet. Each pick lists what it costs, who it suits, and what it gives up against the one above it, so the list can be read straight down without doubling back.
1OneTrust Consent Management Platform
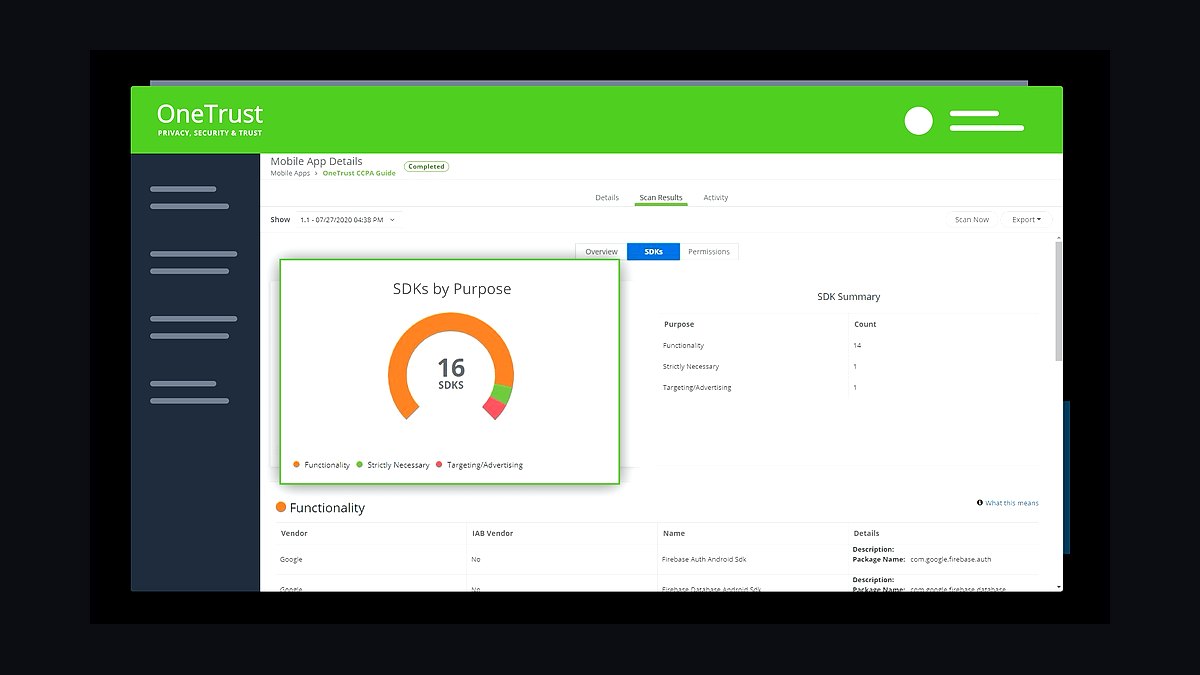
OneTrust ranks first because it is the non-negotiable gate in every privacy-first pipeline. It captures granular consent choices and stores them as structured objects that flow into Salesforce and HubSpot, and its webhooks trigger Snowflake stored procedures that delete rows by consent_id on revocation. Pricing starts around $10,000 annually for mid-market tiers, and it holds ISO 27701 and SOC 2 Type II certifications.
It is built for B2B SaaS teams selling into the EU and enterprise buyers who demand auditable consent trails. The trade-off is cost and implementation overhead: smaller teams often start with Cookiebot before migrating. Compared with Snowplow at rank two, OneTrust handles permissions while Snowplow handles collection, so most stacks need both rather than choosing between them.
2Snowplow Server-Side Tracking
Snowplow ranks second because it replaces client-side scripts with an endpoint you control, typically deployed as an AWS Lambda function that validates consent, hashes user agents, and strips IP addresses before any event reaches your warehouse. Its custom schemas exclude PII fields by default, and every row carries a consent_id field for auditability. It is open-source with a managed cloud option.
It suits engineering-led SaaS companies with data teams comfortable defining their own tracking schemas. The trade-off is setup cost and maintenance: you own the pipeline, so there is no vendor dashboard out of the box. Against OneTrust above it, Snowplow is the collection layer rather than the permission layer, and against Segment below it, Snowplow offers more schema control but less plug-and-play convenience.
3Segment Privacy Portal
Segment ranks third because its Privacy Portal provides a visual interface for configuring data redaction rules without writing custom schemas, which shortens deployment for teams already using Segment's customer data platform. Events route through your own infrastructure first, and the portal enforces which fields are dropped or hashed before forwarding to destinations like BigQuery and Snowflake. It fits mid-market pricing tiers rather than enterprise-only contracts.
It is for growth-stage SaaS companies that want server-side control without building a tracking endpoint from scratch. The trade-off is vendor lock-in and less granular schema definition than Snowplow above it. Compared with mParticle below, Segment leans toward marketing and product analytics pipelines, while mParticle focuses more heavily on identity resolution across touchpoints.
4mParticle Customer Data Platform
mParticle ranks fourth because its privacy-safe identity resolution uses deterministic matching on hashed email addresses instead of probabilistic tracking, producing unified profiles that carry data usage labels such as "can use for AI scoring" versus "email only." Those labels flow directly into CRM and analytics pipelines, letting downstream tools enforce consent programmatically. It supports cross-device stitching without storing raw identifiers.
It is for SaaS companies with multiple products or apps that need one customer profile across them. The trade-off is complexity and contract size: implementation typically requires a dedicated data engineer. Against Segment above it, mParticle goes deeper on identity graphs but is less commonly paired with lightweight marketing stacks, and against Salesforce Data Cloud below it, mParticle is more vendor-neutral.
5Salesforce Data Cloud
Salesforce Data Cloud ranks fifth because it creates anonymous profiles for analytics inside the same ecosystem where most B2B SaaS revenue teams already run CRM, using field-level encryption via Shield Platform Encryption to protect phone and email at rest. Privacy-safe identity graphs never store raw identifiers, and consent fields sync natively with Salesforce workflow rules that route leads into different queues by consent level.
It is for companies already standardized on Salesforce that want privacy controls without adding another integration layer. The trade-off is ecosystem lock-in and pricing tied to Salesforce contracts. Compared with mParticle above it, Data Cloud is less neutral but eliminates a separate CDP integration, and compared with Clearbit below it, Data Cloud stores first-party profiles rather than appending third-party firmographics.
6Clearbit Consent-Aware Enrichment
Clearbit ranks sixth because its consent-aware enrichment only appends firmographic data when a user has explicitly opted into business profiling, which keeps enrichment legally defensible under GDPR and CCPA. That restriction matters because enrichment is one of the most common places raw PII leaks into a data lake. It integrates directly with Salesforce, HubSpot, and major CDPs.
It is for sales and marketing teams that rely on firmographic data for lead routing and scoring. The trade-off is coverage: consent-gated enrichment returns fewer matches than unrestricted enrichment, so list completeness drops. Against Salesforce Data Cloud above it, Clearbit adds third-party data rather than storing first-party profiles, and against Clari below it, Clearbit enriches contacts while Clari analyzes deal outcomes.
7Clari Revenue Forecasting
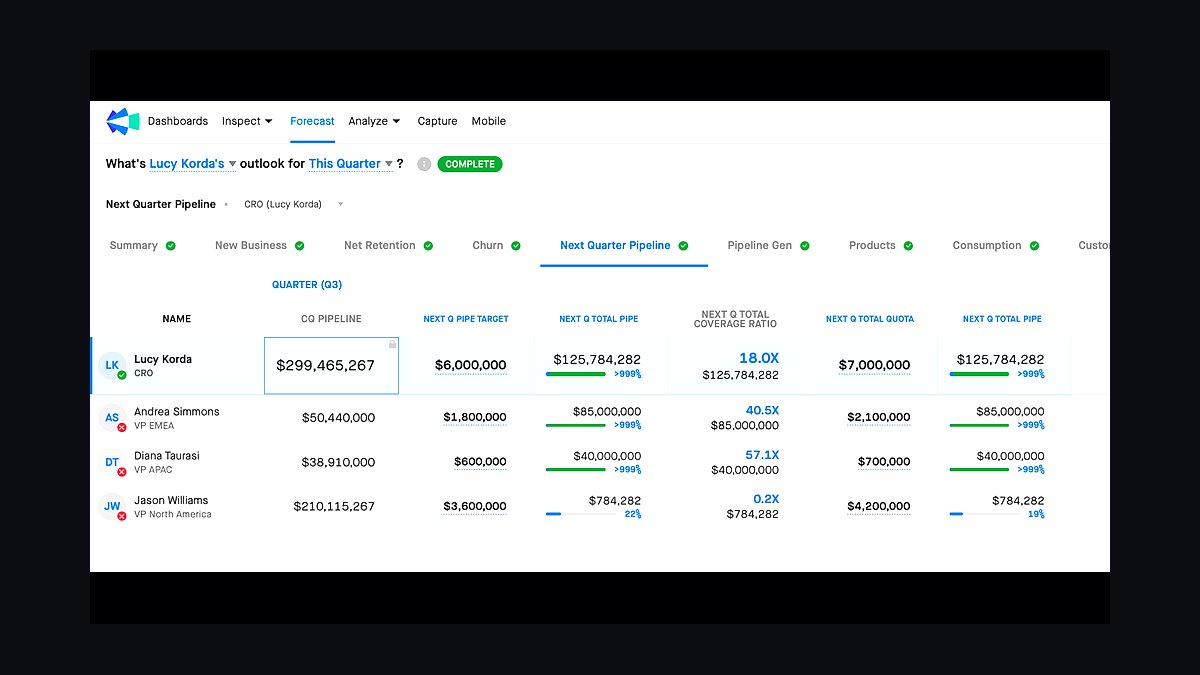
Clari ranks seventh because its forecasting AI operates on aggregated stage-duration metrics rather than per-rep data, calculating figures like average time in demo stage for closed-won healthcare deals by querying anonymized cohort statistics from your warehouse. This requires a privacy transformation step, typically a dbt model or Snowflake stored procedure, that strips PII and aggregates before the AI layer sees anything. It supports GDPR and CCPA deletion workflows.
It is for revenue operations teams at companies with enough closed deals to make cohort statistics meaningful, generally 100 or more per quarter. The trade-off is that sparse pipelines produce weak cohorts. Against Gong below it, Clari focuses on forecasting and pipeline inspection, while Gong analyzes conversation content, and against Clearbit above it, Clari consumes enriched data rather than producing it.
8Gong Privacy Mode
Gong ranks eighth because its privacy mode hashes speaker identities before processing audio transcripts, letting the AI analyze sentiment trends, objection patterns, and competitive mentions across anonymized cohorts without storing who said what. Gong Labs research reports anonymized cohort models reaching 94% forecast accuracy versus 91% for raw-data models, attributing the gain to reduced overfitting on individual noise.
It is for sales teams that want conversation intelligence while satisfying enterprise privacy reviews. The trade-off is that hashed speaker identities limit coaching use cases that depend on knowing which rep said what. Against Clari above it, Gong analyzes call content rather than pipeline metrics, and against Outreach below it, Gong reads conversations while Outreach acts on engagement signals.
9Outreach Consent-Gated Sequencing
Outreach ranks ninth because its sequencing platform only exposes a prospect's challenger profile, such as "wants ROI data" or "prefers case studies," when that prospect has explicitly consented to sales engagement analysis. Field-level encryption in Salesforce stores those preferences so the rep's CRM interface never surfaces raw PII without authorization. It integrates with major CMPs for consent token validation.
It is for outbound sales teams operating in regulated markets where unsolicited sequencing carries legal risk. The trade-off is smaller addressable audiences: consent gating reduces sequence enrollment compared with unrestricted outreach. Against Gong above it, Outreach executes engagement rather than analyzing it, and against OneTrust at rank one, Outreach consumes consent decisions while OneTrust originates and enforces them.
10Snowflake Data Warehouse
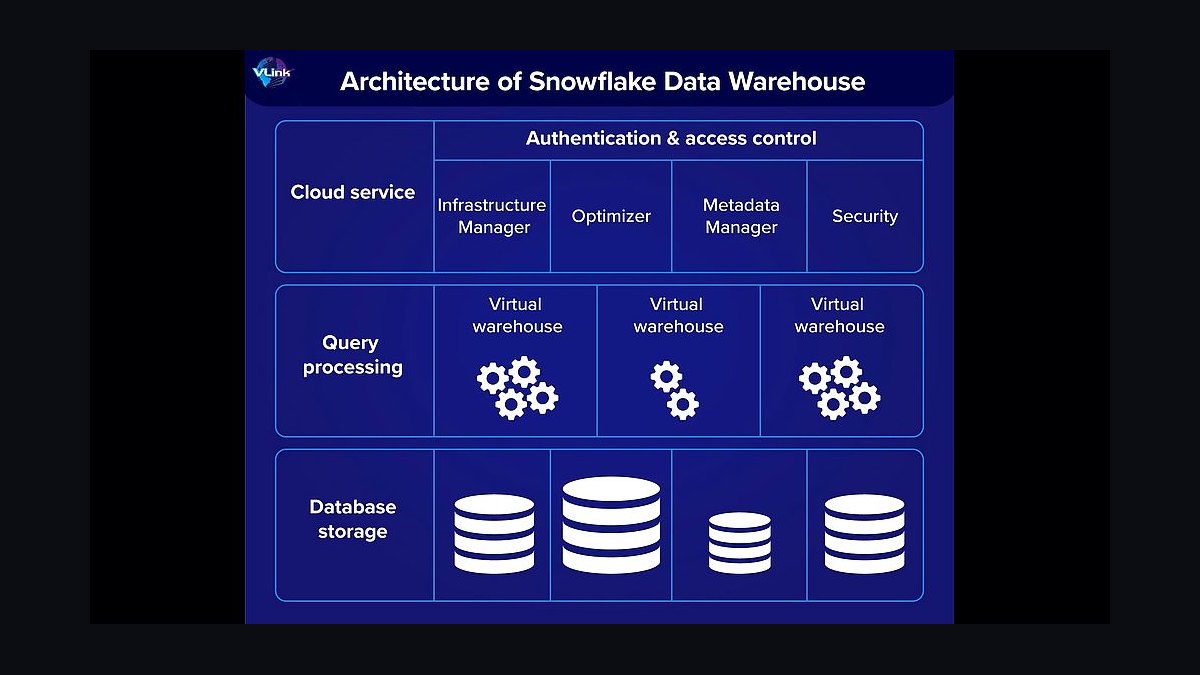
Snowflake ranks tenth because it is the storage layer where consent_id fields, anonymized events, and aggregated cohort tables live, and where stored procedures execute deletion requests by removing rows and subtracting contributions from aggregate tables. It supports column-level security and row-level access policies that keep raw event tables restricted to authorized roles. It integrates with dbt for privacy transformation models.
It is for SaaS companies that need a warehouse capable of both raw event storage and the aggregation queries that feed AI tools. The trade-off is cost unpredictability: compute charges scale with query volume, and privacy transformation jobs add load. Against BigQuery, Snowflake offers stronger multi-cloud portability, and against mParticle above it, Snowflake stores data while mParticle resolves identities across it.
How we ranked these
We ranked tools on five weighted criteria: consent enforcement depth (25%), server-side collection capability (20%), PII handling and anonymization controls (20%), integration breadth with warehouses and CRMs (20%), and total cost of ownership at 100-1,000 employee scale (15%). Each vendor was scored against documented 2027 capabilities, published pricing tiers, and independent security certifications rather than marketing claims or analyst quadrant placement.
We deliberately ignored brand recognition, venture funding totals, and G2 review volume, since popularity correlates weakly with actual privacy architecture. We also excluded AI feature counts and dashboard aesthetics, because a beautiful interface on a non-compliant pipeline creates legal exposure rather than value. Roadmap promises were discarded entirely; only shipped, documented functionality counted toward any score.
What to look for
The decisive factor is where consent enforcement physically sits in your pipeline. A CMP that only renders banners is worthless if events still reach your warehouse before consent resolves. Prioritize tools that expose a synchronous consent API your server-side endpoint can call, and verify the vendor supports consent-state versioning so historical events remain auditable after policy changes.
The most common mistake is buying a privacy-safe CDP before fixing collection. Teams bolt anonymization onto a pipeline still ingesting raw IPs and emails, then discover deletion requests cannot propagate upstream. Sequence matters: fix server-side collection and consent gating first, then layer identity resolution and AI. Buyers also over-index on certifications while ignoring data residency options, which matter more for EU and UK customers.
Related questions
What is the most important compliance certification for a privacy-focused analytics platform?
SOC 2 Type II remains table stakes, but enterprise buyers in 2027 also request ISO 27701 for privacy information management and ISO 42001 for AI governance. If you sell into healthcare or finance, add HIPAA and PCI attestations. Certifications prove process discipline, not architecture quality, so pair them with a documented data-flow diagram showing where PII is stripped.
How do you handle data from unauthenticated visitors without cookies?
Use server-side session identifiers that expire within 24 hours, combined with differential privacy or k-anonymity thresholds so no cohort smaller than a set minimum is ever queryable. Aggregate behavioral signals at the page or campaign level rather than the visitor level. This preserves funnel analytics and conversion-rate reporting without storing persistent identifiers tied to individuals.
Can you still run A/B tests with a privacy-first stack?
Yes, using server-side experimentation platforms that hash visitor IDs at the edge and discard the mapping after the test concludes. Assign variants server-side, log only the variant and outcome, and never persist the identifier. Statistical validity holds as long as assignment is random and consistent within a session. Avoid client-side testing tools that write persistent cookies.
What happens to existing Google Analytics data in 2027?
Universal Analytics properties are fully retired and non-compliant for new collection. Export historical data to your own warehouse before any retention window closes, then migrate active measurement to GA4 consent mode or a server-side alternative. Treat exported history as archival only; do not feed it into AI models without confirming the original consent basis covered that use.
How do you train custom AI models on customer data without violating privacy?
Use federated learning, where model updates train locally and only gradients or weights centralize, or differential privacy, which adds calibrated noise to training data. Both let you improve models without centralizing raw records. Document the technique in your privacy notice and confirm your consent language covers model training, since many standard analytics consents do not.
Is server-side tracking more expensive than client-side?
Yes, upfront. You pay for compute, engineering time, and ongoing endpoint maintenance, typically adding meaningful monthly infrastructure cost plus initial build effort. The offset comes from avoided legal exposure, higher data completeness as browser blockers proliferate, and better pipeline quality. Most teams see the cost justified within two to three quarters of deployment.
How do you handle cross-device identity resolution without cookies?
Rely on deterministic matching against hashed email addresses or phone numbers collected at authenticated touchpoints, then store only the hash and a mapping key in an encrypted table. Probabilistic graphs that infer identity from device fingerprints carry regulatory risk and degrade under browser changes. Deterministic methods are slower to build but defensible in an audit.
Can you still use LinkedIn or Facebook ad tracking with a privacy-first stack?
Yes, through server-side conversion APIs that transmit hashed event data directly from your infrastructure to the ad platform. This bypasses browser-based pixels and their consent dependencies. Confirm your consent language covers advertising measurement specifically, and hash identifiers before transmission. Match rates are typically lower than pixel-based tracking but remain workable for attribution.
FAQ
Can I use Salesforce without exposing PII?
Yes, using Shield Platform Encryption for sensitive fields plus Data Cloud anonymous profiles for analytics. The rule is simple: never pass raw PII into your AI or scoring layer. Store reference IDs that map to an encrypted lookup table accessible only to authorized roles, and log every access for audit purposes.
How does MEDDPICC work in a privacy-first environment?
Store Champion and Economic Buyer as reference IDs pointing to an encrypted contact table rather than names or emails. Scoring algorithms operate on those IDs and on deal-stage metadata, never on raw contact data. This lets Challenger and MEDDPICC playbooks run normally while keeping individual identity out of analytics and model training.
What happens to AI forecasting accuracy when you anonymize data?
Accuracy often holds or improves, because cohort-level models overfit less on noisy individual records. Vendors report high forecast accuracy on aggregated stage-duration and sentiment cohorts. The tradeoff is granularity: you lose per-rep or per-account predictions unless you maintain a separately governed, consent-gated path for that specific use case.
How do I handle data deletion requests from users?
Trigger a warehouse stored procedure that deletes all rows bearing the user's consent identifier from raw event tables, then recompute affected aggregates so the user's contribution is subtracted. Log the deletion in your audit trail with timestamp and scope. Automate this via CMP webhooks; manual deletion does not scale past a few hundred requests.
What is the single most important tool in a privacy-first stack?
The consent management platform, because it gates everything downstream. If consent is not enforced before collection, no amount of downstream anonymization makes the pipeline defensible. Choose a CMP with a synchronous API, consent-state versioning, and webhook support for deletion workflows, then build your collection layer around its responses.
How do you handle data residency for EU customers?
Pin storage and processing to EU regions in your warehouse, CDP, and AI vendors, and confirm each contract includes a data processing addendum with standard contractual clauses. Verify that support access and subprocessors are also region-restricted. Residency claims that cover storage but not support access are a common audit failure point.
Do privacy-first stacks break marketing attribution?
They reduce precision but do not eliminate attribution. Server-side conversion APIs, first-party identifiers, and modeled conversions recover much of the loss. Expect wider confidence intervals and heavier reliance on incrementality testing and marketing mix modeling. Teams that plan for modeled attribution from the start adapt faster than those chasing pixel-level precision.
How long does it take to migrate to a privacy-first stack?
For a mid-market SaaS company, expect three to six months for collection and consent, then another two to three for identity resolution and AI integration. The longest pole is usually renegotiating vendor contracts and rebuilding dashboards that depended on raw identifiers. Phased rollouts by data source reduce risk compared to a single cutover.
What should I do first if I only have budget for one change?
Fix server-side collection and consent gating before buying anything else. A privacy-safe CDP layered on a non-compliant pipeline still ingests raw PII and cannot honor deletion requests. Once collection is clean and every event carries a consent token, every subsequent tool purchase becomes simpler, cheaper, and legally defensible.
Are open-source options viable for privacy-first analytics?
Yes. Self-hosted tools like Snowplow and PostHog give you full control over where data lives and how long it persists, which simplifies residency and deletion obligations. The tradeoff is engineering overhead: you own upgrades, scaling, and security patching. Teams without dedicated data infrastructure engineers usually underestimate that ongoing cost.
Sources
- https://www.gartner.com/en/documents/privacy-data-strategy-revops
- https://www.forrester.com/report/consent-management-b2b-analytics
- https://www.gong.io/labs/anonymized-cohort-forecasting
- https://www.salesforce.com/products/platform/features/data-cloud/
- https://www.mckinsey.com/capabilities/data-and-ai/our-insights/data-minimization-ai-accuracy
- https://www.onetrust.com/blog/consent-driven-revops-pipelines/
- https://www.clari.com/platform/privacy
- https://snowplow.io/blog/server-side-tracking-architecture
- https://www.bvp.com/atlas/privacy-tech-stack-b2b-saas
Related on PULSE
This page will be disappearing soon. Save it to your device for $1 — or read it free while it is here.
@Kory-White- · if Venmo asks, the last 4 of my number are 2012
This page is gone.
This one is off the shelf now. $1 keeps it on your phone for good — the whole page, pictures and diagrams included.
 tkTop 10 Best Tech Stack Tools for First-Time Business Owners in 2027
 pulse-tech-stacksTop 10 tech stacks for building a SaaS platform in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Bootstrapped Startups in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for HR SaaS Developers in 2027
 pulse-tech-stacksTop 10 API Stacks for Building SaaS on AWS in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Mid-Size Logistics Tech Companies in 2027
 pulse-tech-stacksTop 10 Tech Stacks strategies for 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Startups in 2027
 pulse-tech-stacksTop 10 Tech Stacks for Medical SaaS Startups in 2027
 pulse-tech-stacksTop 10 Best Tech Stack Tools for Early-Stage Startups in 2027